Resources
White Papers
Design and Evaluation of DLP AI Models for Multilingual Sensitive Data Detection
A technical account of multilingual sensitive-data detection: dataset design, lightweight risk screening, precise extraction, the correction of character-offset errors, and comparative model evaluation.
ACP Lab Notes
[Part 1] After a Breach, How Far Can an Attacker Go? — Why I Want to Try ACP Firsthand
Recent security incident reports keep bringing me back to the same question: ‘If an attacker is already inside, what can we still stop?’

Blog
[Part 2] ISO/IEC 42001 — Where Do I Even Start? What Comes First?
This article introduces a practical approach to identifying AI assets, building an AI inventory, and evolving it into an AI Control Tower from the perspective of ISO/IEC 42001.
July 31, 2026
Blog
What is an FDE (Forward Deployed Engineer)? Explaining the new engineer role gaining attention in the generative AI era
This article explains the meaning, role, background of attention, required skills, and differences from IT consultants and SES of an FDE (Forward Deployed Engineer) in an easy-to-understand manner.
July 23, 2026
Blog
[Part 1] ISO/IEC 42001 — Where Do I Even Start? What Comes First?
A practical starting guide for ISO/IEC 42001 certification, covering the standard's perspective, scope definition, and stakeholder identification before building an AI management system.
July 12, 2026
Introduction Decks
QueryPie AIP Introduction
Everything You Need to Know About QueryPie AIP
ACP Lab Notes
[Part 2] Installing QueryPie ACP Community Edition — A First Lab Environment for Evaluating Adoption
To explore what can be controlled after an intrusion, I installed QueryPie ACP Community Edition on my Mac. This first lab records the installation steps, issues encountered, and the checks completed before testing access policies.
Manuals
QueryPie AIP Manual
A guide page for the QueryPie AIP user guide, feature usage, and operating flow.
Introduction Decks
QueryPie ACP Introduction
Everything You Need to Know About QueryPie ACP
ACP Lab Notes
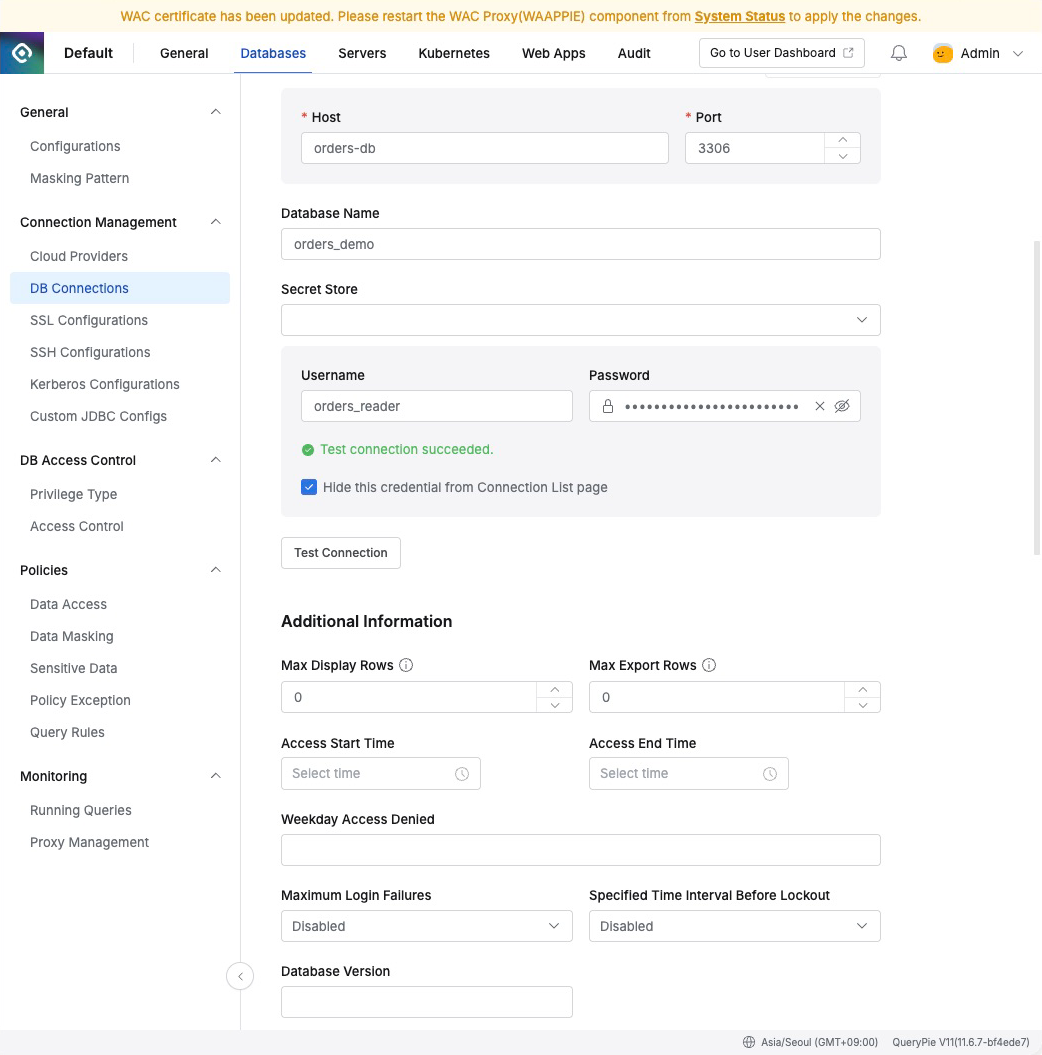
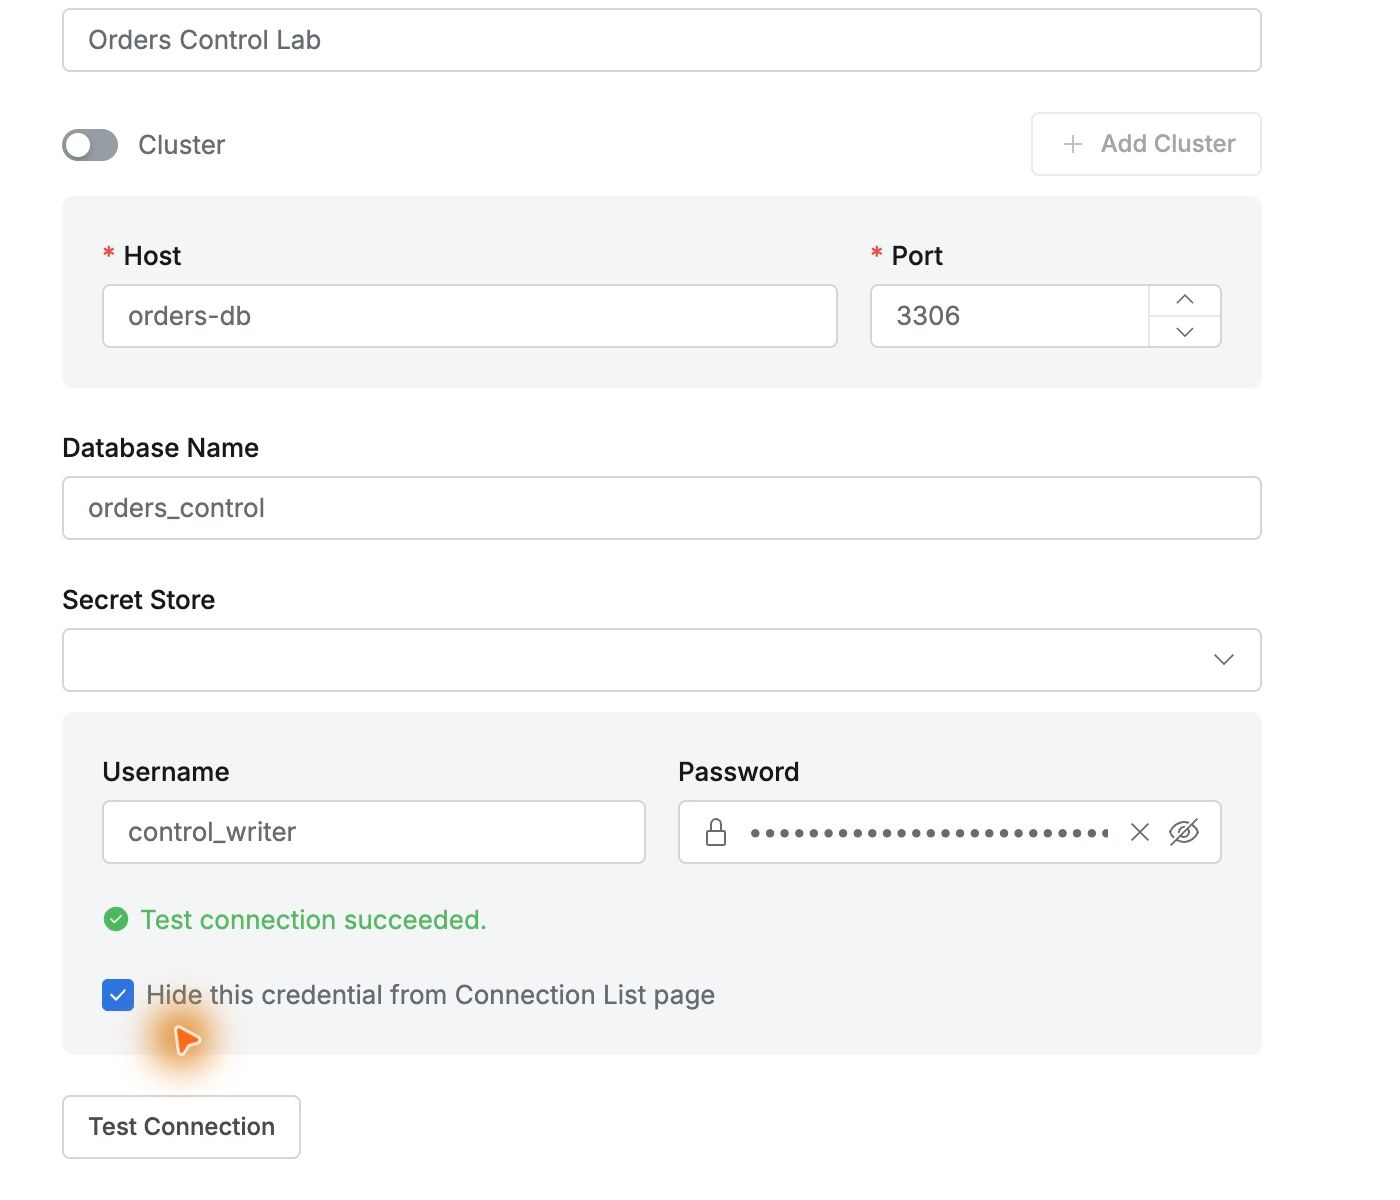
[Part 3] Connecting the First Database to QueryPie ACP — What Changes for Developers?
In Part 2, I installed QueryPie ACP Community Edition on my Mac and signed in. Now I want to connect a database and query real test data. What interested me was the developer experience: once an administrator registers a database, where does a developer run SQL? Is access limited to the browser, or can an existing database client be used?
Blog
AI Work OS: How a new intelligence works within an enterprise
Now that AI has become a new intelligence working alongside humans within enterprises, organizations need context that AI can understand, an execution structure to perform actual tasks, and an operational system to safely control that execution.
June 16, 2026
Manuals
QueryPie ACP Manual
A guide page that brings together administrator and user documentation for QueryPie ACP.
White Papers
The End of SaaS, or Its Evolution? — Strategies SaaS Companies Must Adopt in the Age of AI Agents
This white paper analyzes the impact of AI agents on the SaaS business, outlines the strategies SaaS companies should adopt, and shares the real story of QueryPie AI's transformation from a SaaS vendor to an AI-native company.
ACP Lab Notes
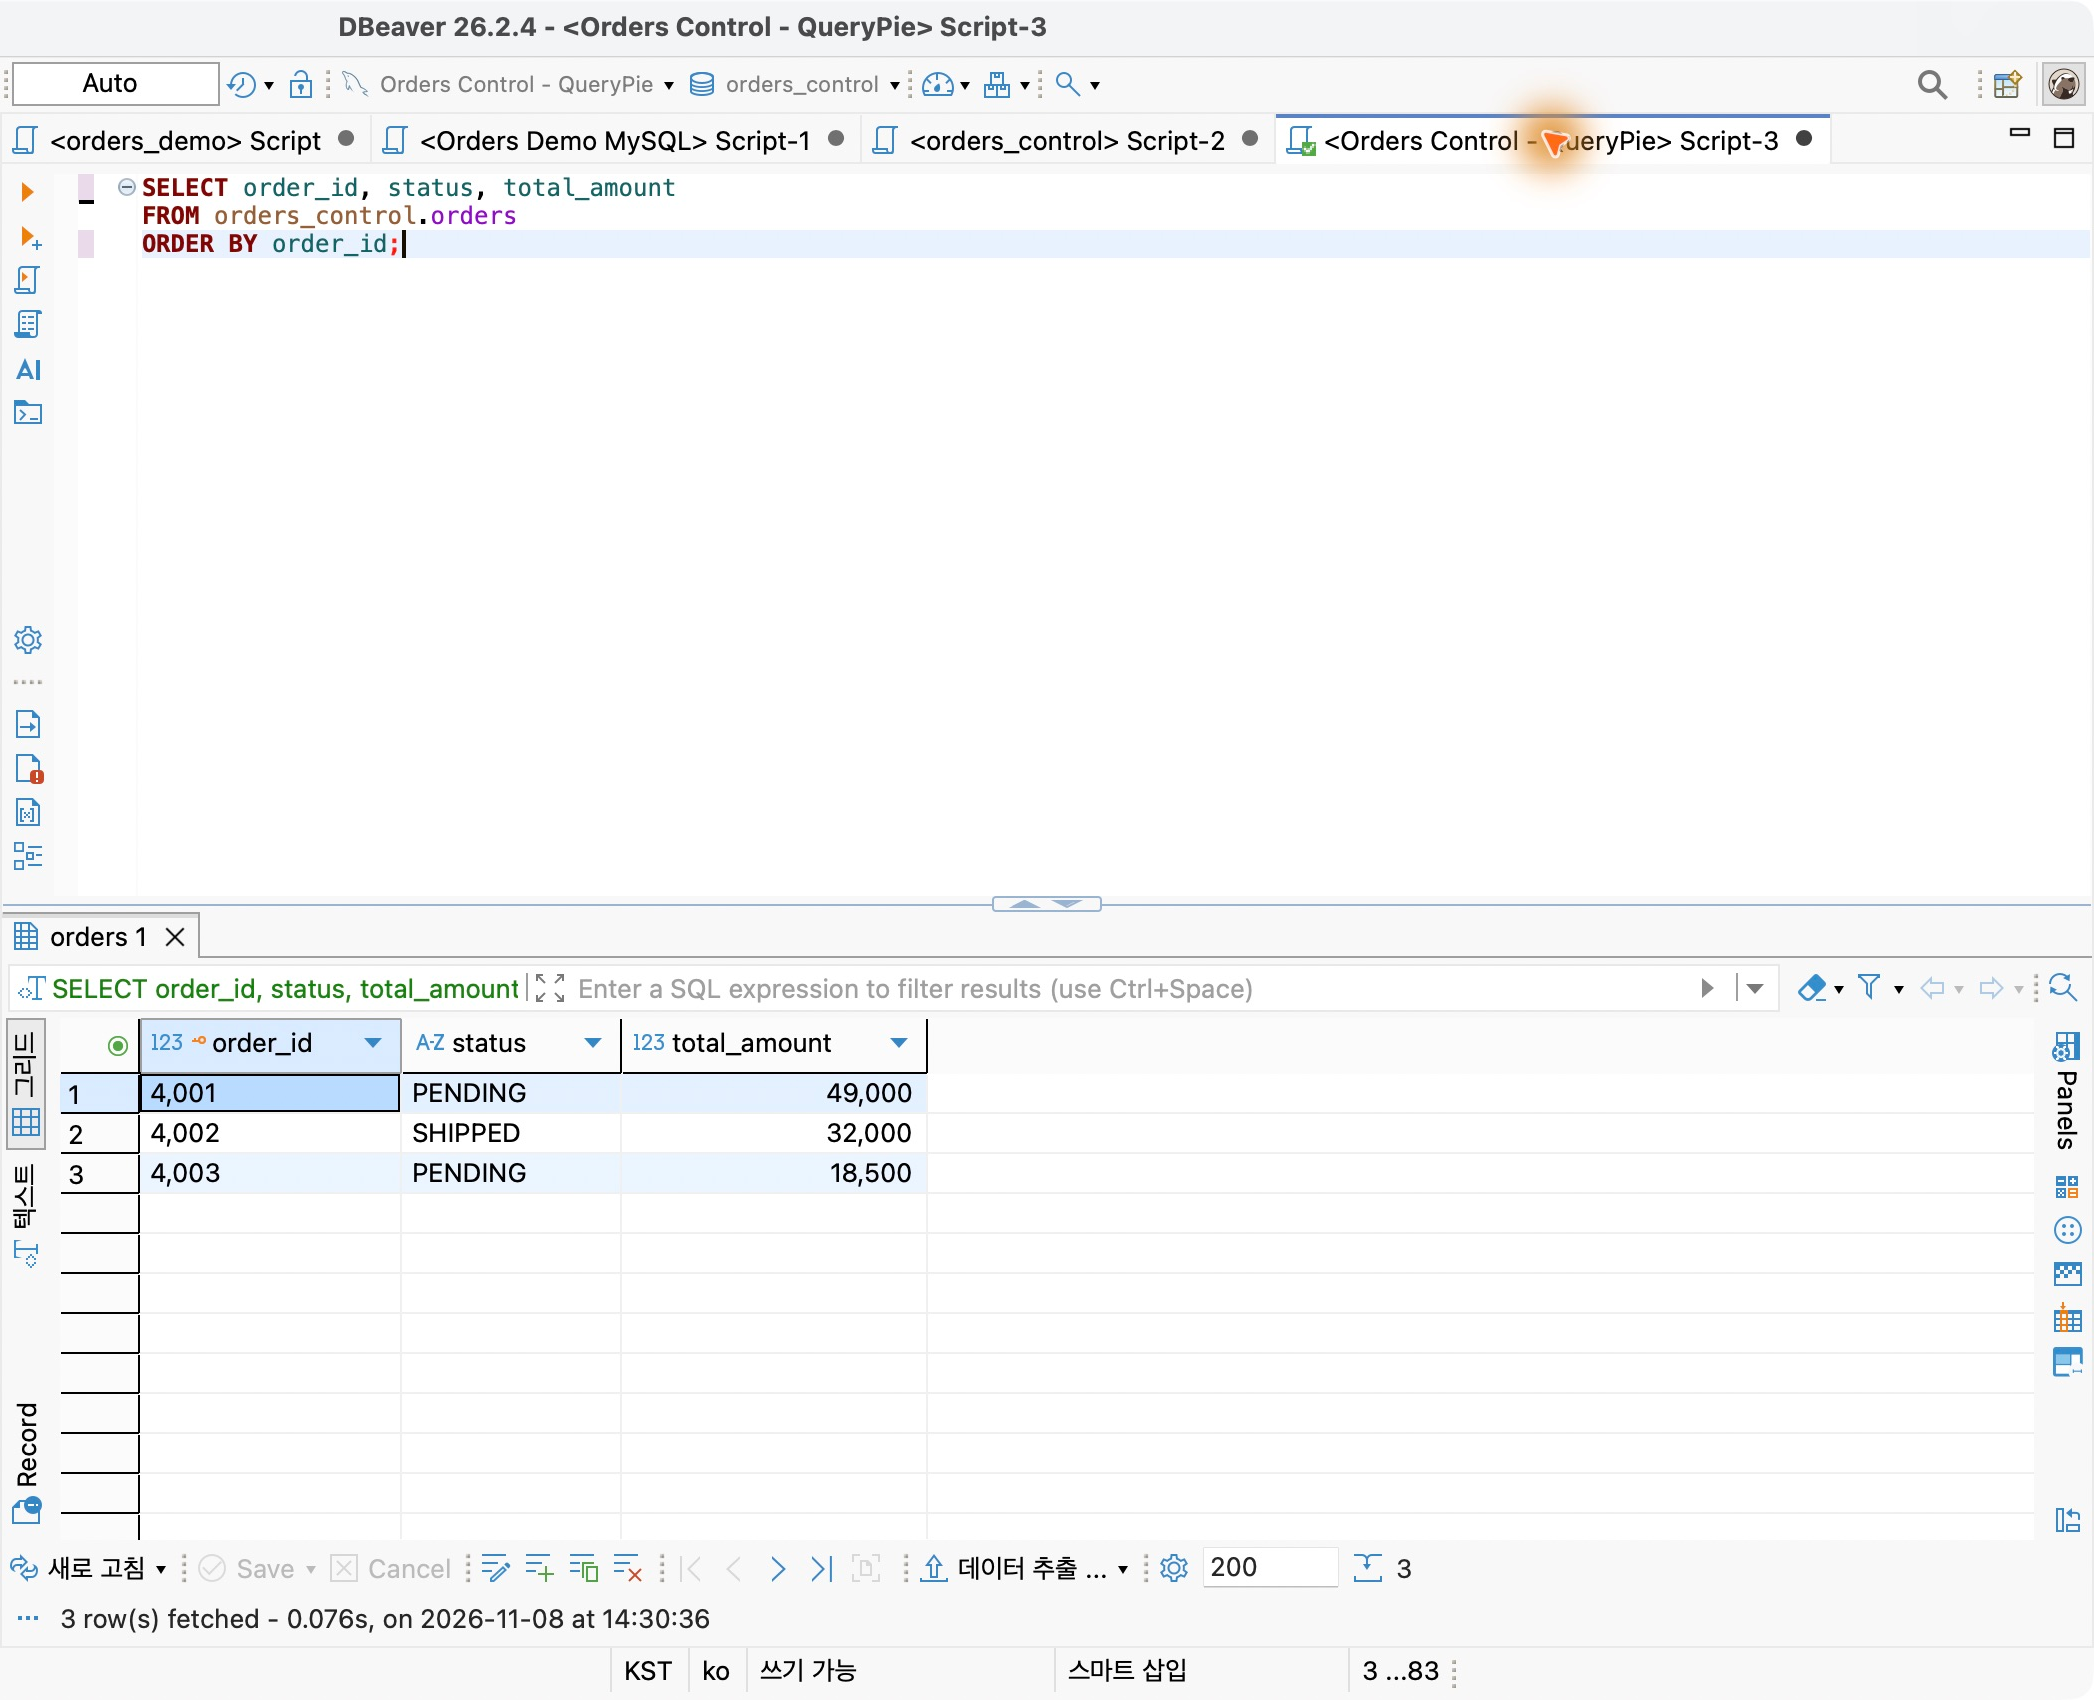
[Part 4] Running UPDATE with QueryPie ACP Read-Only Access — Blocking Queries, Revoking Access, and Reviewing Audits
Previously, I registered a database in QueryPie and queried orders in DBeaver, both with manual connection settings and Multi Agent. With reads working, I wanted to try the opposite: what happens when a read-only developer runs UPDATE, or an administrator revokes access?
Manuals
QueryPie ACP User Manual
A guide page for basic user operations and day-to-day QueryPie usage.
White Papers
Guardrail Design in the AI Agent Era (2026 Edition) — Part 1: Philosophy & Design
As AI agents move from conversational assistants to autonomous executors, enterprises need stronger control systems. This 2026 guide explains a four-element guardrail framework—Permission, Approval, Audit Trail, and Kill Switch—for CxOs and operational leaders.
ACP Lab Notes
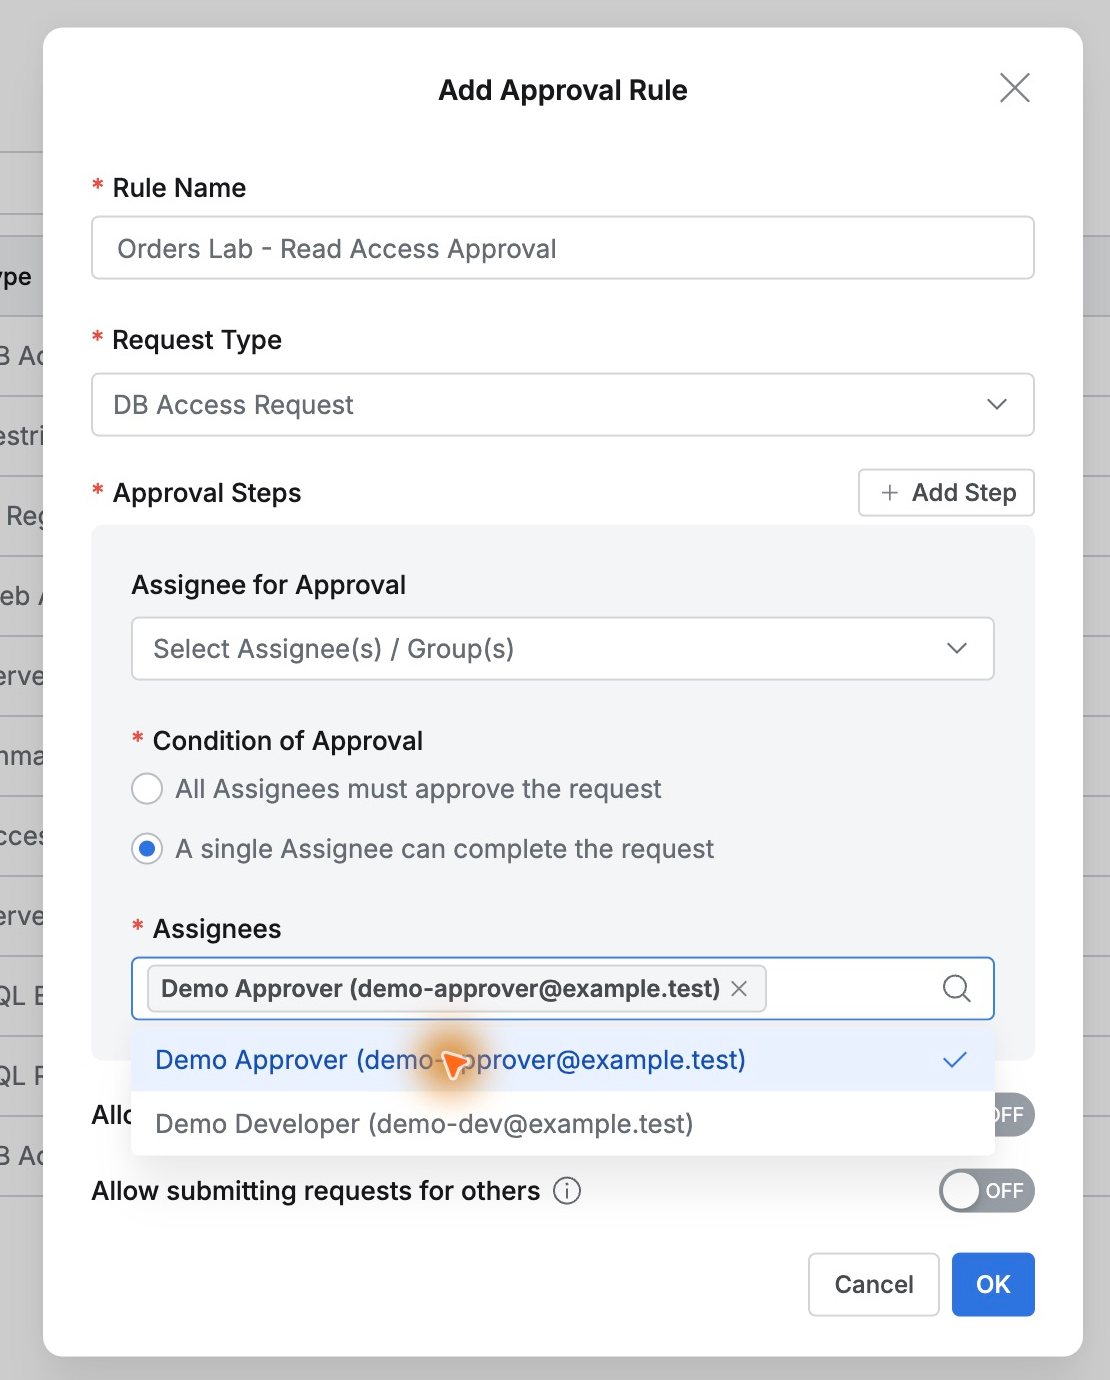
[Part 5] Requesting and Approving Database Access in QueryPie ACP — Through to Queries in DBeaver
‘I need to check order settlements. Could I have read access to the database until tomorrow?’ Database operators often receive requests like this. They need to establish which database, what privileges, and how long access is needed; as teams grow, recording who received access and why becomes important.
Manuals
QueryPie ACP Administrator Manual
A guide page for administrator setup, operations, and permission management procedures.
Blog
AI Attack Tools Breach 600 Firewalls Across 55 Countries: How to Protect the Data Beyond the Firewall
An AI-powered open-source attack platform breached 600+ FortiGate firewalls across 55 countries. An unskilled threat actor leveraged AI to execute attacks at scale. This article analyzes the CyberStrikeAI incident and presents a defense-in-depth framework for CxOs to protect data beyond the firewall.
March 9, 2026
White Papers
Guardrail Design in the AI Agent Era (2026 Edition) — Part 2: Practice & Implementation
A practical implementation guide for AI-agent guardrails. Includes three case studies (PC-operation agents, development AI vulnerabilities, and autonomous 5G operations), a reusable checklist, and a 90-day rollout roadmap.
ACP Lab Notes
[Part 6] Approving SQL and Updating Data in QueryPie ACP — Keeping Read Access, Authorizing Only the Task
While querying a production database, sometimes one or two records need correcting: an order may still show an old status after delivery, or an incorrect value needs fixing. Even a simple production change should clearly record who changed it and why. After access approval in Part 5, this time I tried SQL approval.
Manuals
QueryPie ACP Release Notes
A guide page for checking the latest product updates, added features, and improvements.
Blog
AI Security Threat Map 2026 | 7 Attack Vectors and Practical Defense Framework for CxOs
AI security is not an extension of traditional cybersecurity—it requires an additional defense layer. Explore 7 AI-specific attack vectors including prompt injection and model supply chain threats, with an OWASP and NIST-aligned governance framework for CxOs.
March 3, 2026
White Papers
Comparative Evaluation of LLMs for a Domain-Specific Pipeline Focused on Code Generation and Agentic RAG [Part 1]
Do not blindly trust LLM benchmarks. Evaluate and select the LLM best suited to your domain yourself. This is the first part of a study that systematically compares 13 LLM configurations on a real Japanese payroll-system pipeline.
Glossary
QueryPie AI Glossary - Key Terms and Definitions
Access QueryPie AI's glossary of key terms related to data governance and security. Learn essential terminology for understanding our platform and the industry.
ACP Lab Notes
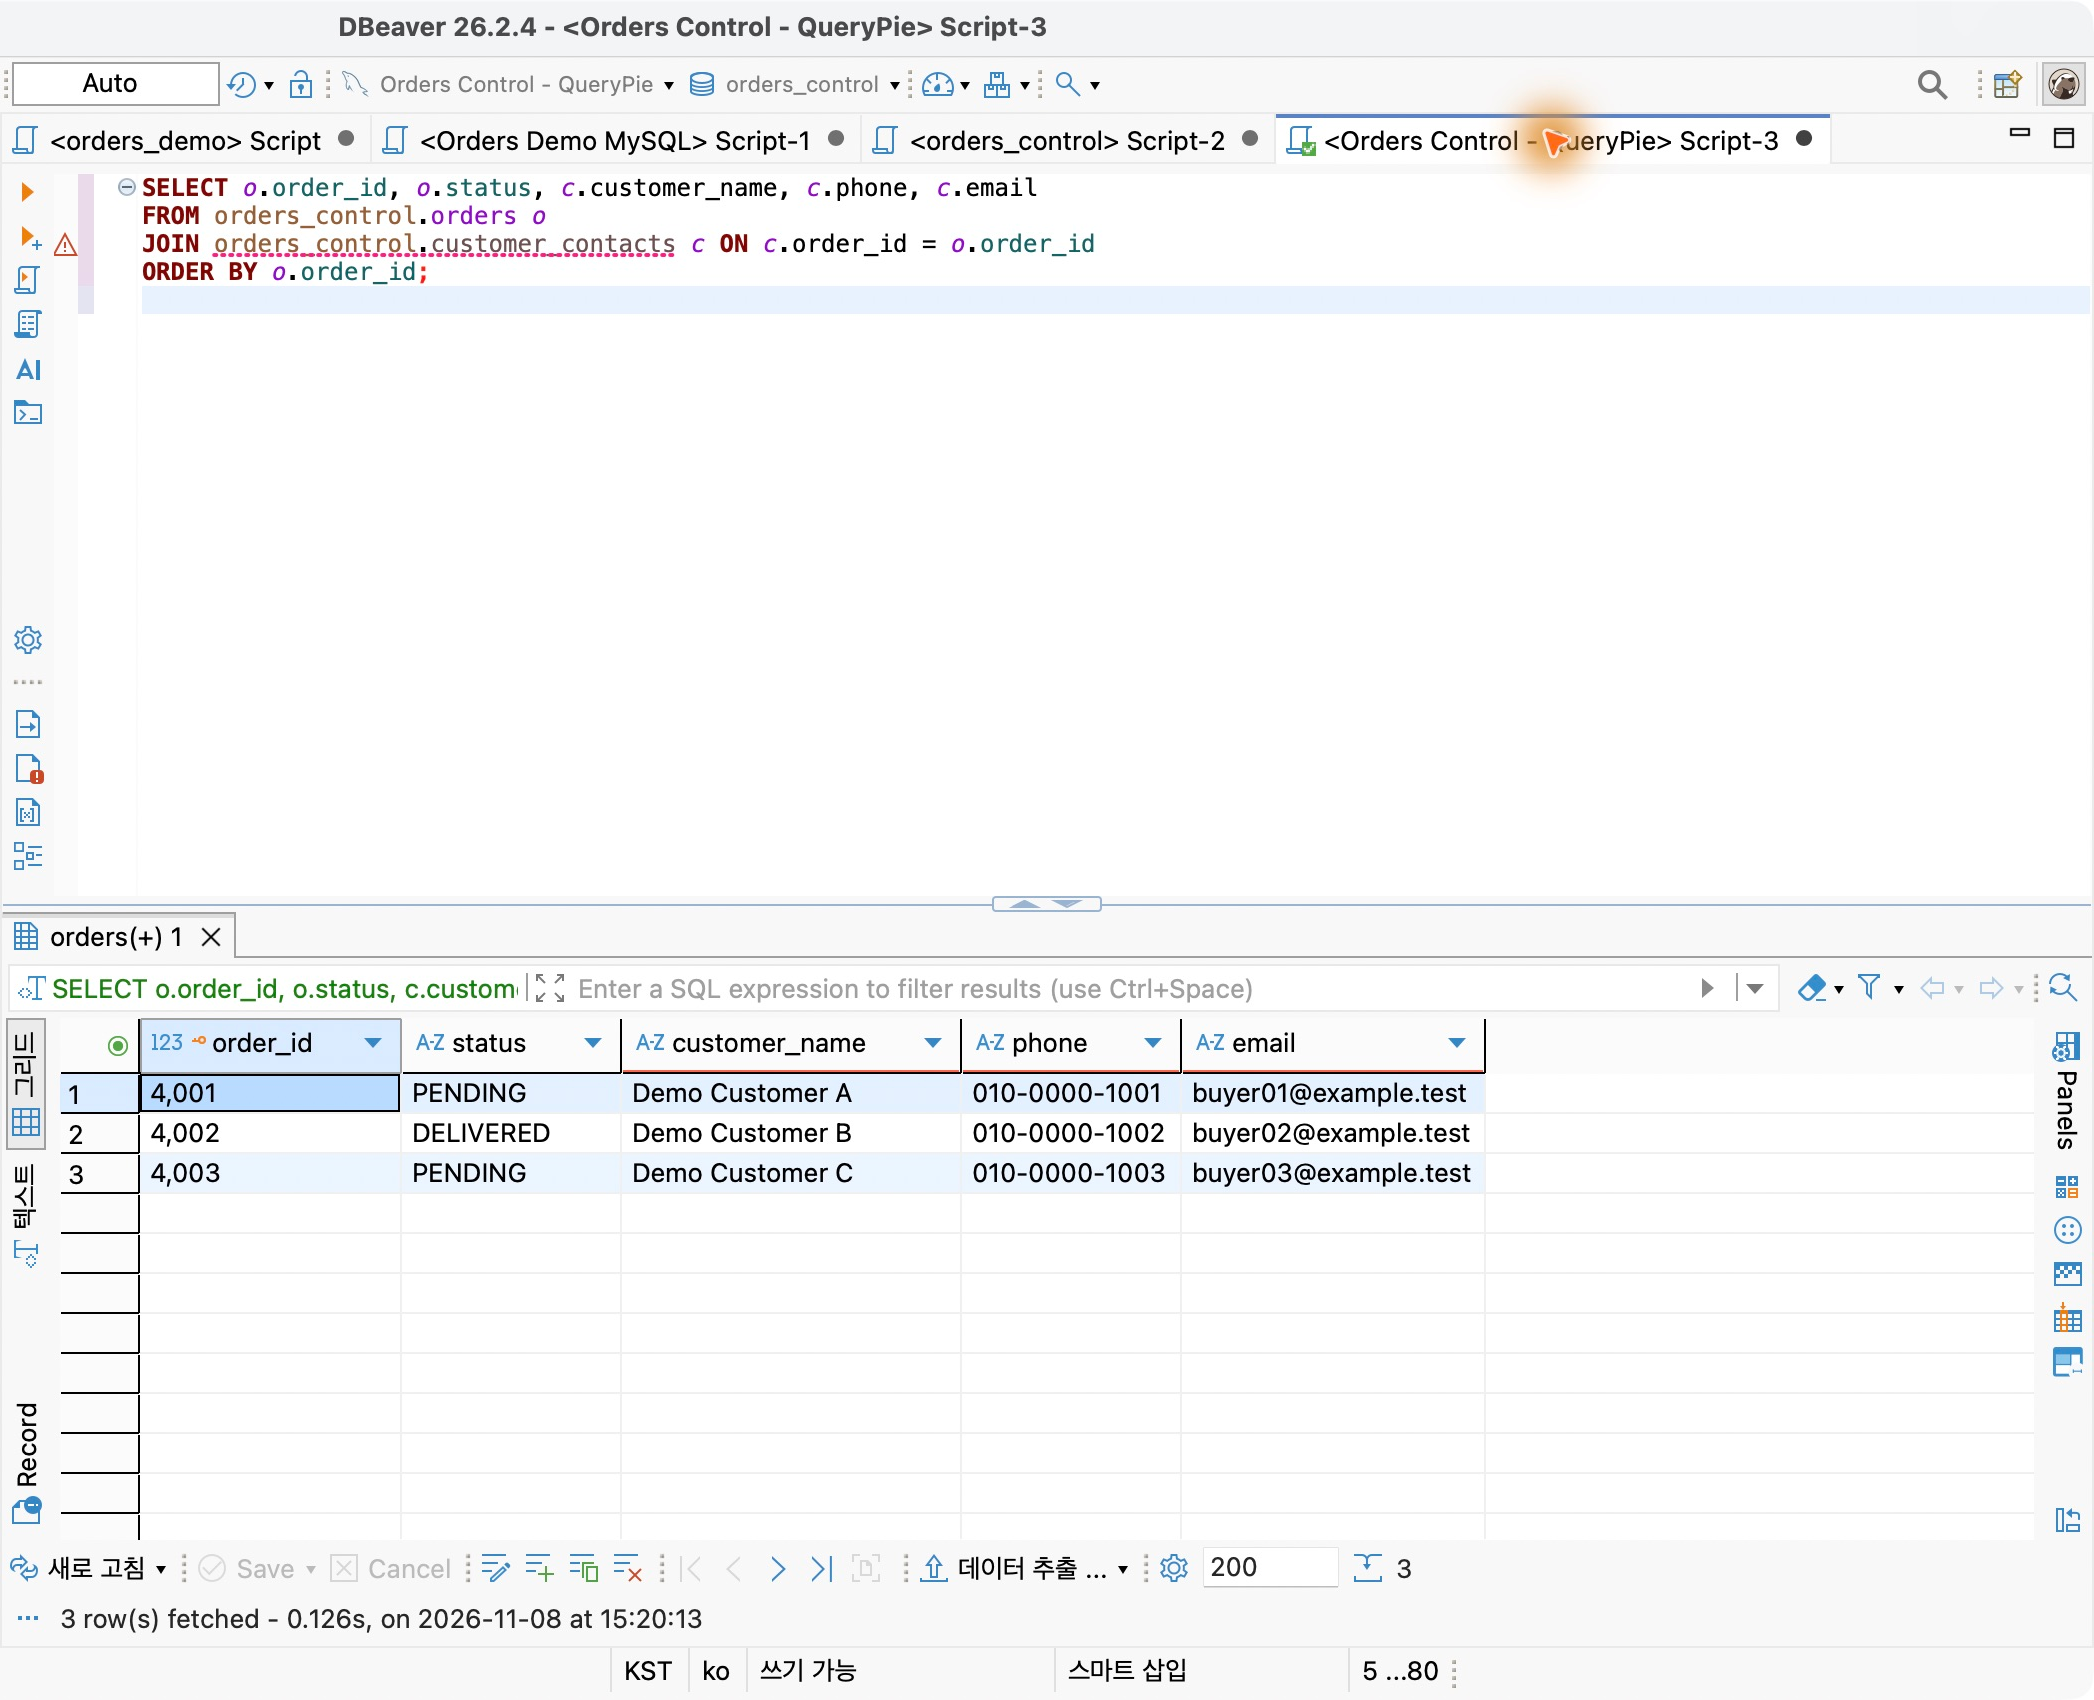
[Part 7] Allowing Database Queries While Hiding Personal Data — QueryPie Data Masking in Practice
In Part 6, I changed only necessary data through approved SQL while keeping read access. Now I wanted to control what query results reveal. Checking delivery status does not always require the customer’s full phone number and email, but blocking order queries altogether is not practical either.
Manuals
QueryPie ACP OpenAPI Reference
A guide that collects entry points to the QueryPie ACP OpenAPI Reference and related developer resources.
Blog
[2026 Update] The Full Scope of Shadow AI Risk: 5 CxO Actions to Prevent Data Leaks and Compliance Violations
Shadow AI is now a board-level business risk. IBM reports that breaches linked to shadow AI cost an average of $4.63M. This article explains five concrete actions for CxOs to prevent data leakage, compliance failures, and NDA violations, backed by the latest data.
February 20, 2026
White Papers
Comparative Evaluation of LLMs for a Domain-Specific Pipeline Focused on Code Generation and Agentic RAG [Part 2]
We present a comprehensive analysis of experimental results across 13 LLM configurations. We reveal unexpected pitfalls in "Thinking" mode, stability issues with GPT, and the optimal pipeline setup that achieves a 60% cost reduction.
ACP Lab Notes
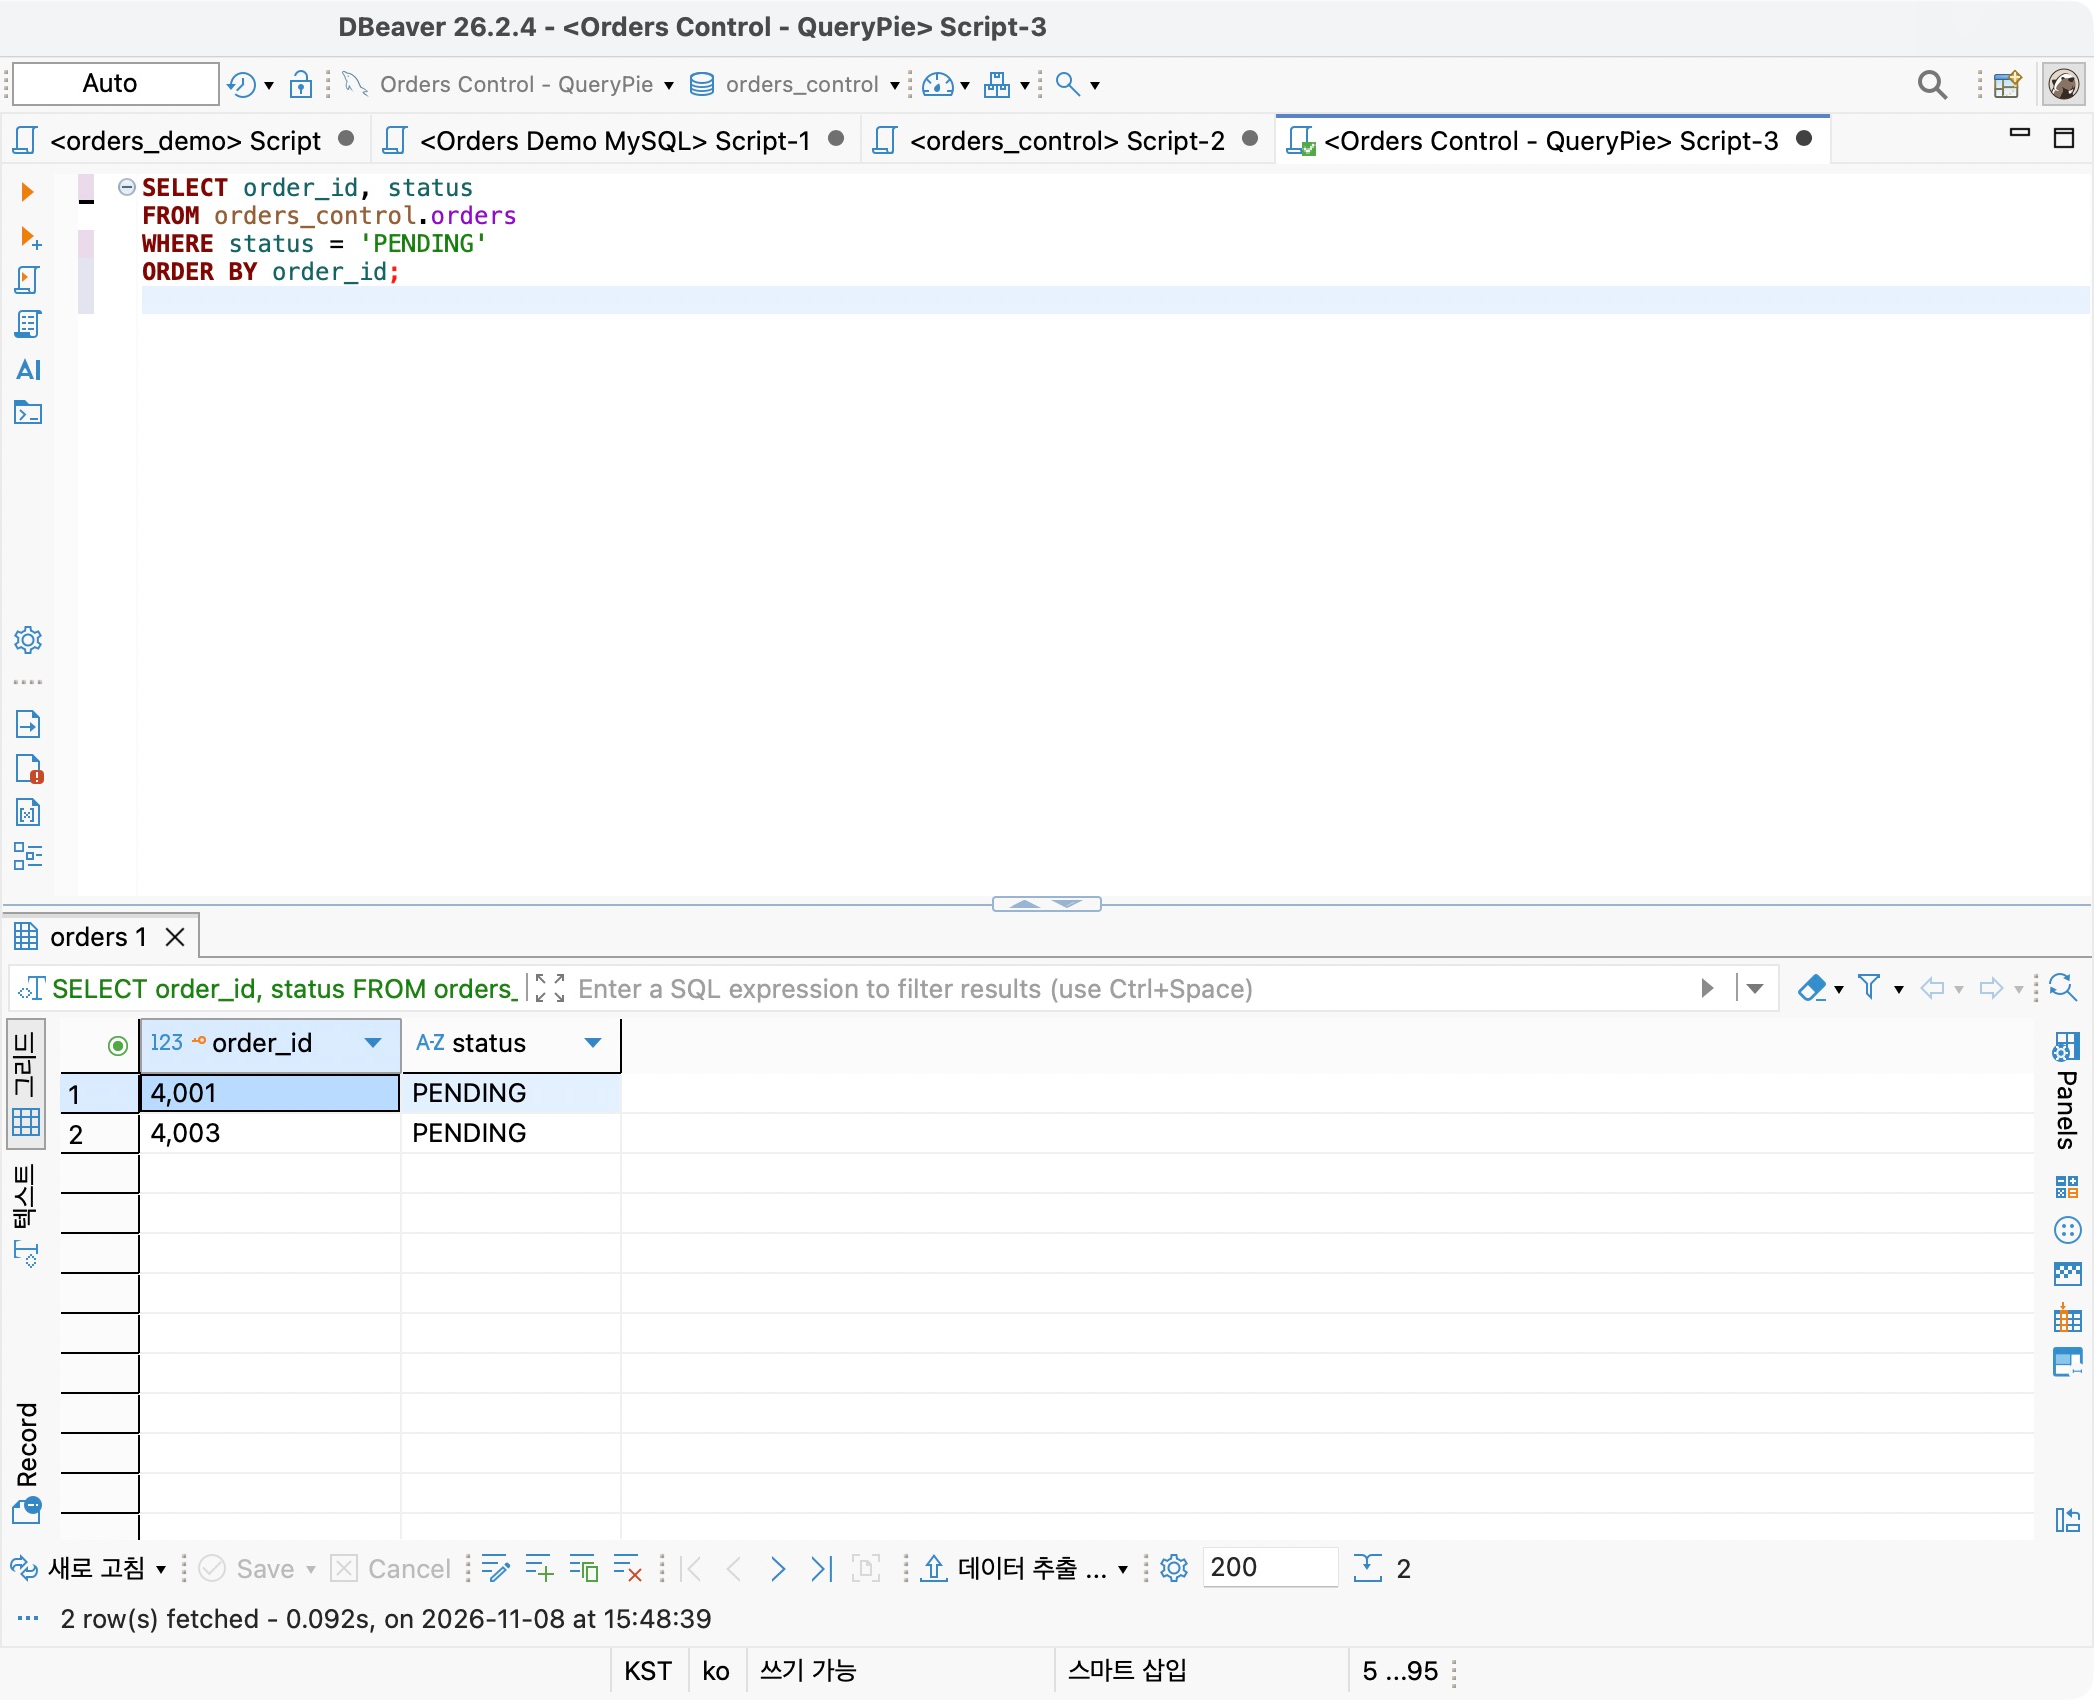
[Part 8] Who Queried Customer Information? — Tracing Database Activity with QueryPie Audit Logs
Part 7 masked phone numbers and emails for developers, with exceptions for staff needing original values. Now suppose someone asks who queried order 4002 after a delivery inquiry. Where should an administrator look, and what can the records tell us?
White Papers
Why Japanese Enterprises Are Accelerating Their AI Transformation Now
A concise, executive guide that diagnoses Japan’s AI gaps and delivers a pragmatic roadmap to turn AI into enterprise-wide productivity and growth.
ACP Lab Notes
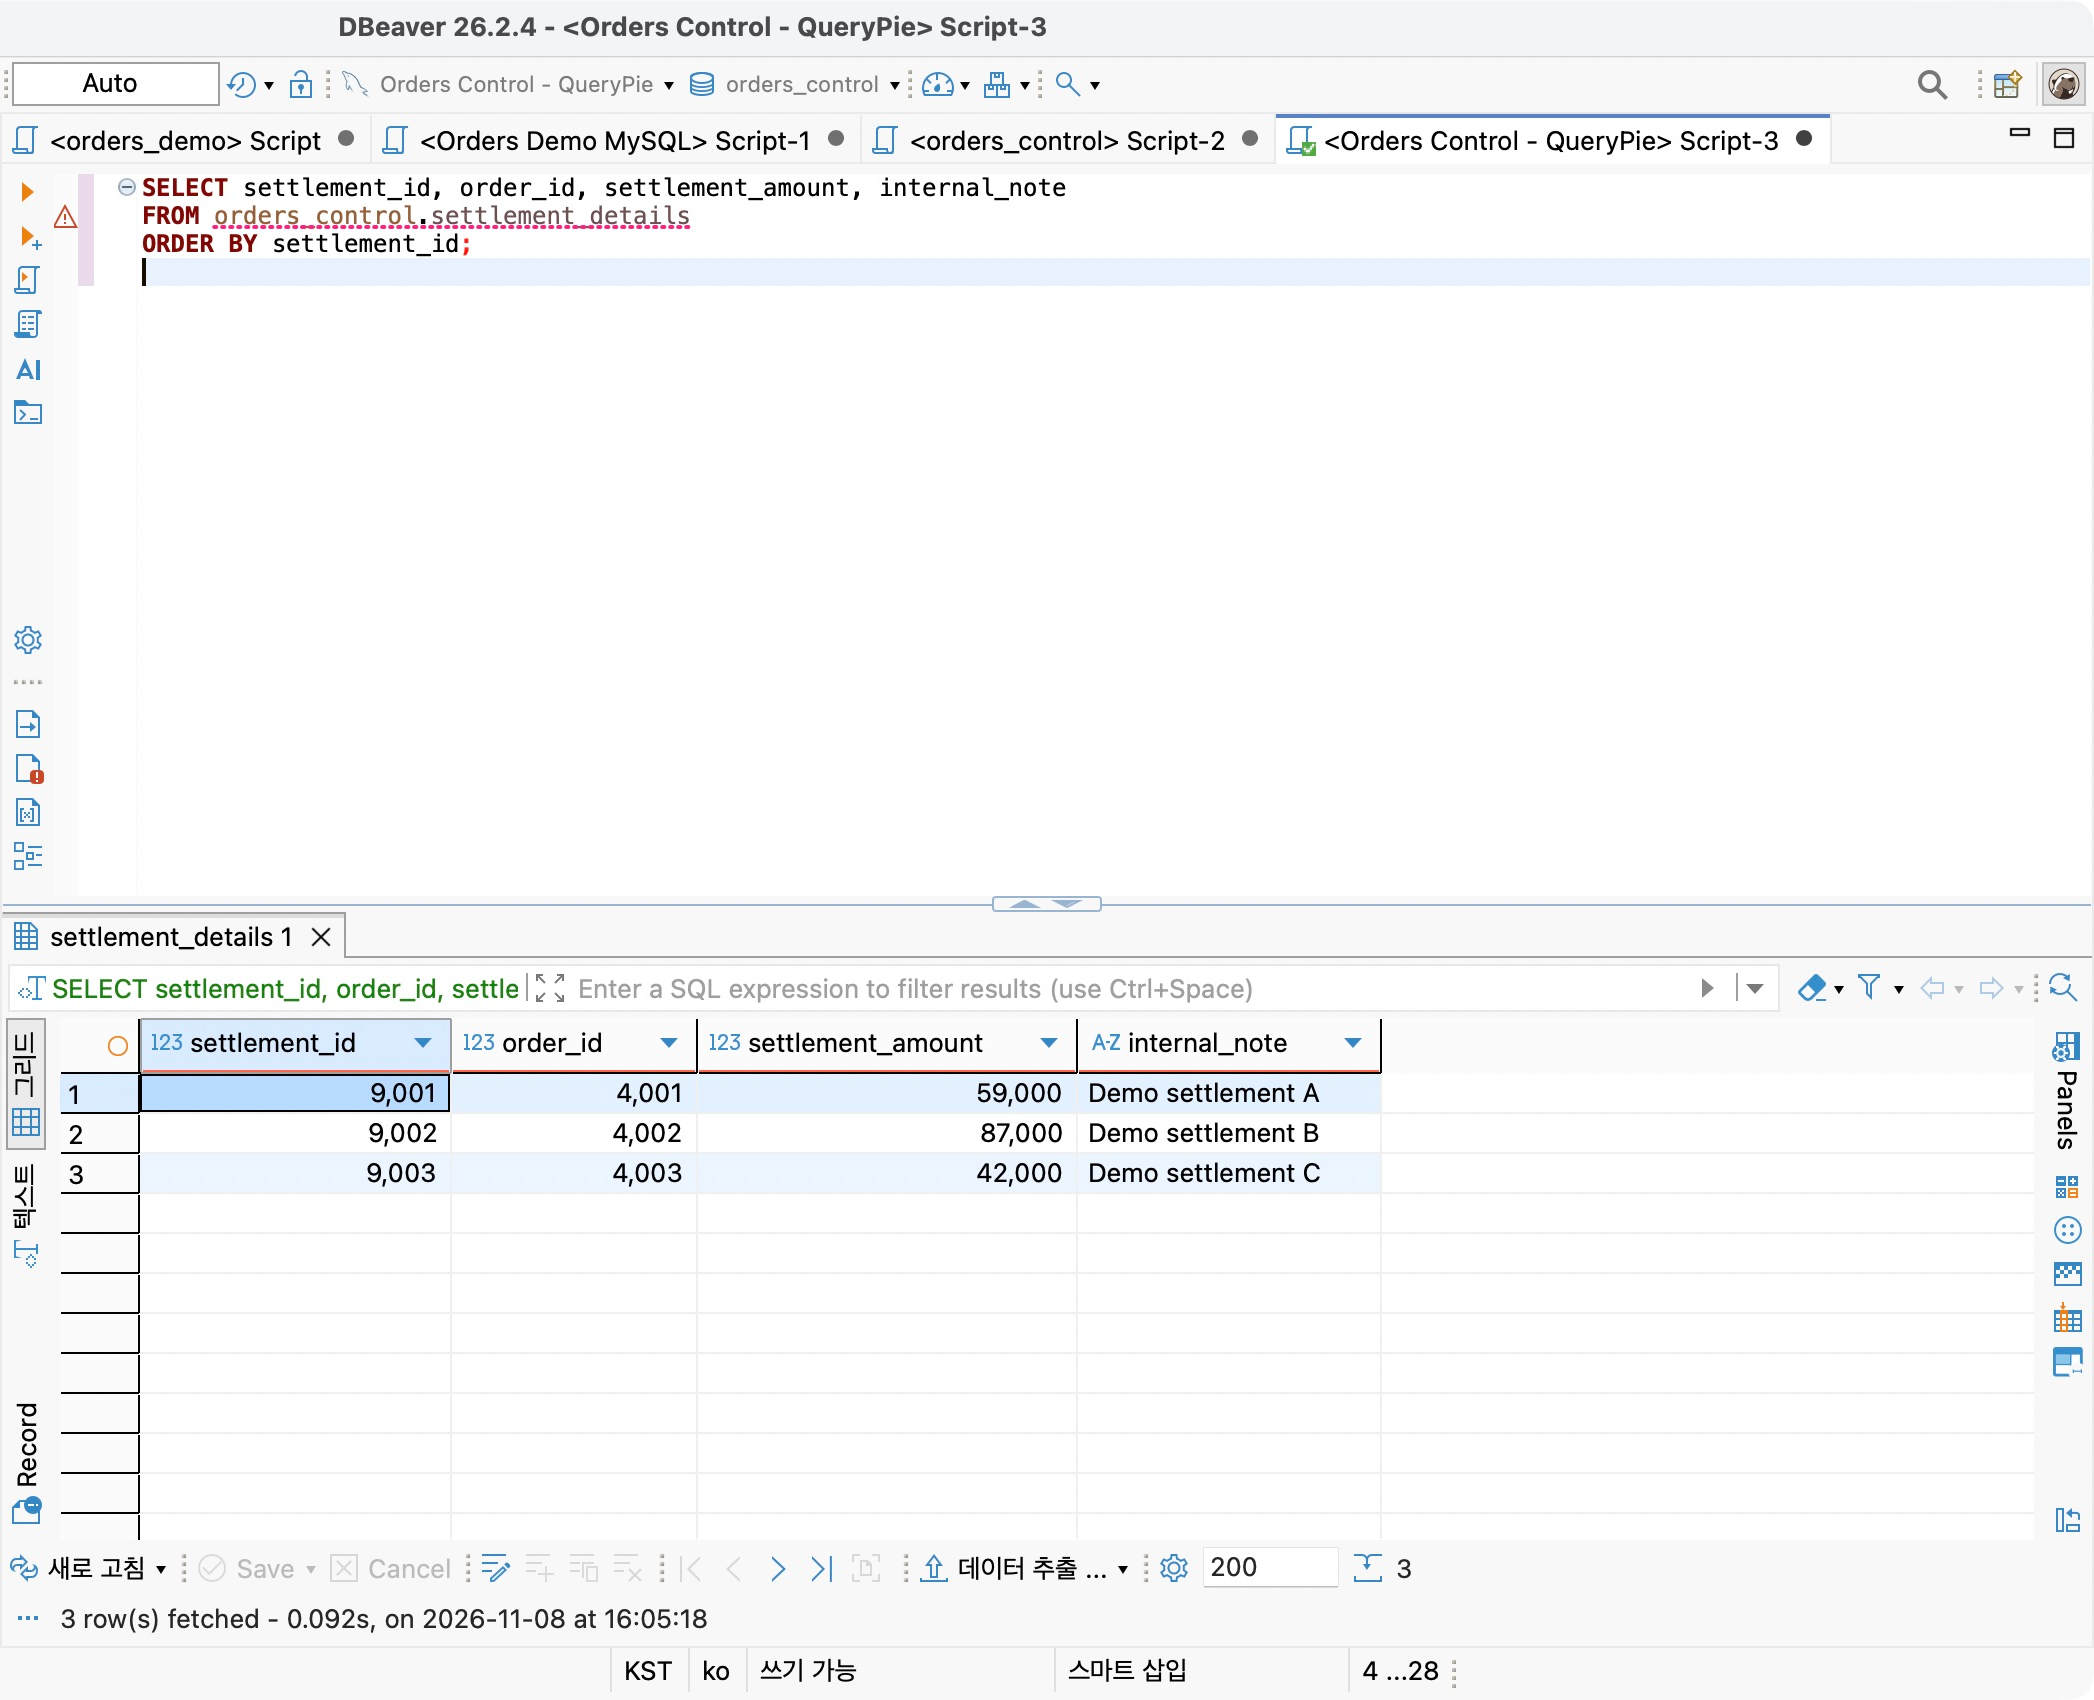
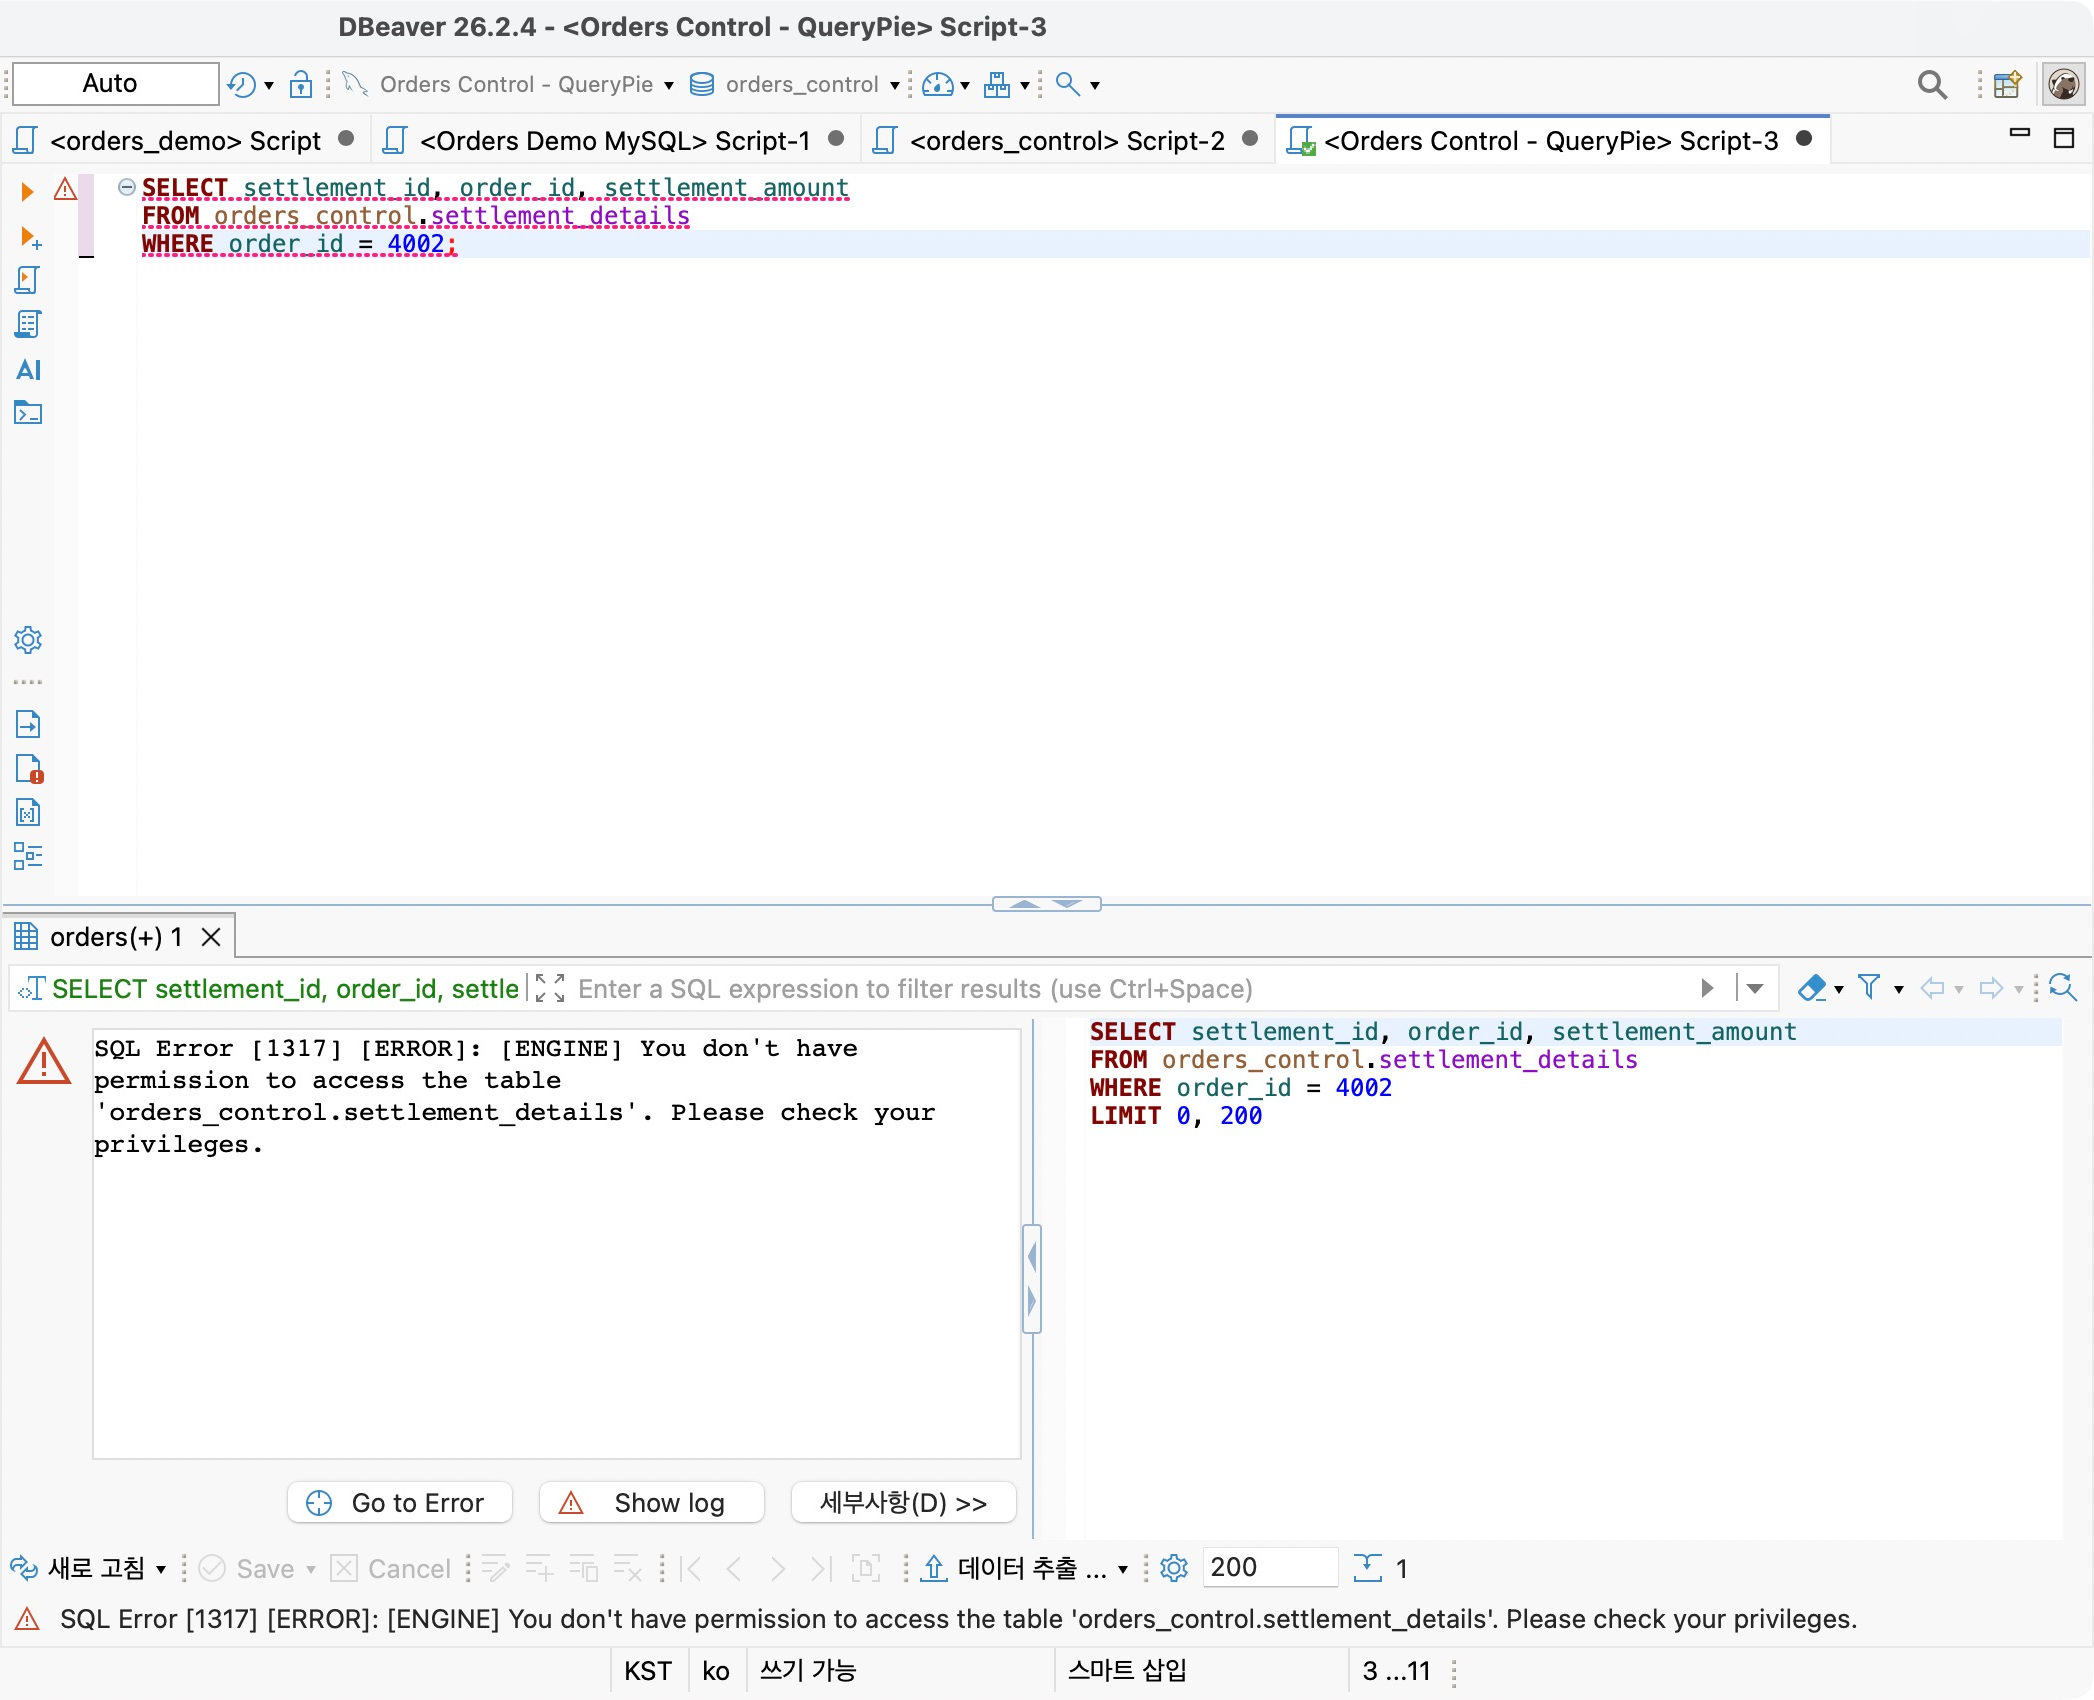
[Part 9] Allowing Order Queries While Protecting Settlements — QueryPie Table Access Restrictions
Allowing a database connection does not mean every table is needed. A developer checking orders does not necessarily need settlement amounts or internal notes. I put both tables in one database and tried allowing order queries while restricting settlements in QueryPie ACP.
White Papers
RAG 2.0 Security: Microsoft and Meta’s Groundwork, QueryPie Builds the Bridge
This article introduces the background and security architecture of RAG 2.0 and emphasizes the importance of execution flow control through various corporate cases. RAG 2.0 is differentiated from existing RAGs in that it goes beyond simple document search and applies policies in real time to prevent sensitive information from being delivered to the wrong users.
ACP Lab Notes
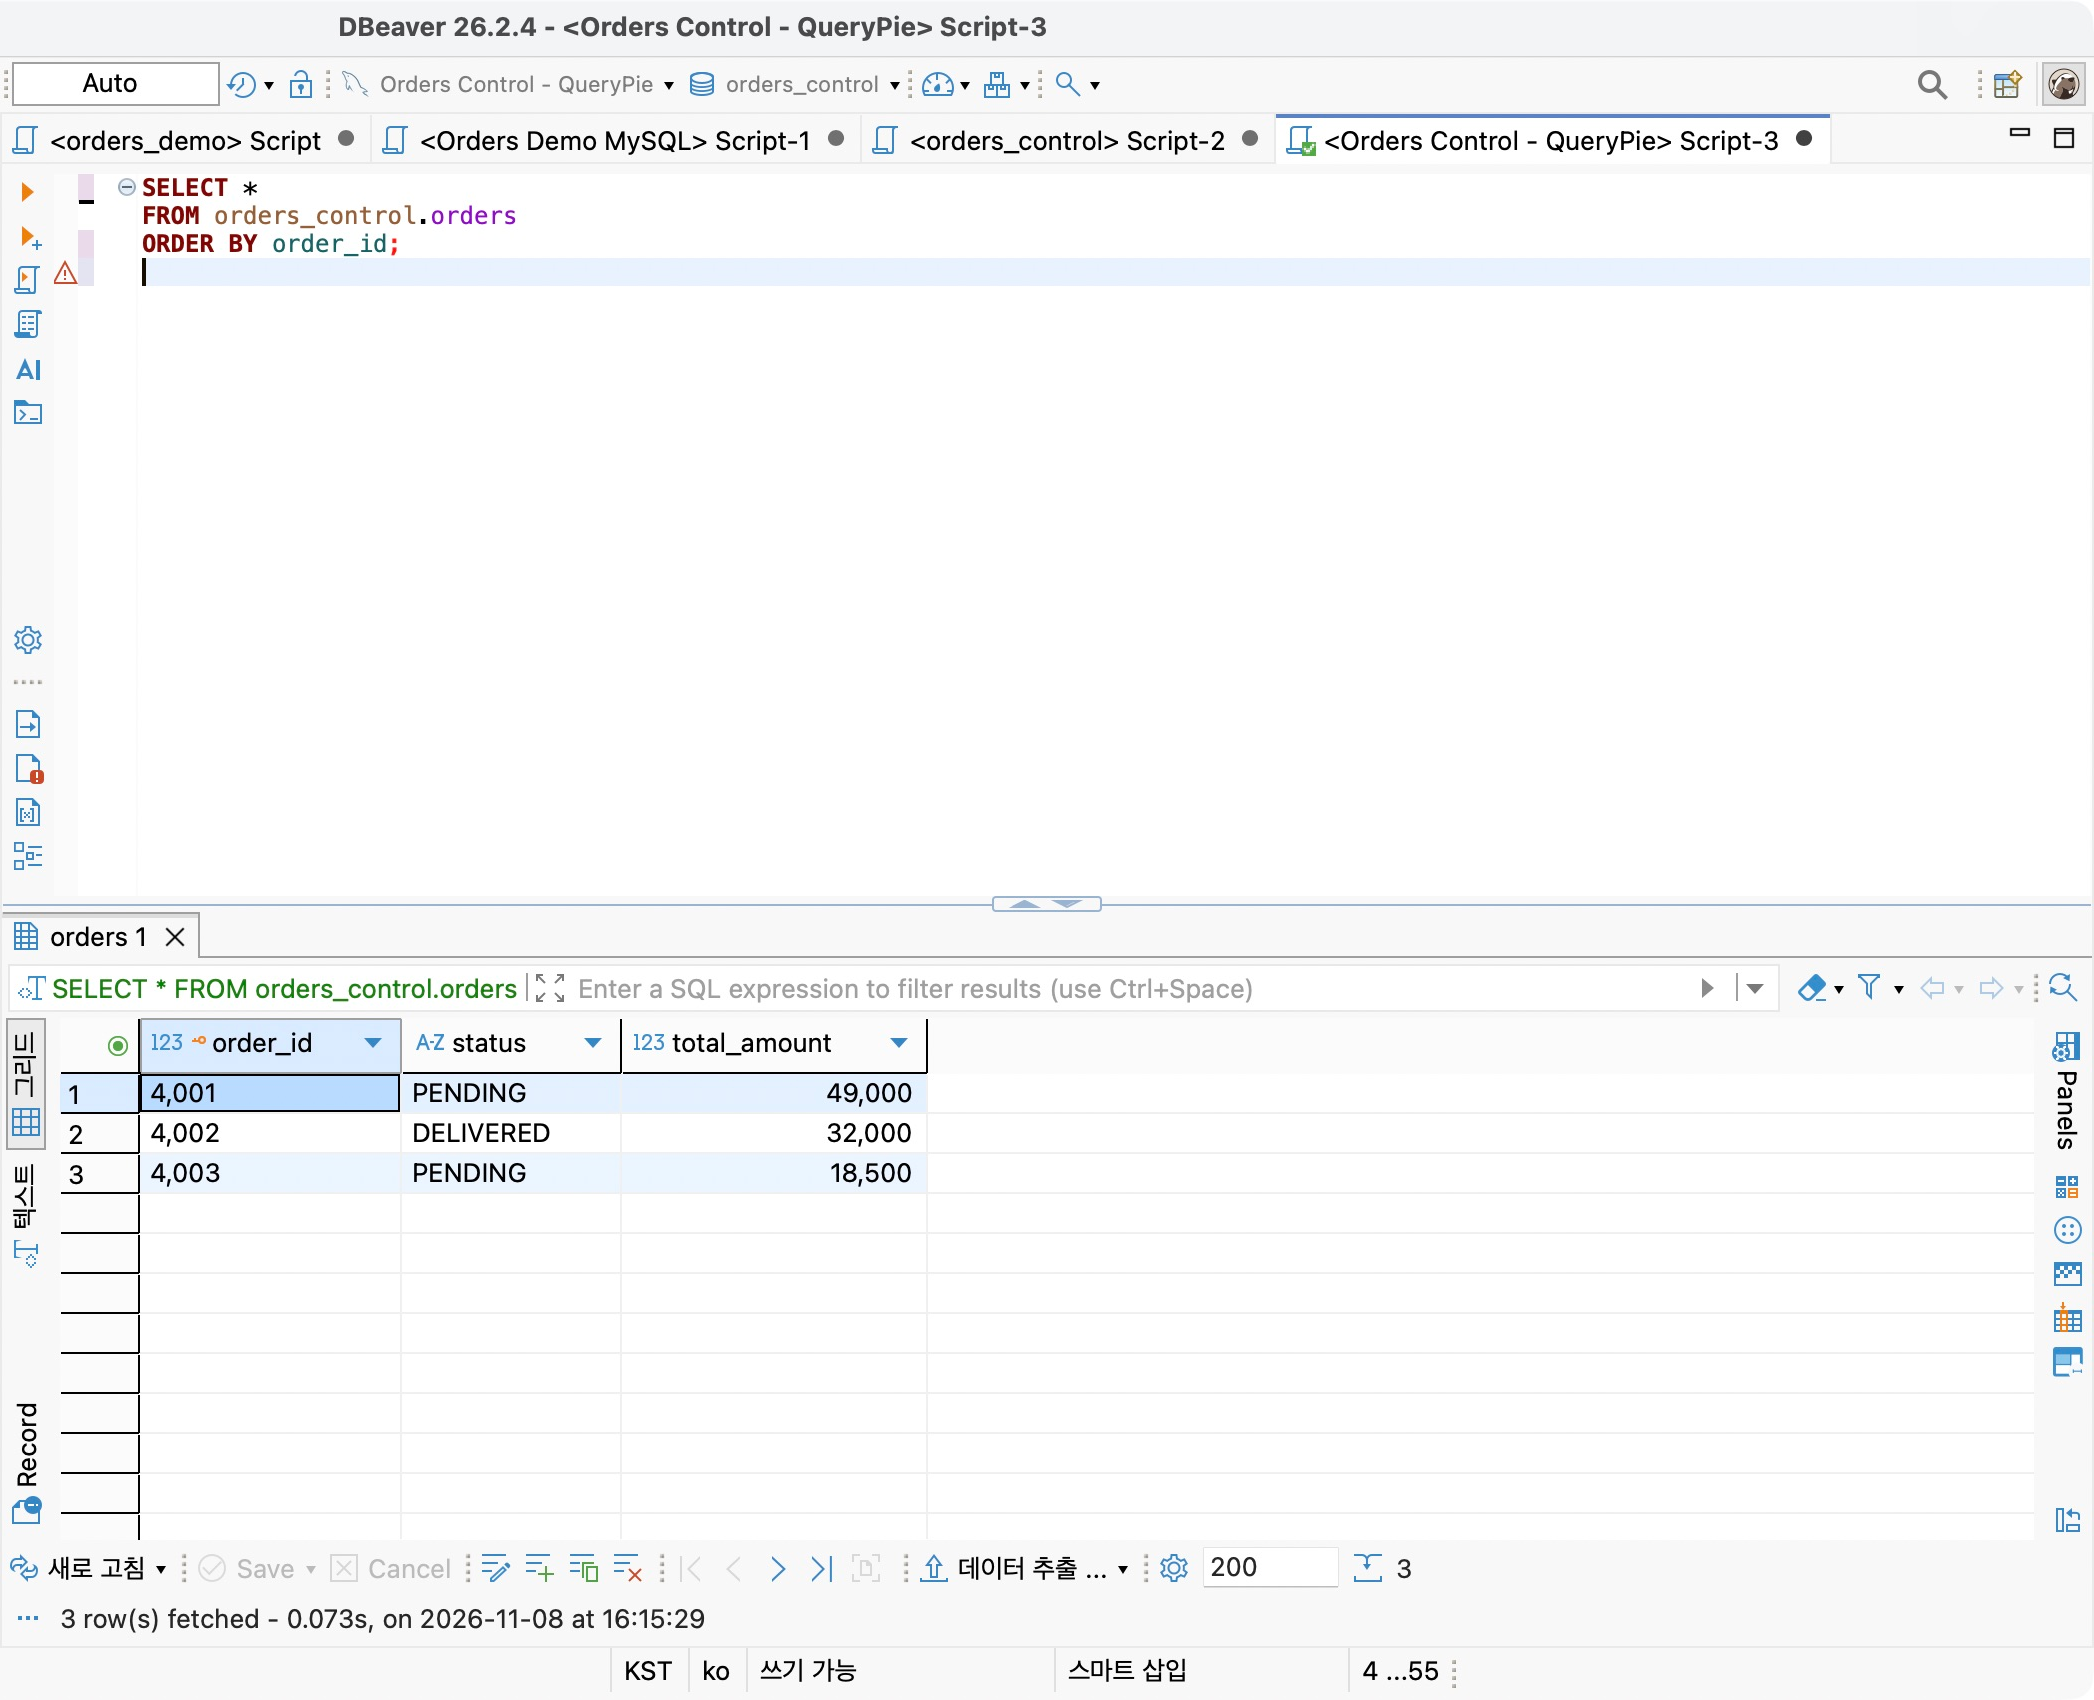
[Part 10] ‘Select Only the Columns You Need’ — Enforcing SQL Guidelines with QueryPie Query Rules
‘Specify only the columns you need.’ Teams sharing a database often adopt this rule. Habitual SELECT * retrieves extra fields such as amounts even when only order status is needed. I tried enforcing that guideline through QueryPie Query Rules.
Blog
Top 10 Privileged Access Management (PAM) Solutions You Should Know
Discover the top 10 Privileged Access Management (PAM) solutions that are essential for modern enterprise security, featuring comprehensive leading platforms that provide advanced credential management, zero-trust access control, and automated security features to protect your organization's critical IT infrastructure in today's rapidly evolving digital landscape.
August 11, 2025
White Papers
Your Architecture vs. AI Agents: Can MCP Hold the Line?
In this article, we clearly distinguish the roles of the MCP server and AI agents, providing a structured explanation of their respective responsibilities and limitations to prevent misunderstandings.
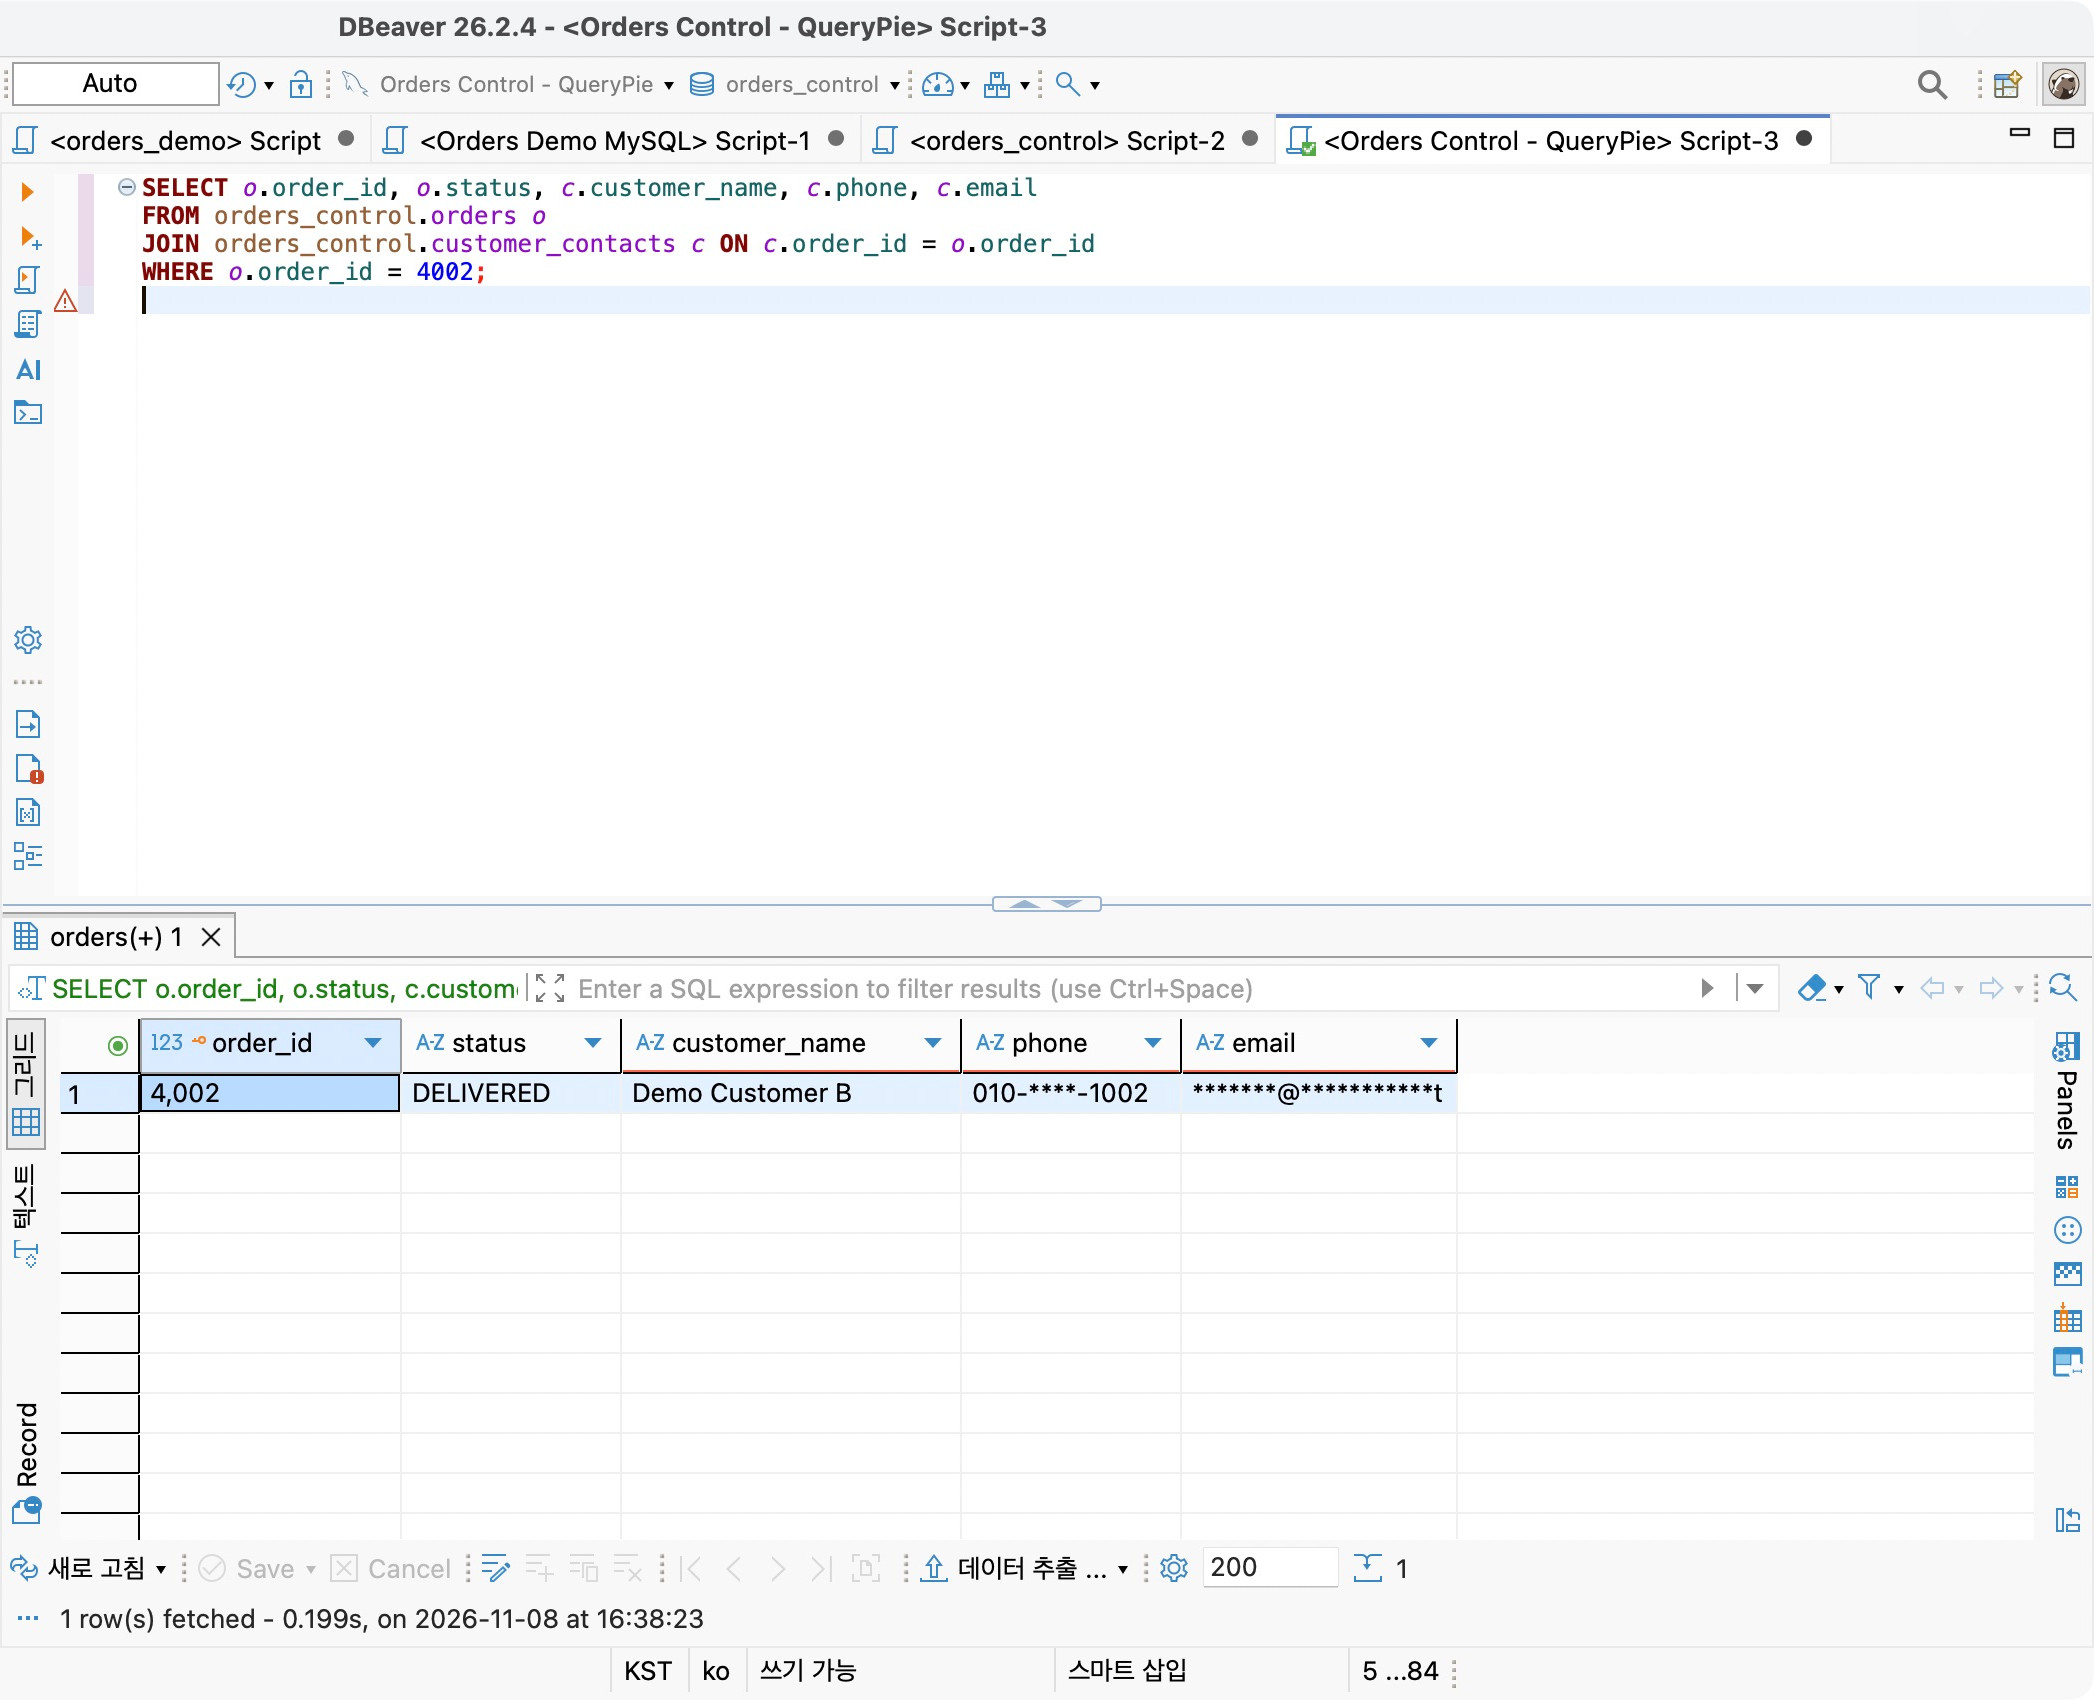
ACP Lab Notes
[Part 11] When a Masked Phone Number Is Needed — QueryPie Unmasking Requests and Approvals
Masking let us keep order information visible while hiding phone numbers and emails. But staff handling delivery inquiries sometimes need to contact a customer. Must the administrator change the entire masking policy each time? I tried QueryPie Unmasking Request instead.
White Papers
Welcome to the Age of AgentSecOps—Code Stands Still, Agents Take Over
As AI agent–based automation systems continue to proliferate, we’ve moved beyond simple task automation to a new paradigm: AgentOps, where autonomous agents make decisions and interact with external systems on their own. In this article, we explore the emerging concept of AgentSecOps—security operations tailored for agent-driven environments—and take a deep dive into how its structure and role compare to traditional DevSecOps frameworks.
ACP Lab Notes
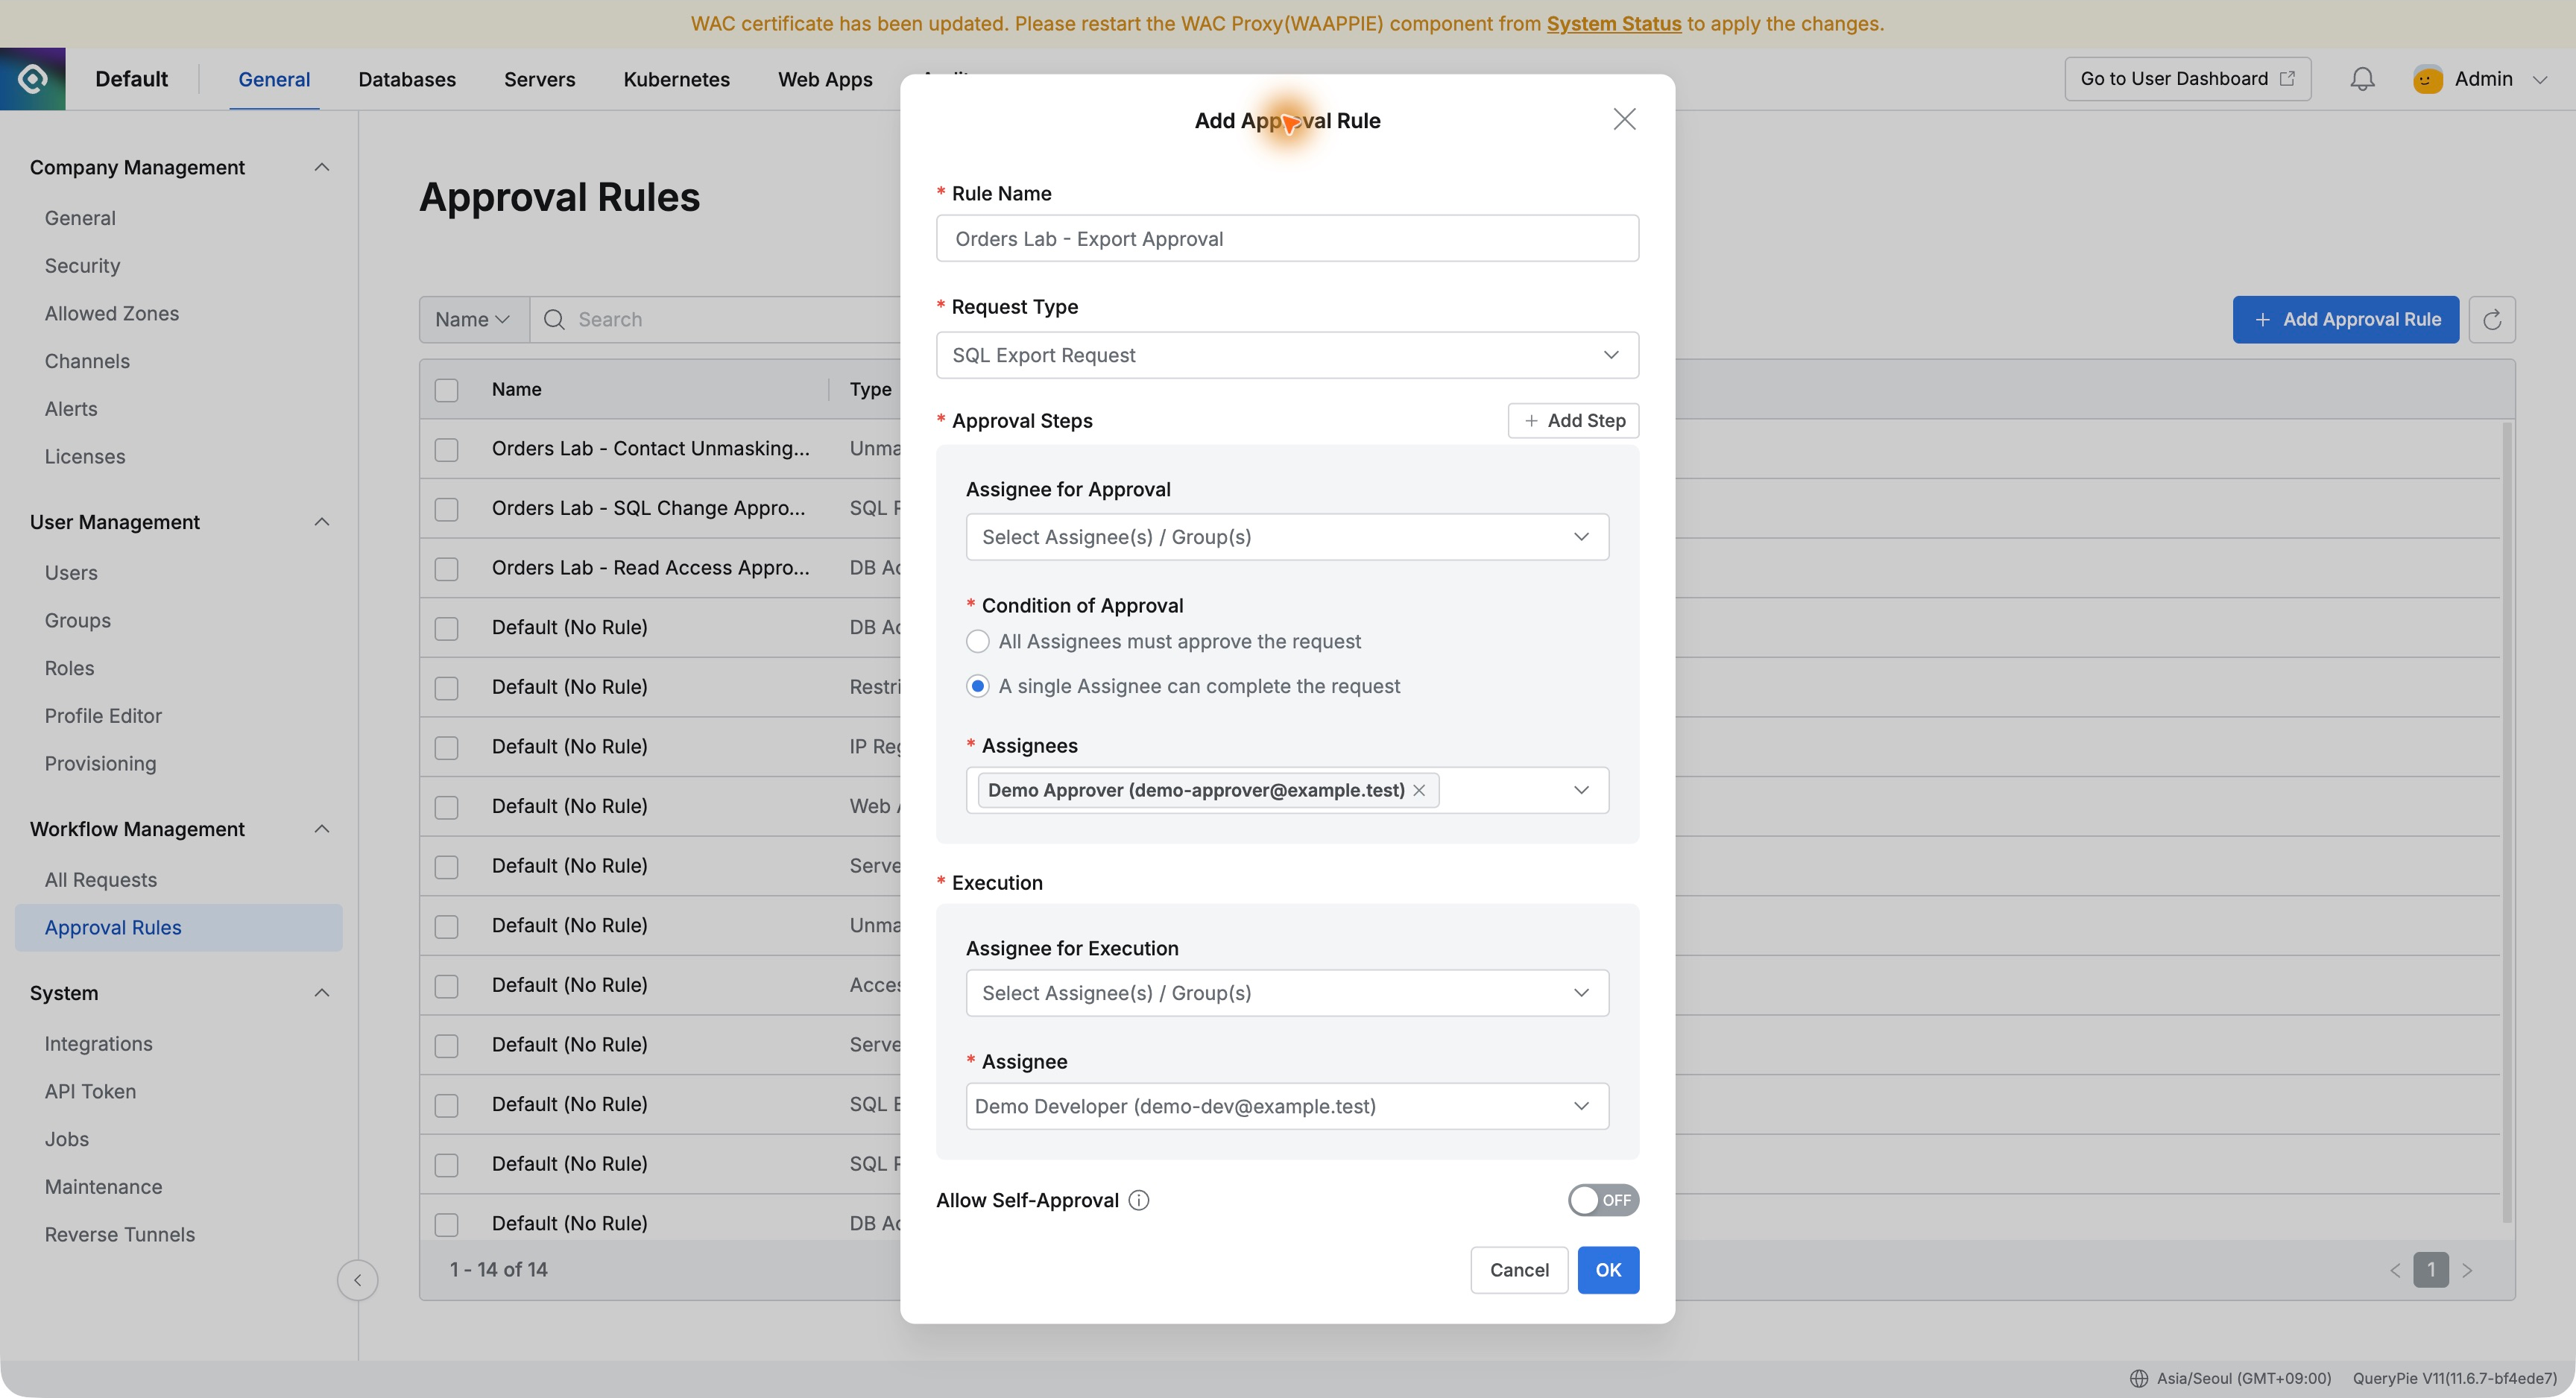
[Part 12] Exporting Database Data with Approval — QueryPie SQL Export in Practice
Query results sometimes need to become a report. A file makes shipping summaries and amount comparisons easier, but operators also want to know who downloaded what and why. I tried SQL Export Request for an order summary.
Blog
How Much Can We Trust AI? The Naked Truth of AI Agent Security Through the Replit Incident
The incident where Replit AI Agent deleted a production DB is not just a technical mistake, but highlights the importance of security architecture when deploying AI agents in real environments. This case summarizes a security checklist including AI hallucination detection, least privilege design, and execution log retention.
July 29, 2025
White Papers
Beyond MCP to MCPS: The Need for a Secure Protocol for Enterprise AI
MCP(Model Context Protocol) is innovative, but it has a critical weakness for use in enterprise environments. In this article, we will look at the basic concepts and current status of MCP, and deeply analyze the security issues that arise in enterprise environments.
ACP Lab Notes
[Part 13] When Settlement Data Is Needed — Approving Restricted Data Access in QueryPie
Part 9 allowed order queries while restricting settlements. A developer normally checking status did not need settlement data. But reconciliation can require it. I tried Restricted Data Access Request to obtain approved, time-limited access without removing the policy.
Blog
AI Rebels Are Becoming Reality — Why We Need AI Red Teaming
AI is no longer just generating answers — it’s executing real-world actions. Through real incidents and case studies, QueryPie explains emerging AI security threats like command refusal and indirect prompt injection, and why AI Red Teaming is now essential.
June 10, 2025
White Papers
Google Agentspace Gets Things Done—QueryPie MCP PAM Keeps Them Safe
Google Agentspace is a powerful AI execution platform, but unchecked automation raises security concerns. This post explores how QueryPie MCP PAM enables secure, policy-based control for enterprise-grade AI adoption.
ACP Lab Notes
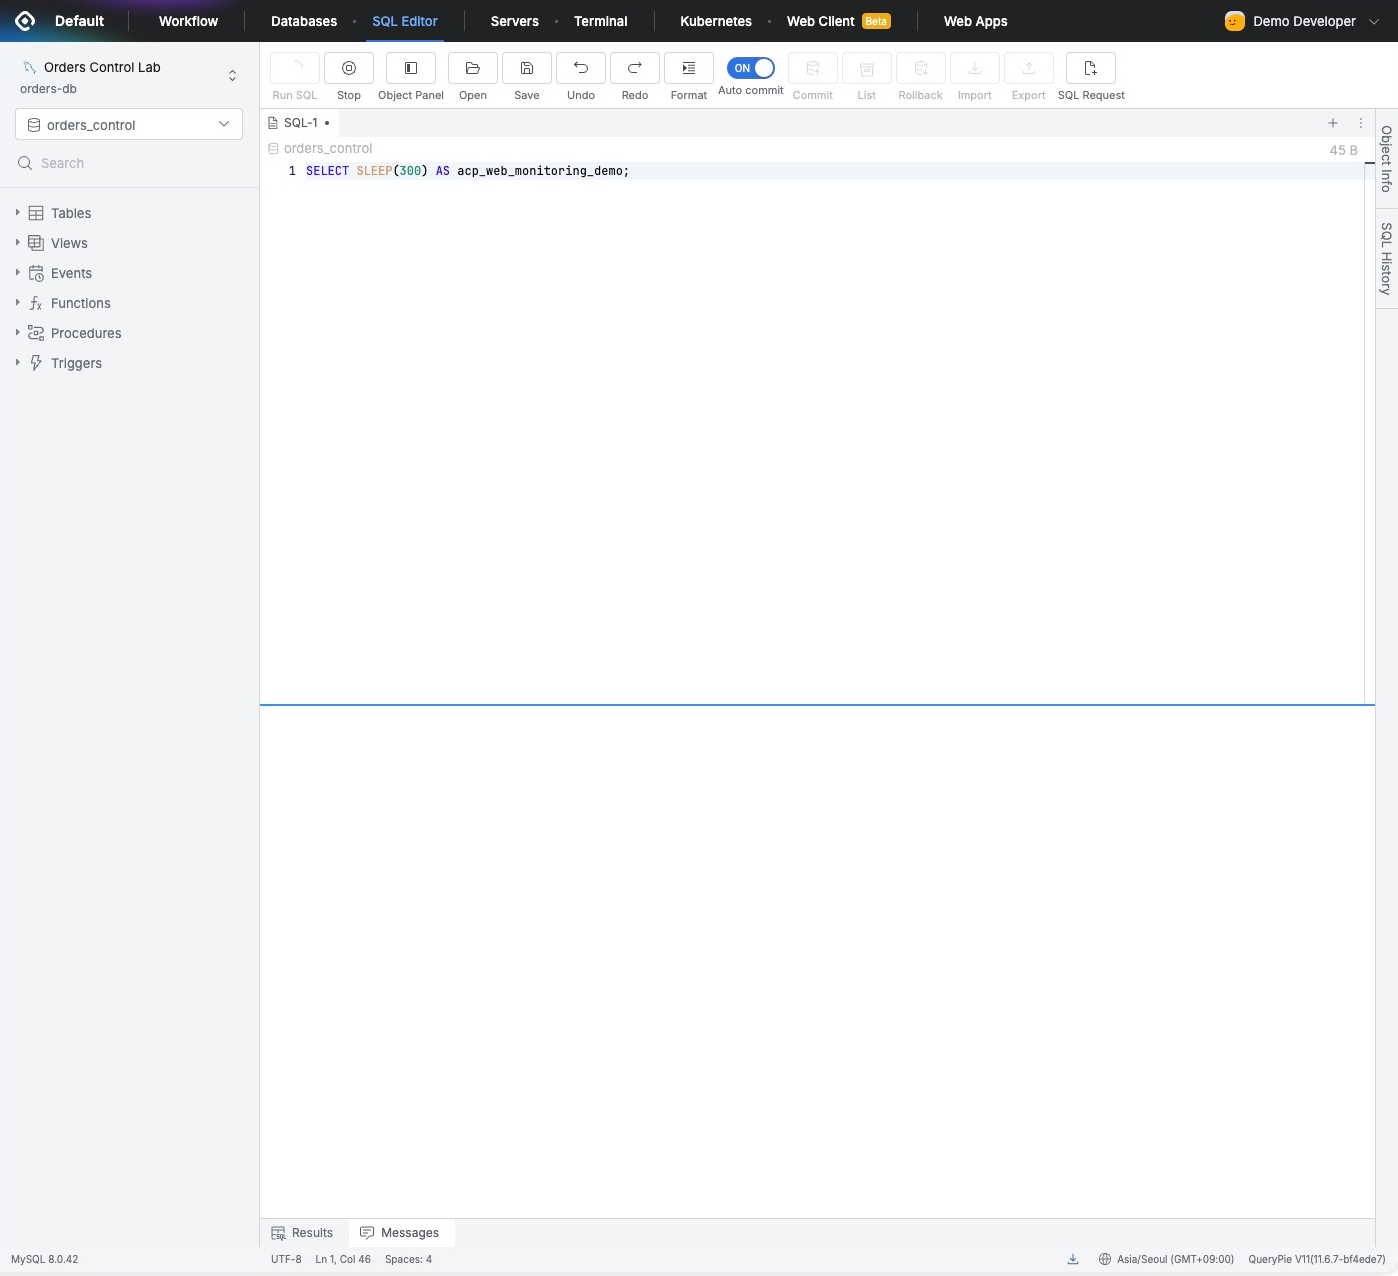
[Part 14] Stopping a Running SQL Statement — QueryPie Query Monitoring
Even with access controls and approvals, operators sometimes need to inspect SQL already running. A slow-query report starts with identifying who ran what and where. I tried Running Queries to locate and stop a web-editor test query.
White Papers
Uncovering MCP Security: Threat Mapping and Vulnerability Analysis through Literature-based Investigation
As AI systems become increasingly interconnected, context sharing between models is critical to ensure reliable reasoning and secure execution. This white paper analyzes recent research on the Model Context Protocol (MCP), identifies key security threats, and proposes a next-generation architecture—MCP PAM—for context-aware access control and autonomous policy enforcement.
Blog
Next.js Server Action and Frontend Security
Next.js Server Actions' high-level abstractions may lead developers to make security mistakes. This article analyzes these risks and presents development strategies to prevent security errors. Enhance your security awareness when developing server-side code in the frontend to build safer and more efficient web applications!
March 20, 2025
ACP Lab Notes
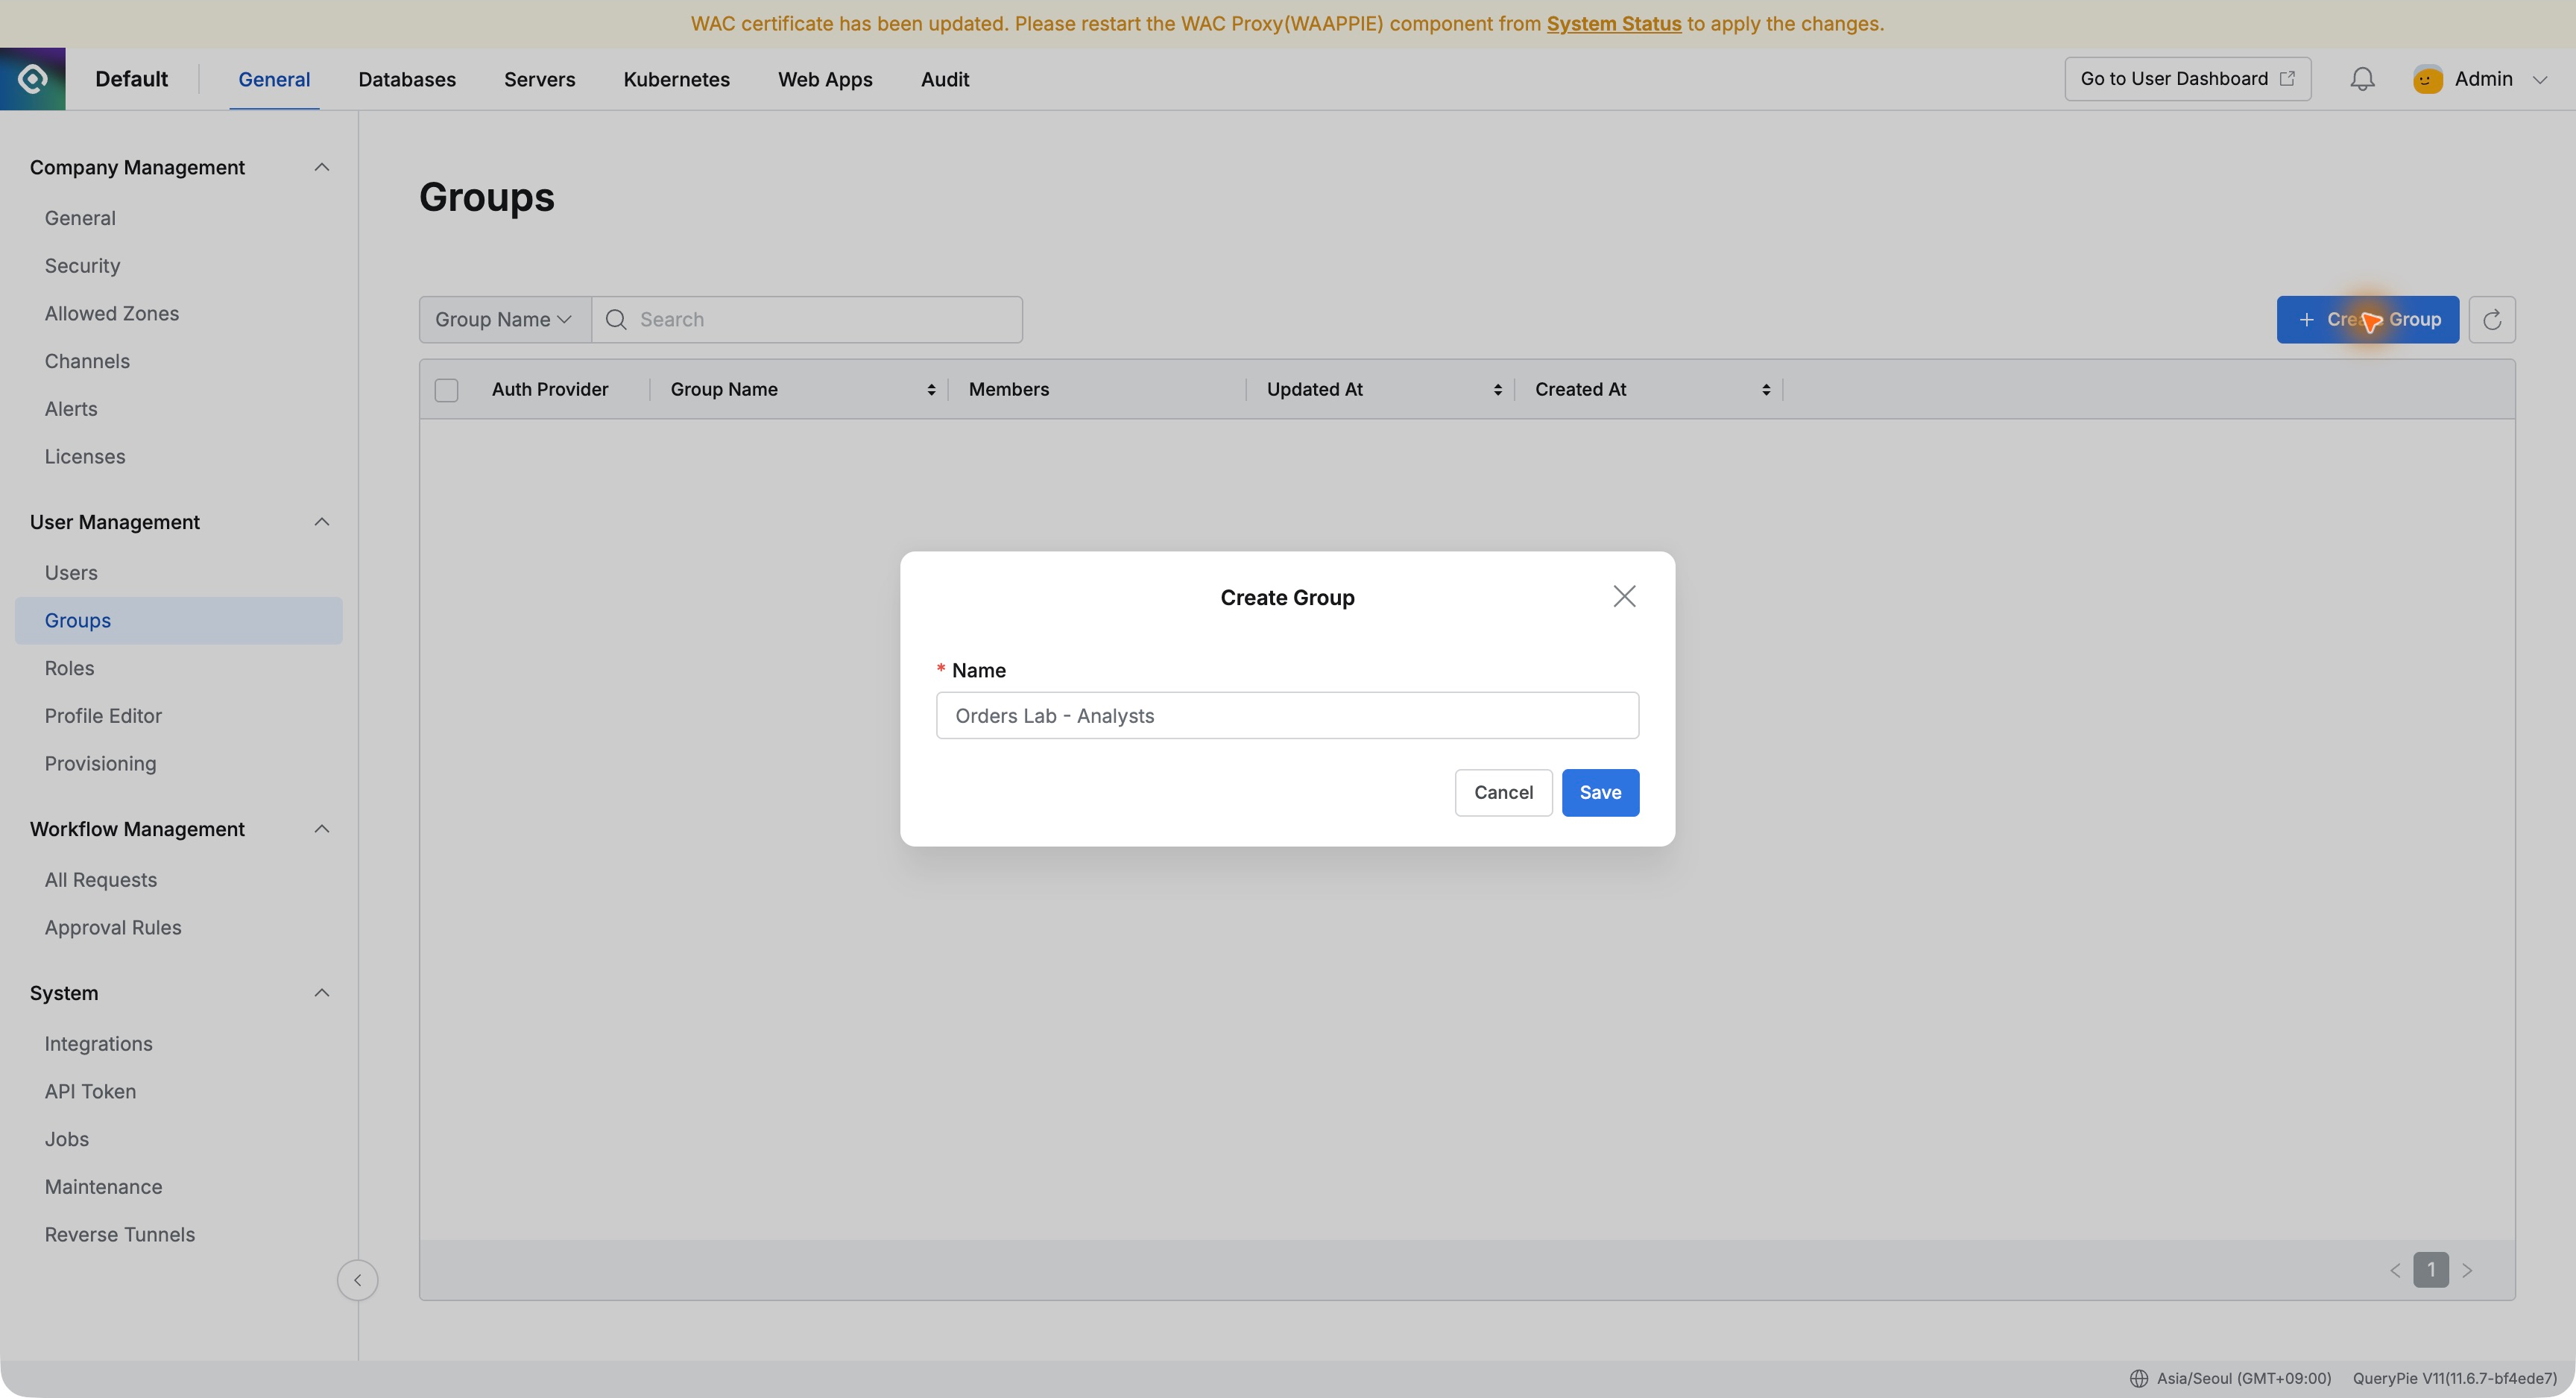
[Part 15] Join the Team, Receive Database Access — QueryPie Group Management
Granting one user access was enough at first, but individually checking privileges becomes tedious as a team grows. I created an order-analysis group, granted read-only access to the group, and added a new analyst without assigning individual database privileges.
White Papers
AI Can Drive Itself—Why Not Secure Itself? Introducing Autonomous Access Control
In an era where AI directly executes system operations, traditional security models are no longer enough. This white paper introduces a new security paradigm for MCP-based AI execution environments—QueryPie MCP PAM—and outlines strategic approaches to achieving Autonomous Access Control.
Blog
Cost Optimization through EC2 Automation: Leveraging AWS Lambda and EventBridge
Learn how to optimize EC2 costs by automating instances with AWS Lambda and EventBridge. This guide explores best practices for cost reduction through serverless solutions.
February 7, 2025
ACP Lab Notes
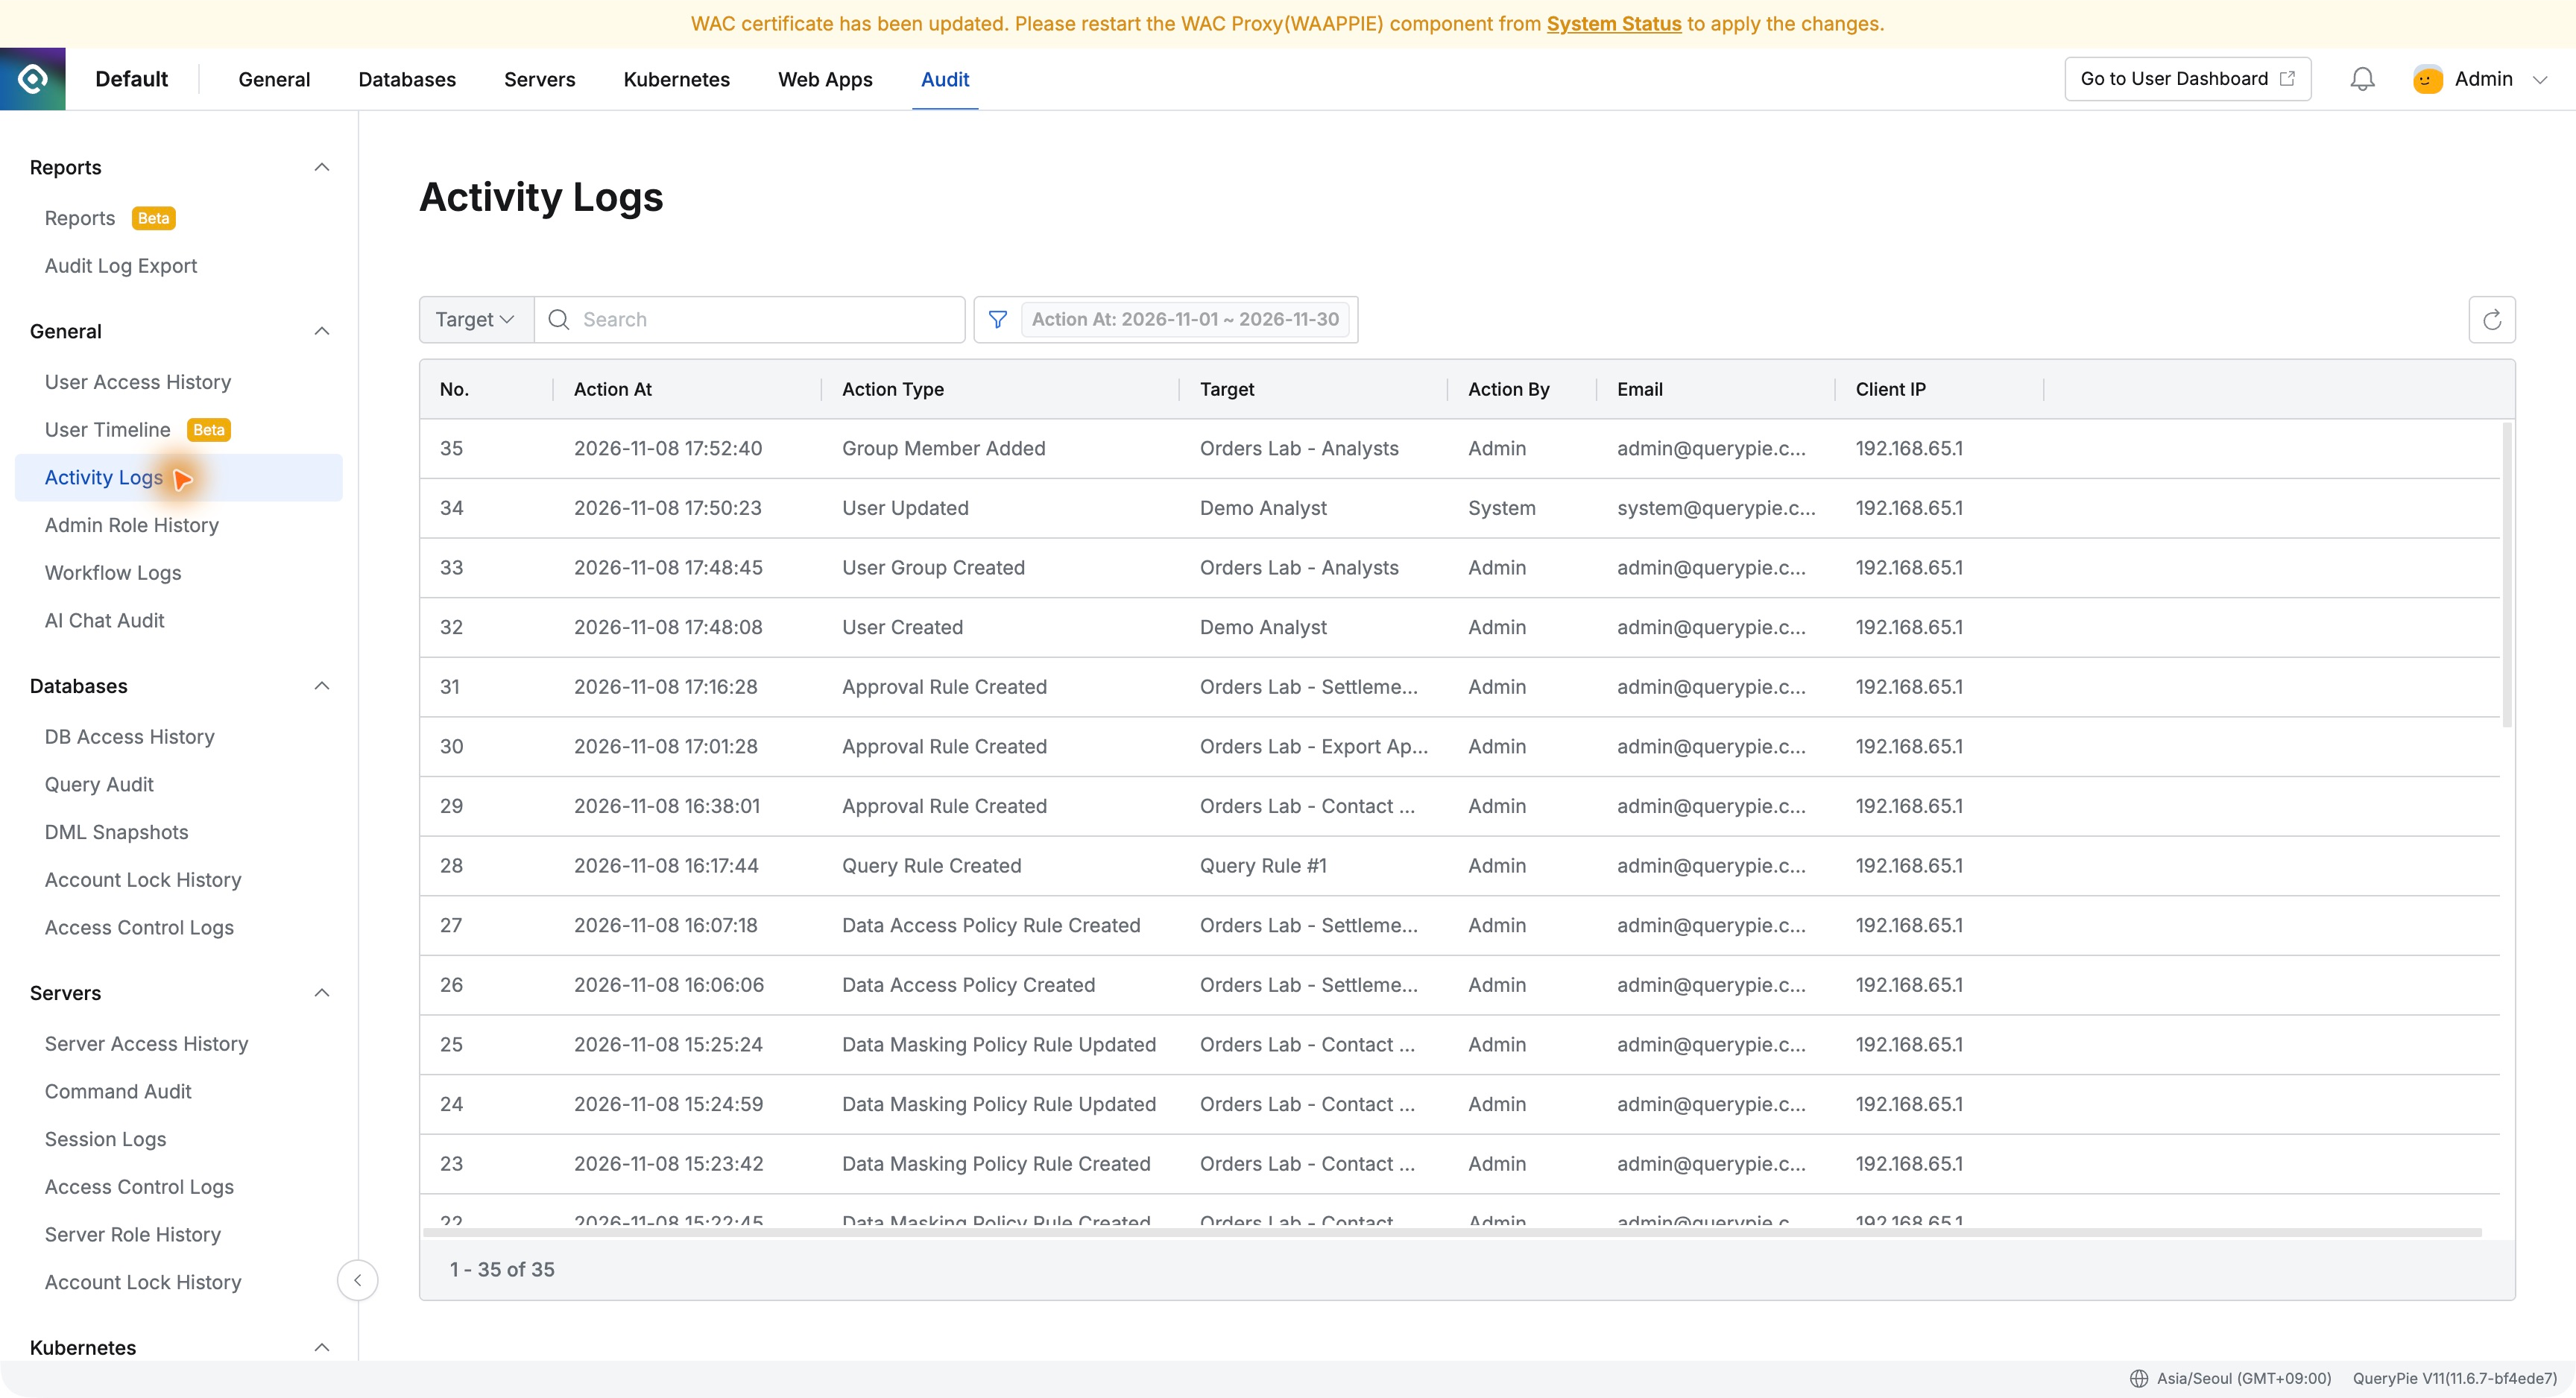
[Part 16] Who Granted This Database Access? — QueryPie Administrator Change History
After creating an analysts group and adding a user, I wondered whether a future operator could explain how the current privileges came about. I searched QueryPie audits for the group creation, access grant, and membership change.
White Papers
MCP PAM as the Next Step Beyond Guardrails
As generative AI adoption accelerates, traditional guardrails fall short in securing real-world LLM integrations. This whitepaper explores how MCP-based Privileged Access Management (PAM) complements existing safeguards to enforce user-intent-aware, context-driven control over AI operations—addressing threats like prompt injection, insider abuse, and sensitive data leakage.
Blog
Why is SSO important?
Understand why Single Sign-On (SSO) is crucial for enhancing user experience, streamlining access, and improving security across multiple platforms. See the benefits today!
February 4, 2025
ACP Lab Notes
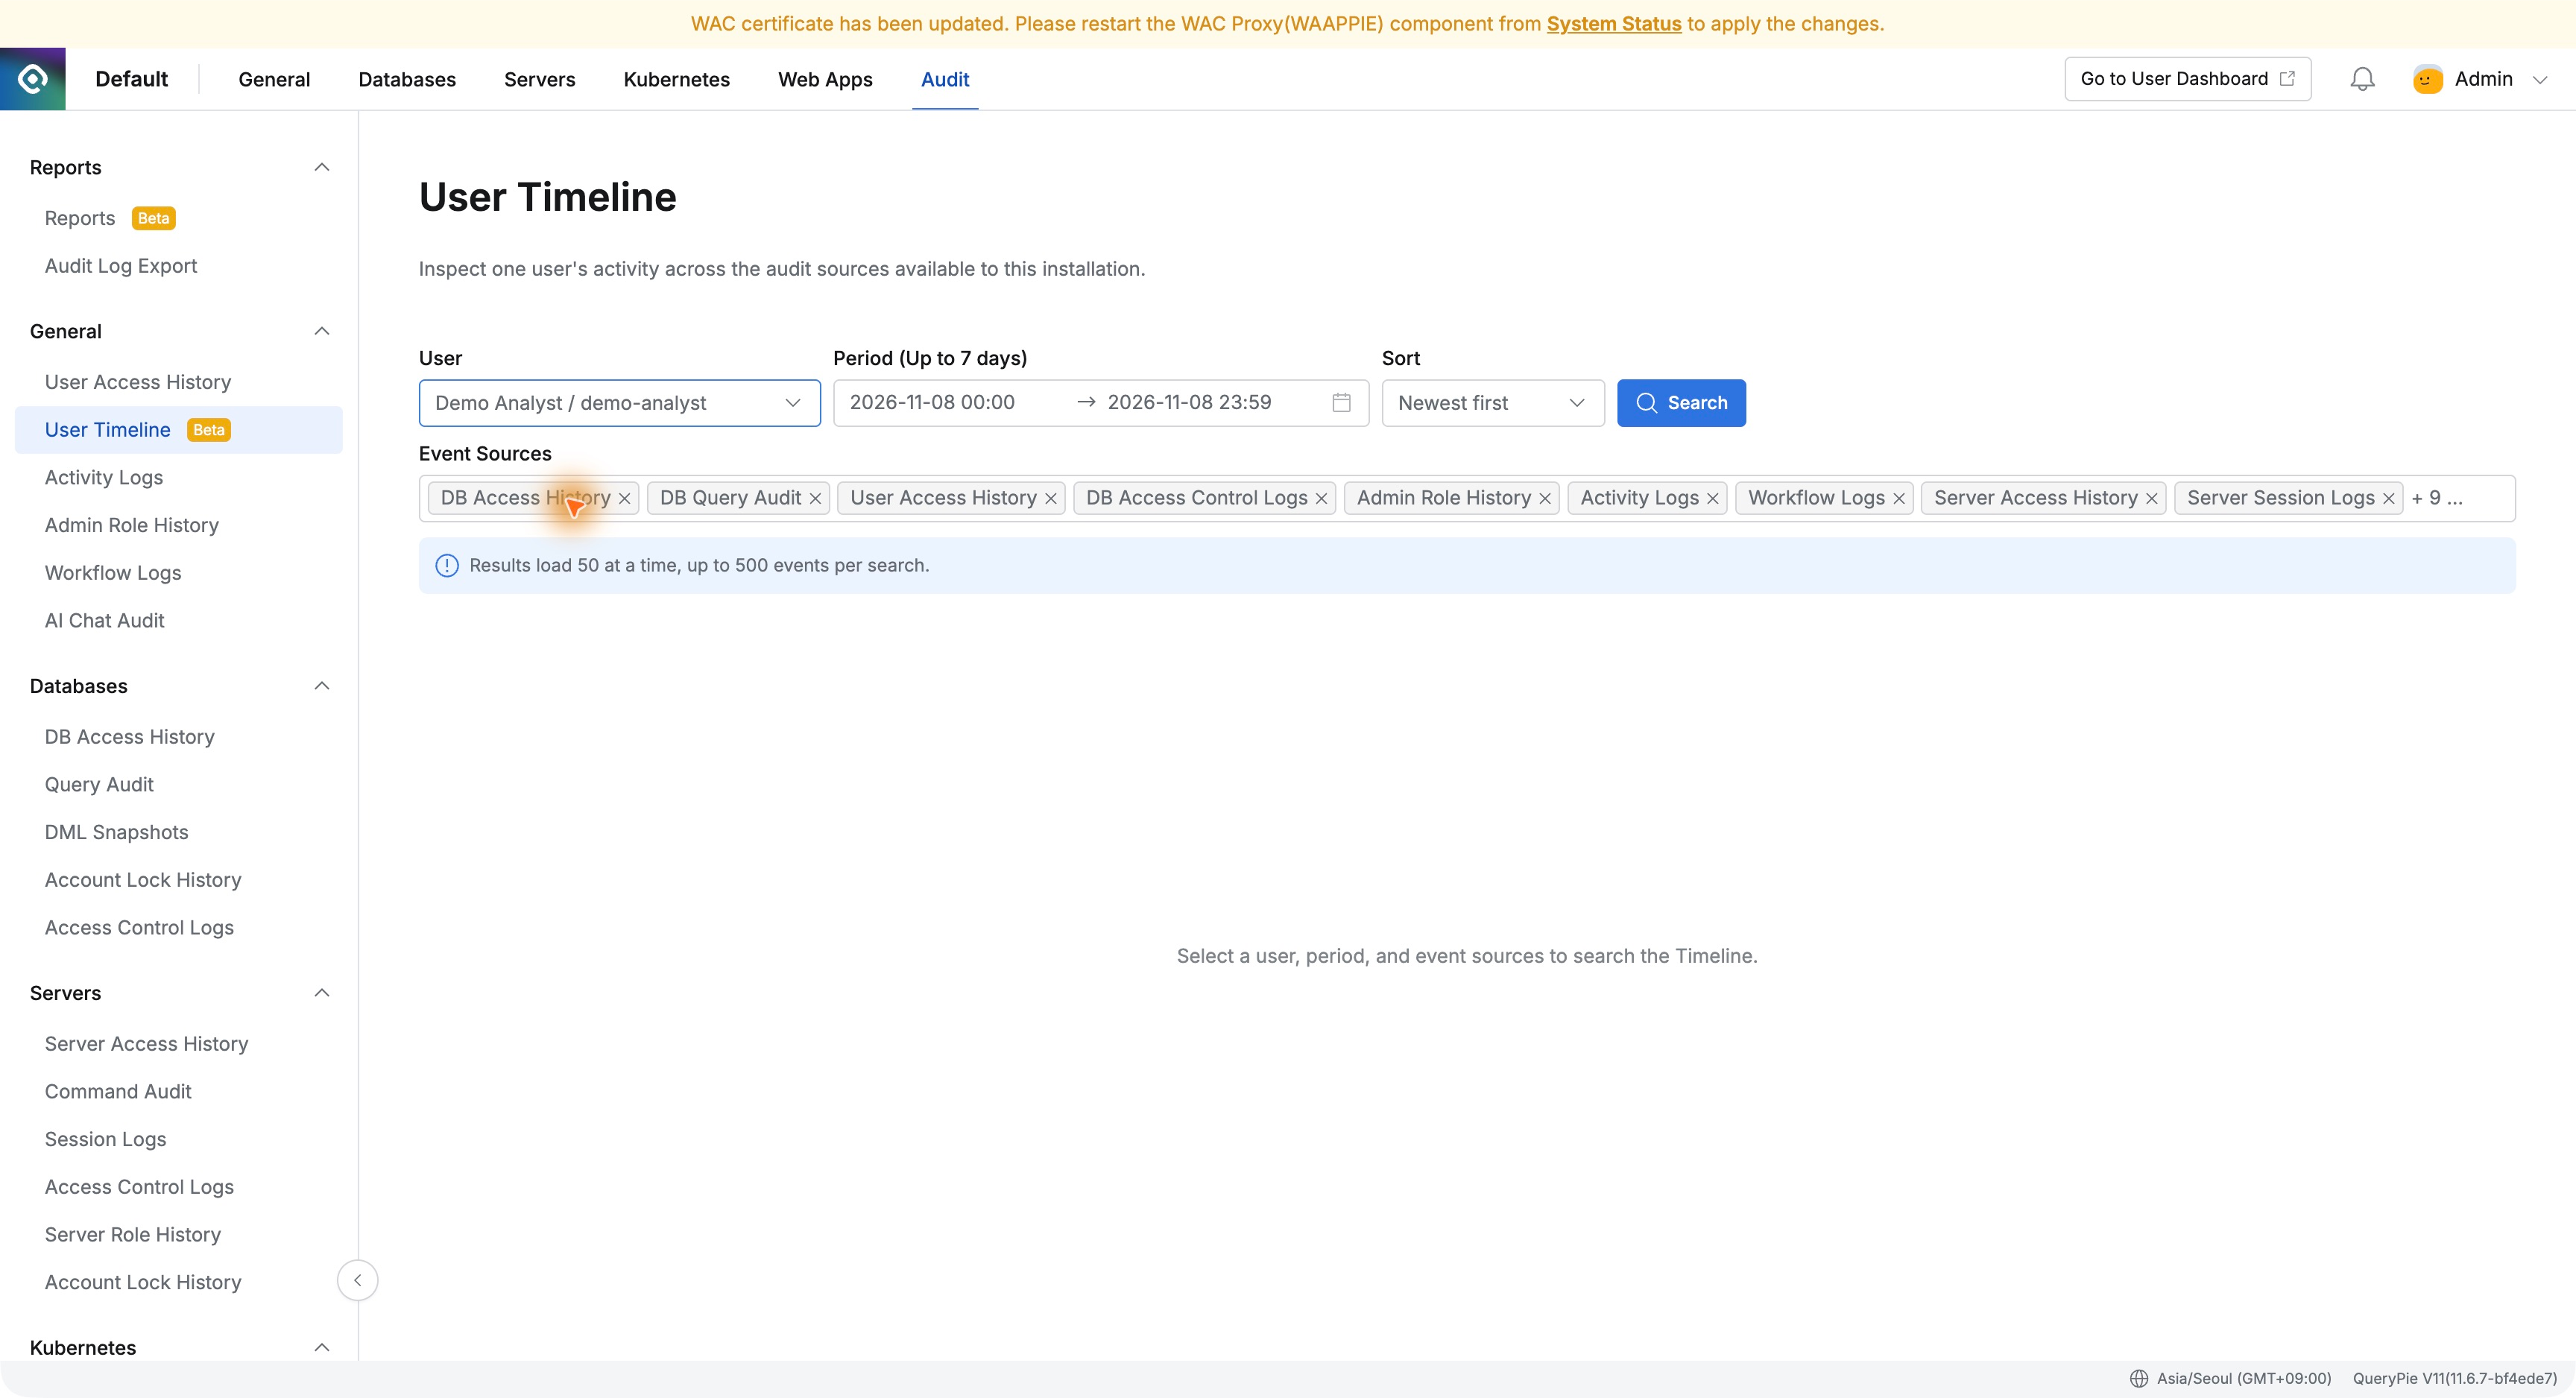
[Part 17] What Did This User Do? — QueryPie User Timeline
‘I can connect to the database, but one operation fails.’ Operators must distinguish login problems, connection issues, and blocked SQL. I used User Timeline to follow Demo Analyst’s successful read and blocked UPDATE in one sequence.
White Papers
Security Governance and Integrated PAM Strategy for AI Agents in the Age of the Model Context Protocol (MCP)
Learn how integrating Privileged Access Management (PAM) into the Model Context Protocol (MCP) framework strengthens AI governance, enhances visibility, and mitigates emerging security risks in enterprise environments.
Blog
Demystifying Privileged Access Management: Insights, Comparisons, and Practical Applications
Discover how PAM strengthens security by managing and monitoring privileged access, reducing risks to critical data.
January 23, 2025
ACP Lab Notes
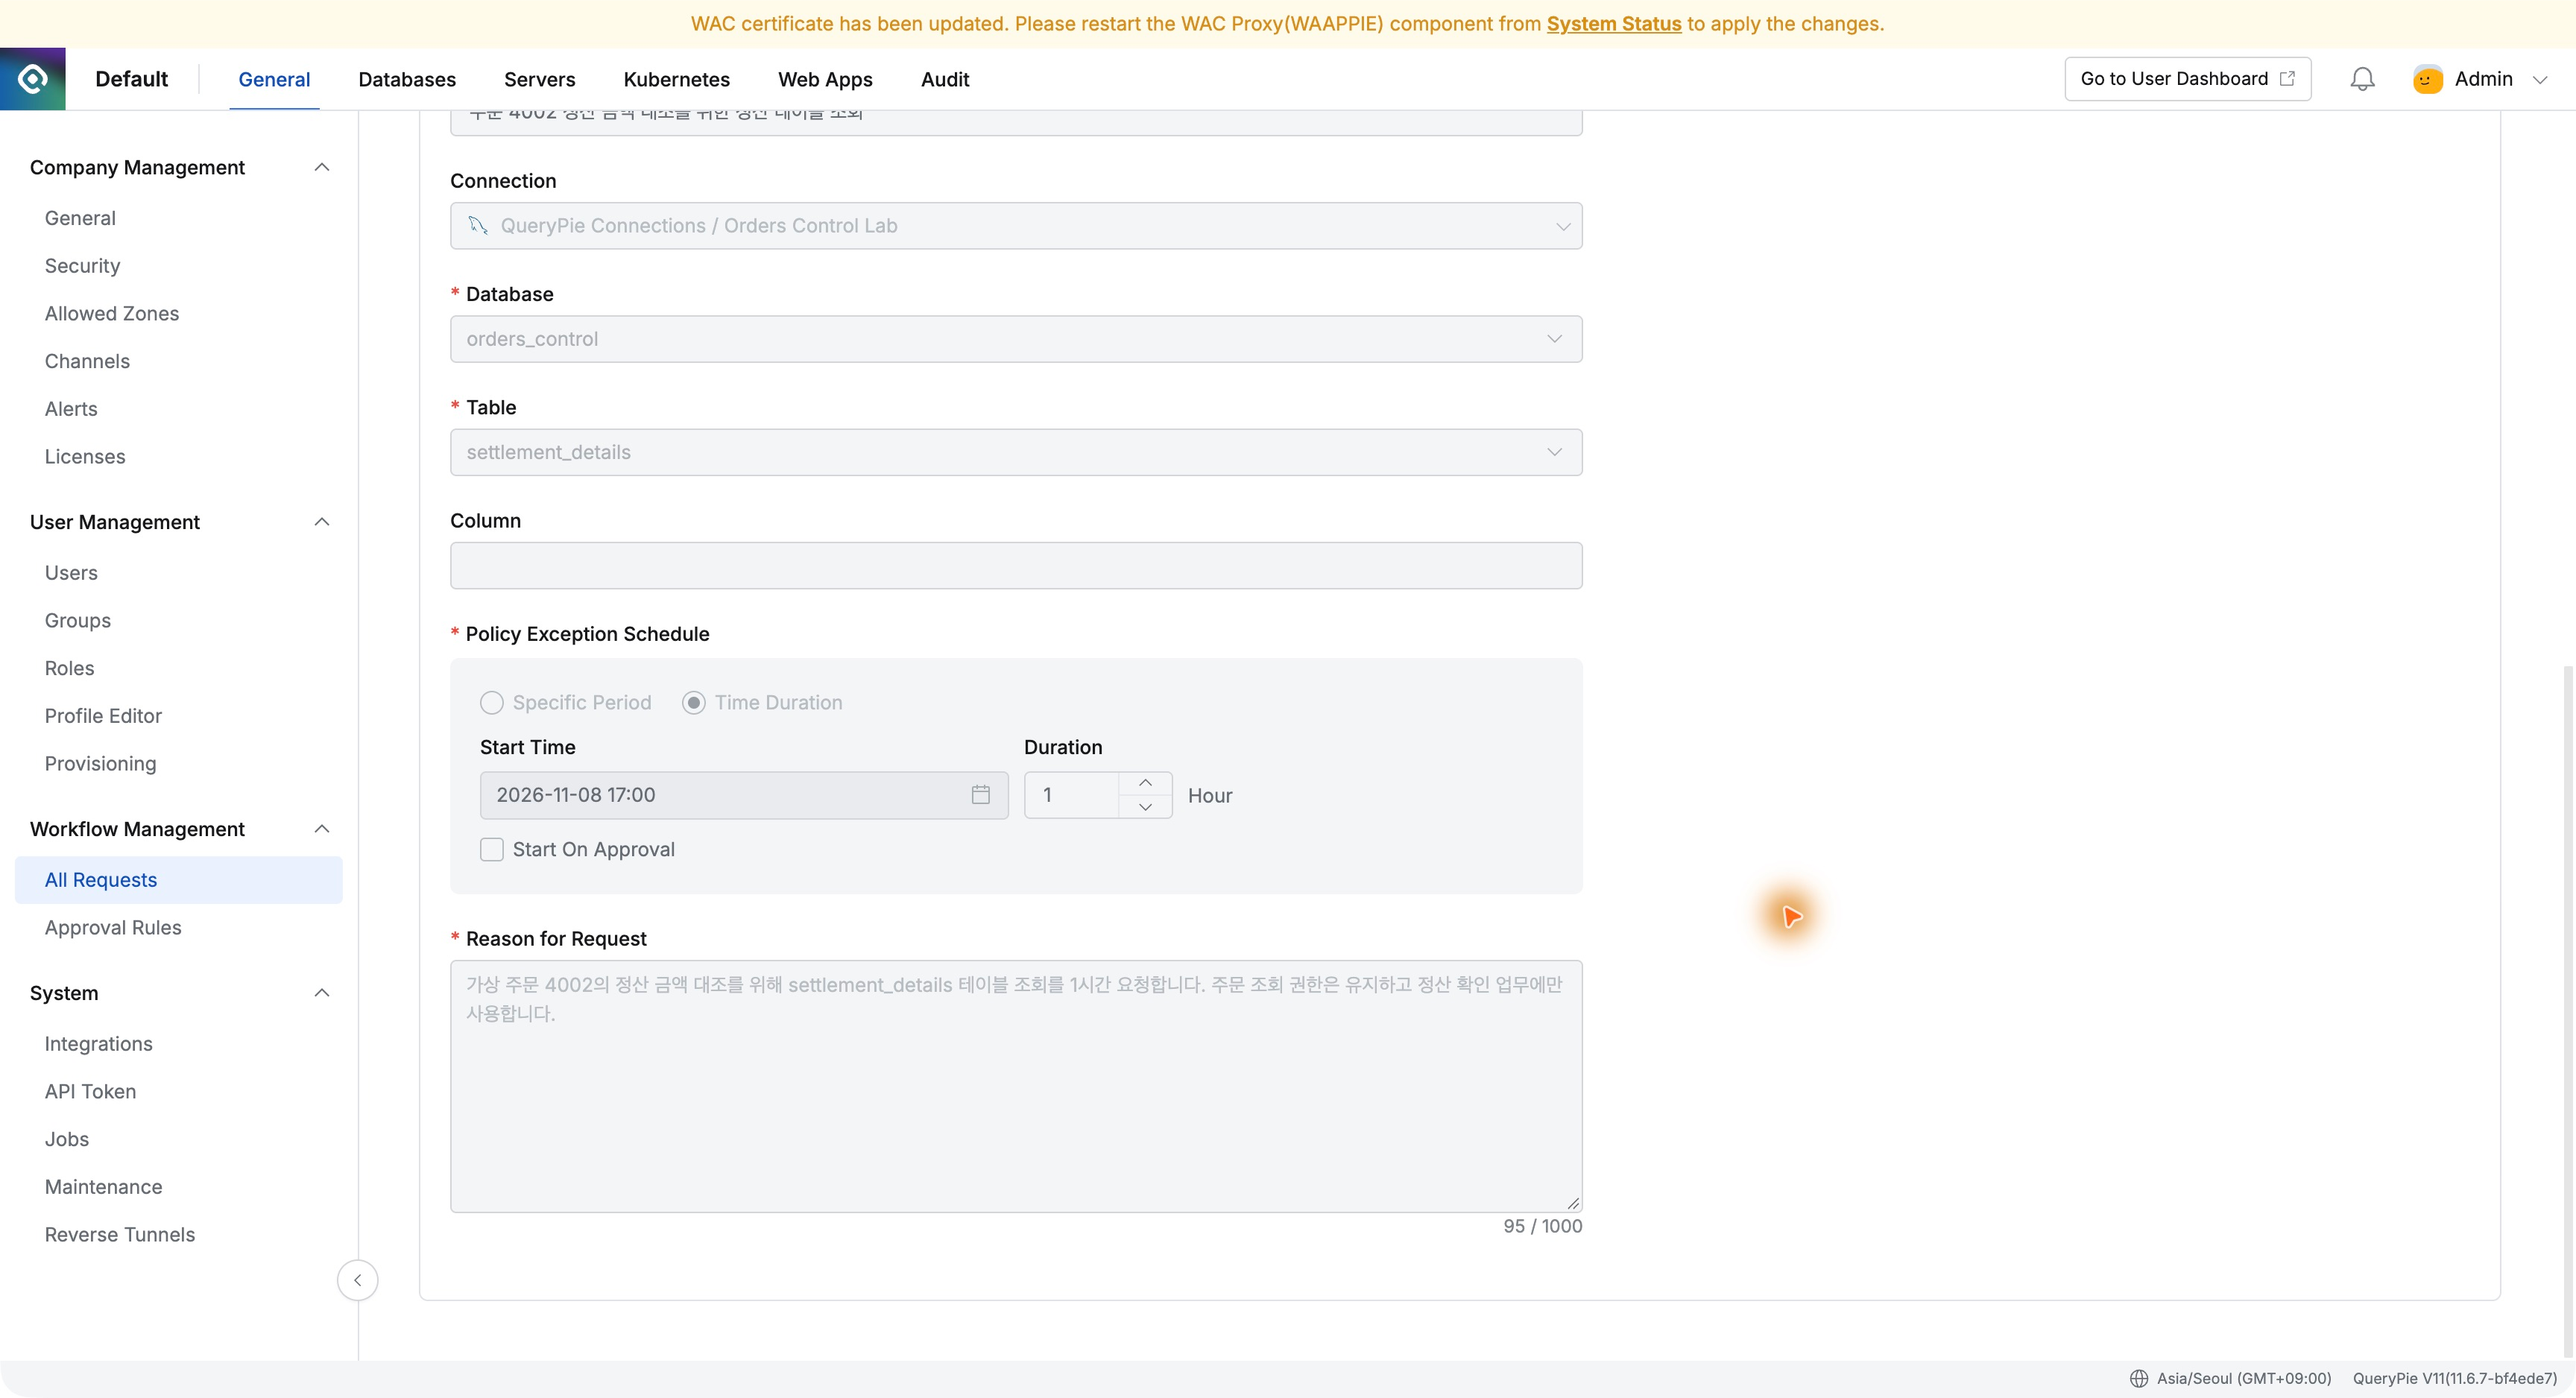
[Part 18] Temporary Access Needs an End Time Too — QueryPie Policy Exceptions
‘I just need a quick look at settlement amounts.’ Once access is granted, its end time needs managing too, so exceptions do not remain after work ends.
White Papers
Secure Server Access in an Era of Network Isolation: Multi-hop Bidirectional Tunneling via the SSH Protocol
As enterprises adopt network isolation, secure access to internal servers becomes more complex. This white paper outlines the limitations of traditional SSH methods and explains how QueryPie enables seamless, scalable server access through multi-hop tunneling and centralized control—without exposing intermediate credentials.
Blog
Healthcare Data Security: Protecting Patient Privacy and Ensuring Compliance
Discover how to safeguard healthcare data with advanced security measures, ensuring patient privacy, compliance, and protection from data breaches. Learn more now!
January 17, 2025
ACP Lab Notes
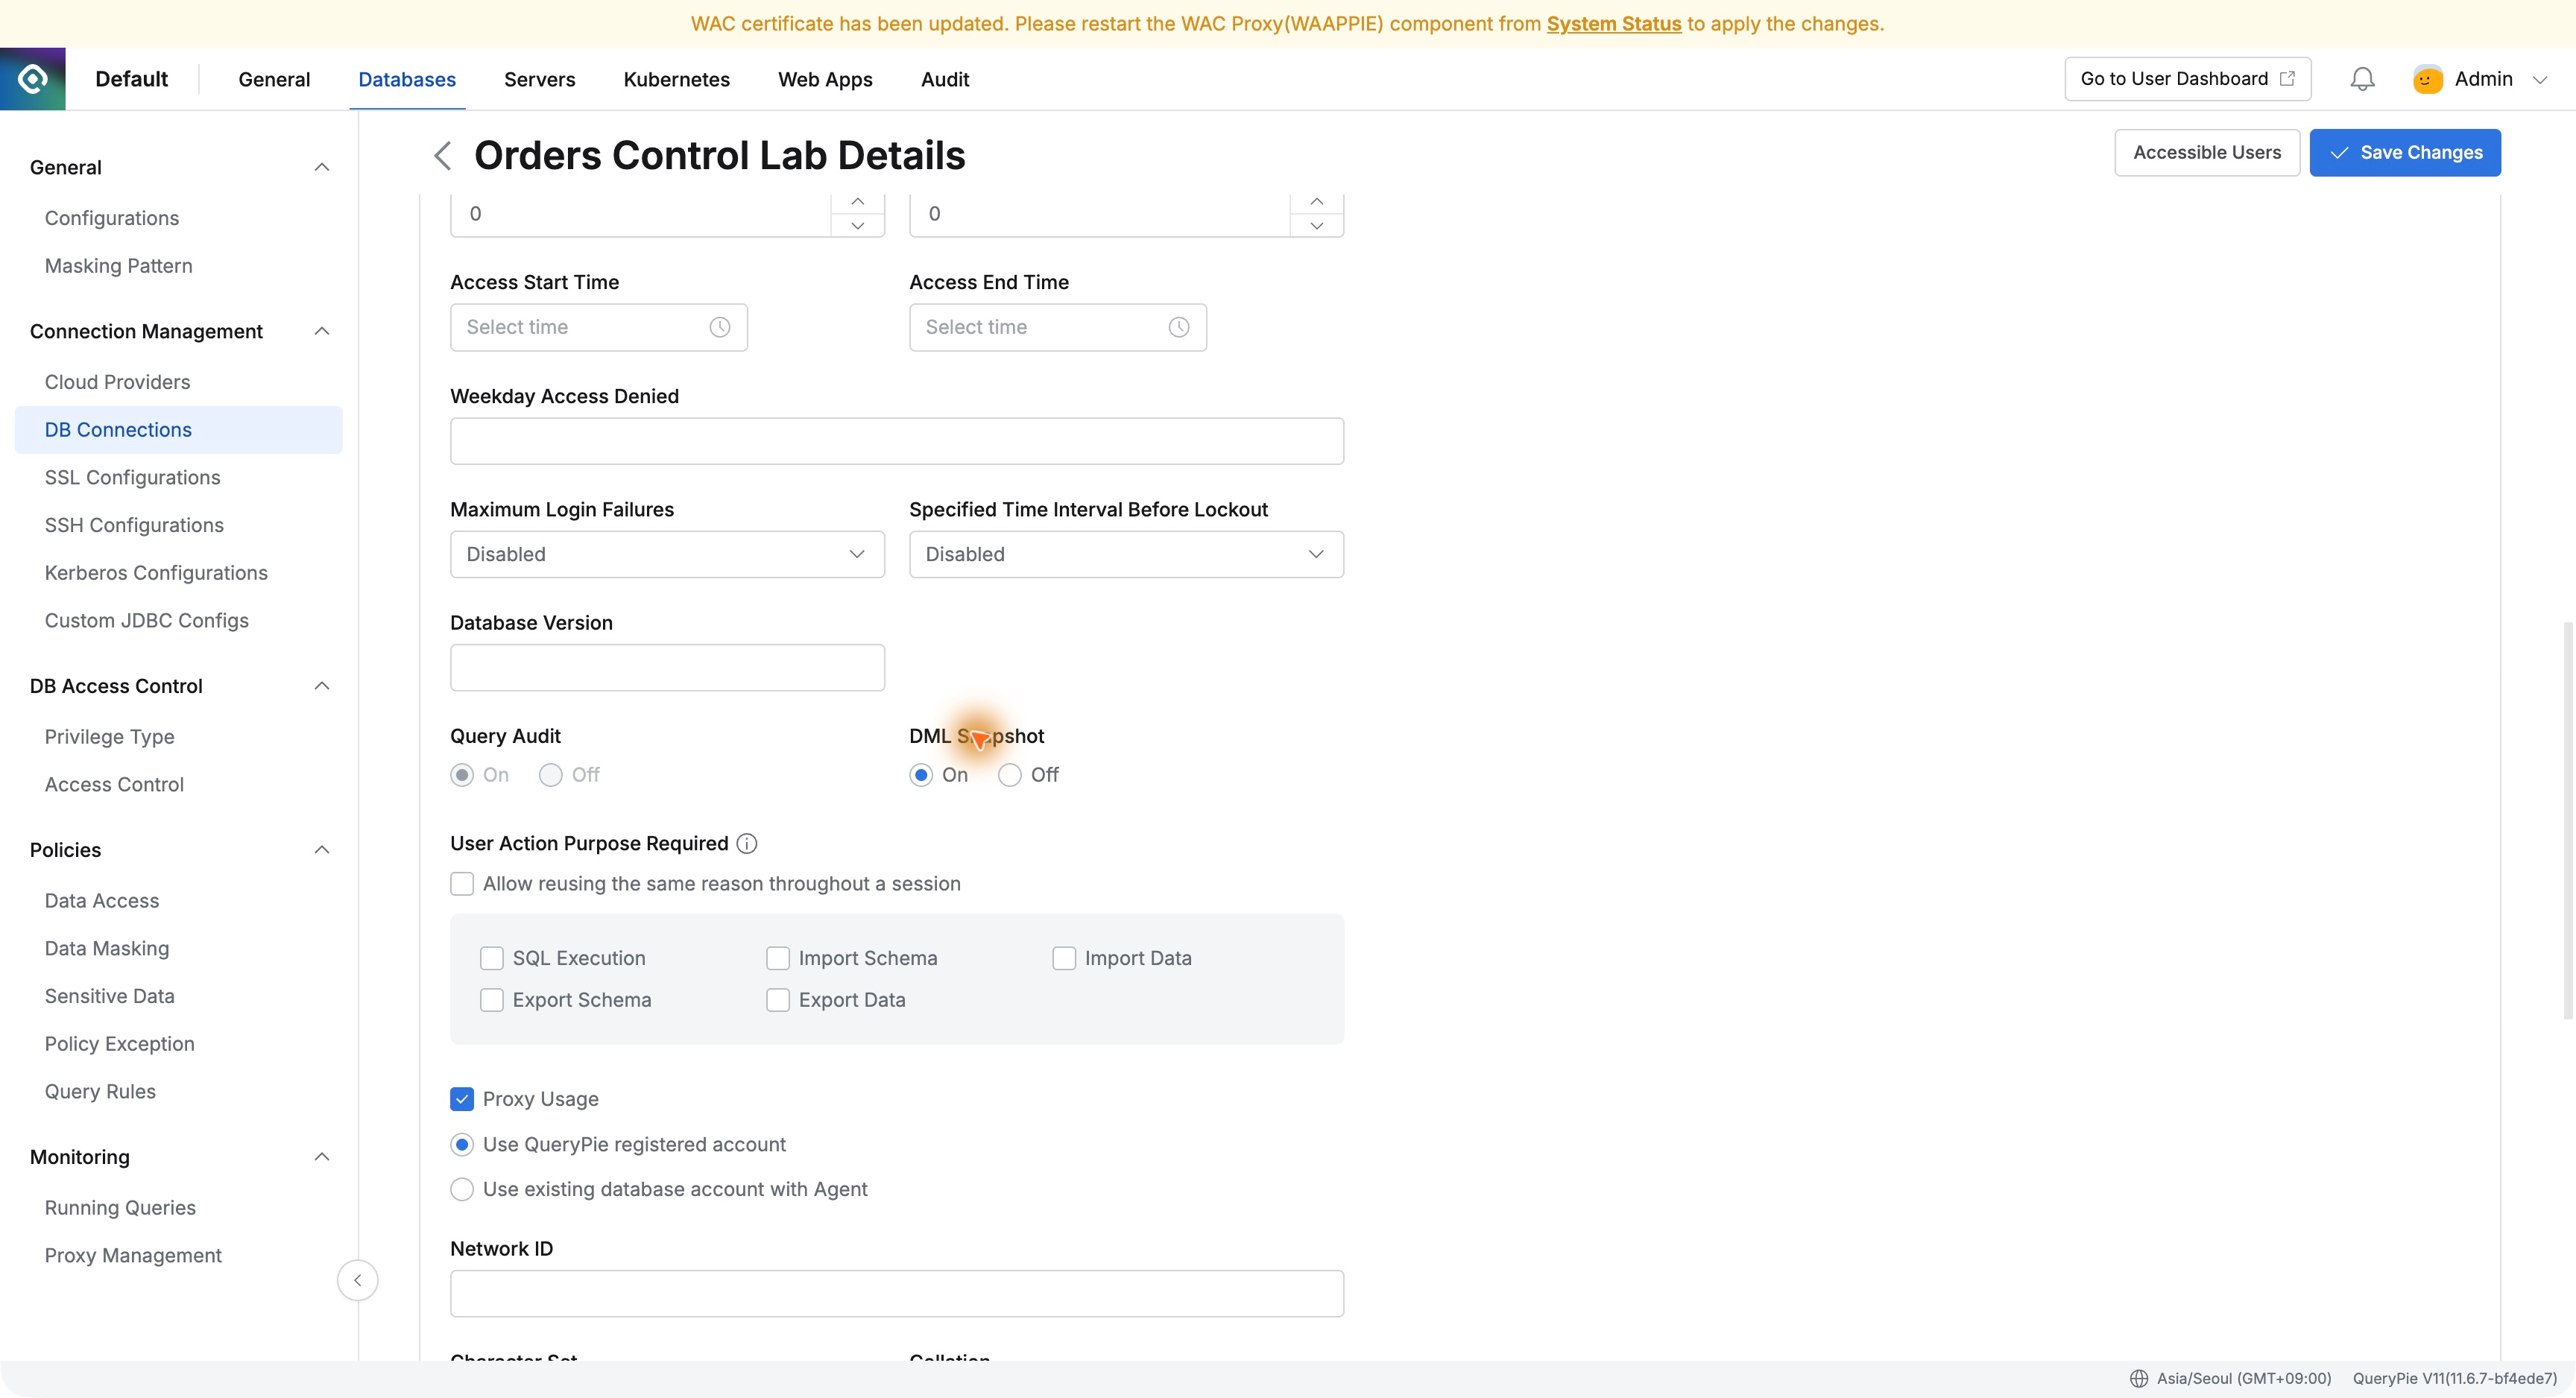
[Part 19] Finding the Previous Value After an Order Update — QueryPie DML Snapshot
Part 6 executed approved SQL without granting ongoing write access. Now I wanted to see not only who ran SQL, but how the data actually changed. I changed a fictional order from PENDING to DELIVERED and inspected DML Snapshot.
White Papers
Optimal Method for Using a Terminal with Seamless SSH Connection
Discover an optimal method for seamless SSH connections that enhances security without disrupting the CLI workflow. Learn how QueryPie’s approach eliminates the need for additional agents while maintaining robust access control.
Blog
Zero Trust Security: Redefining Cybersecurity in a Hyper-Connected World
Understand how Zero Trust Security can protect your business by continuously verifying users, devices, and networks, ensuring stronger defense against threats. Explore it now!
January 16, 2025
Events
Ep. 4 QueryPie KAC: Kubernetes One Strike!—Multi K8s clusters, yap! K8s resources, yap! Pod access history, yap!
In Episode 4, we explored how to maintain a robust security environment in Kubernetes using QueryPie's Kubernetes access control solution, 'QueryPie KAC (Kubernetes Access Controller)'.
November 29, 2024
ACP Lab Notes
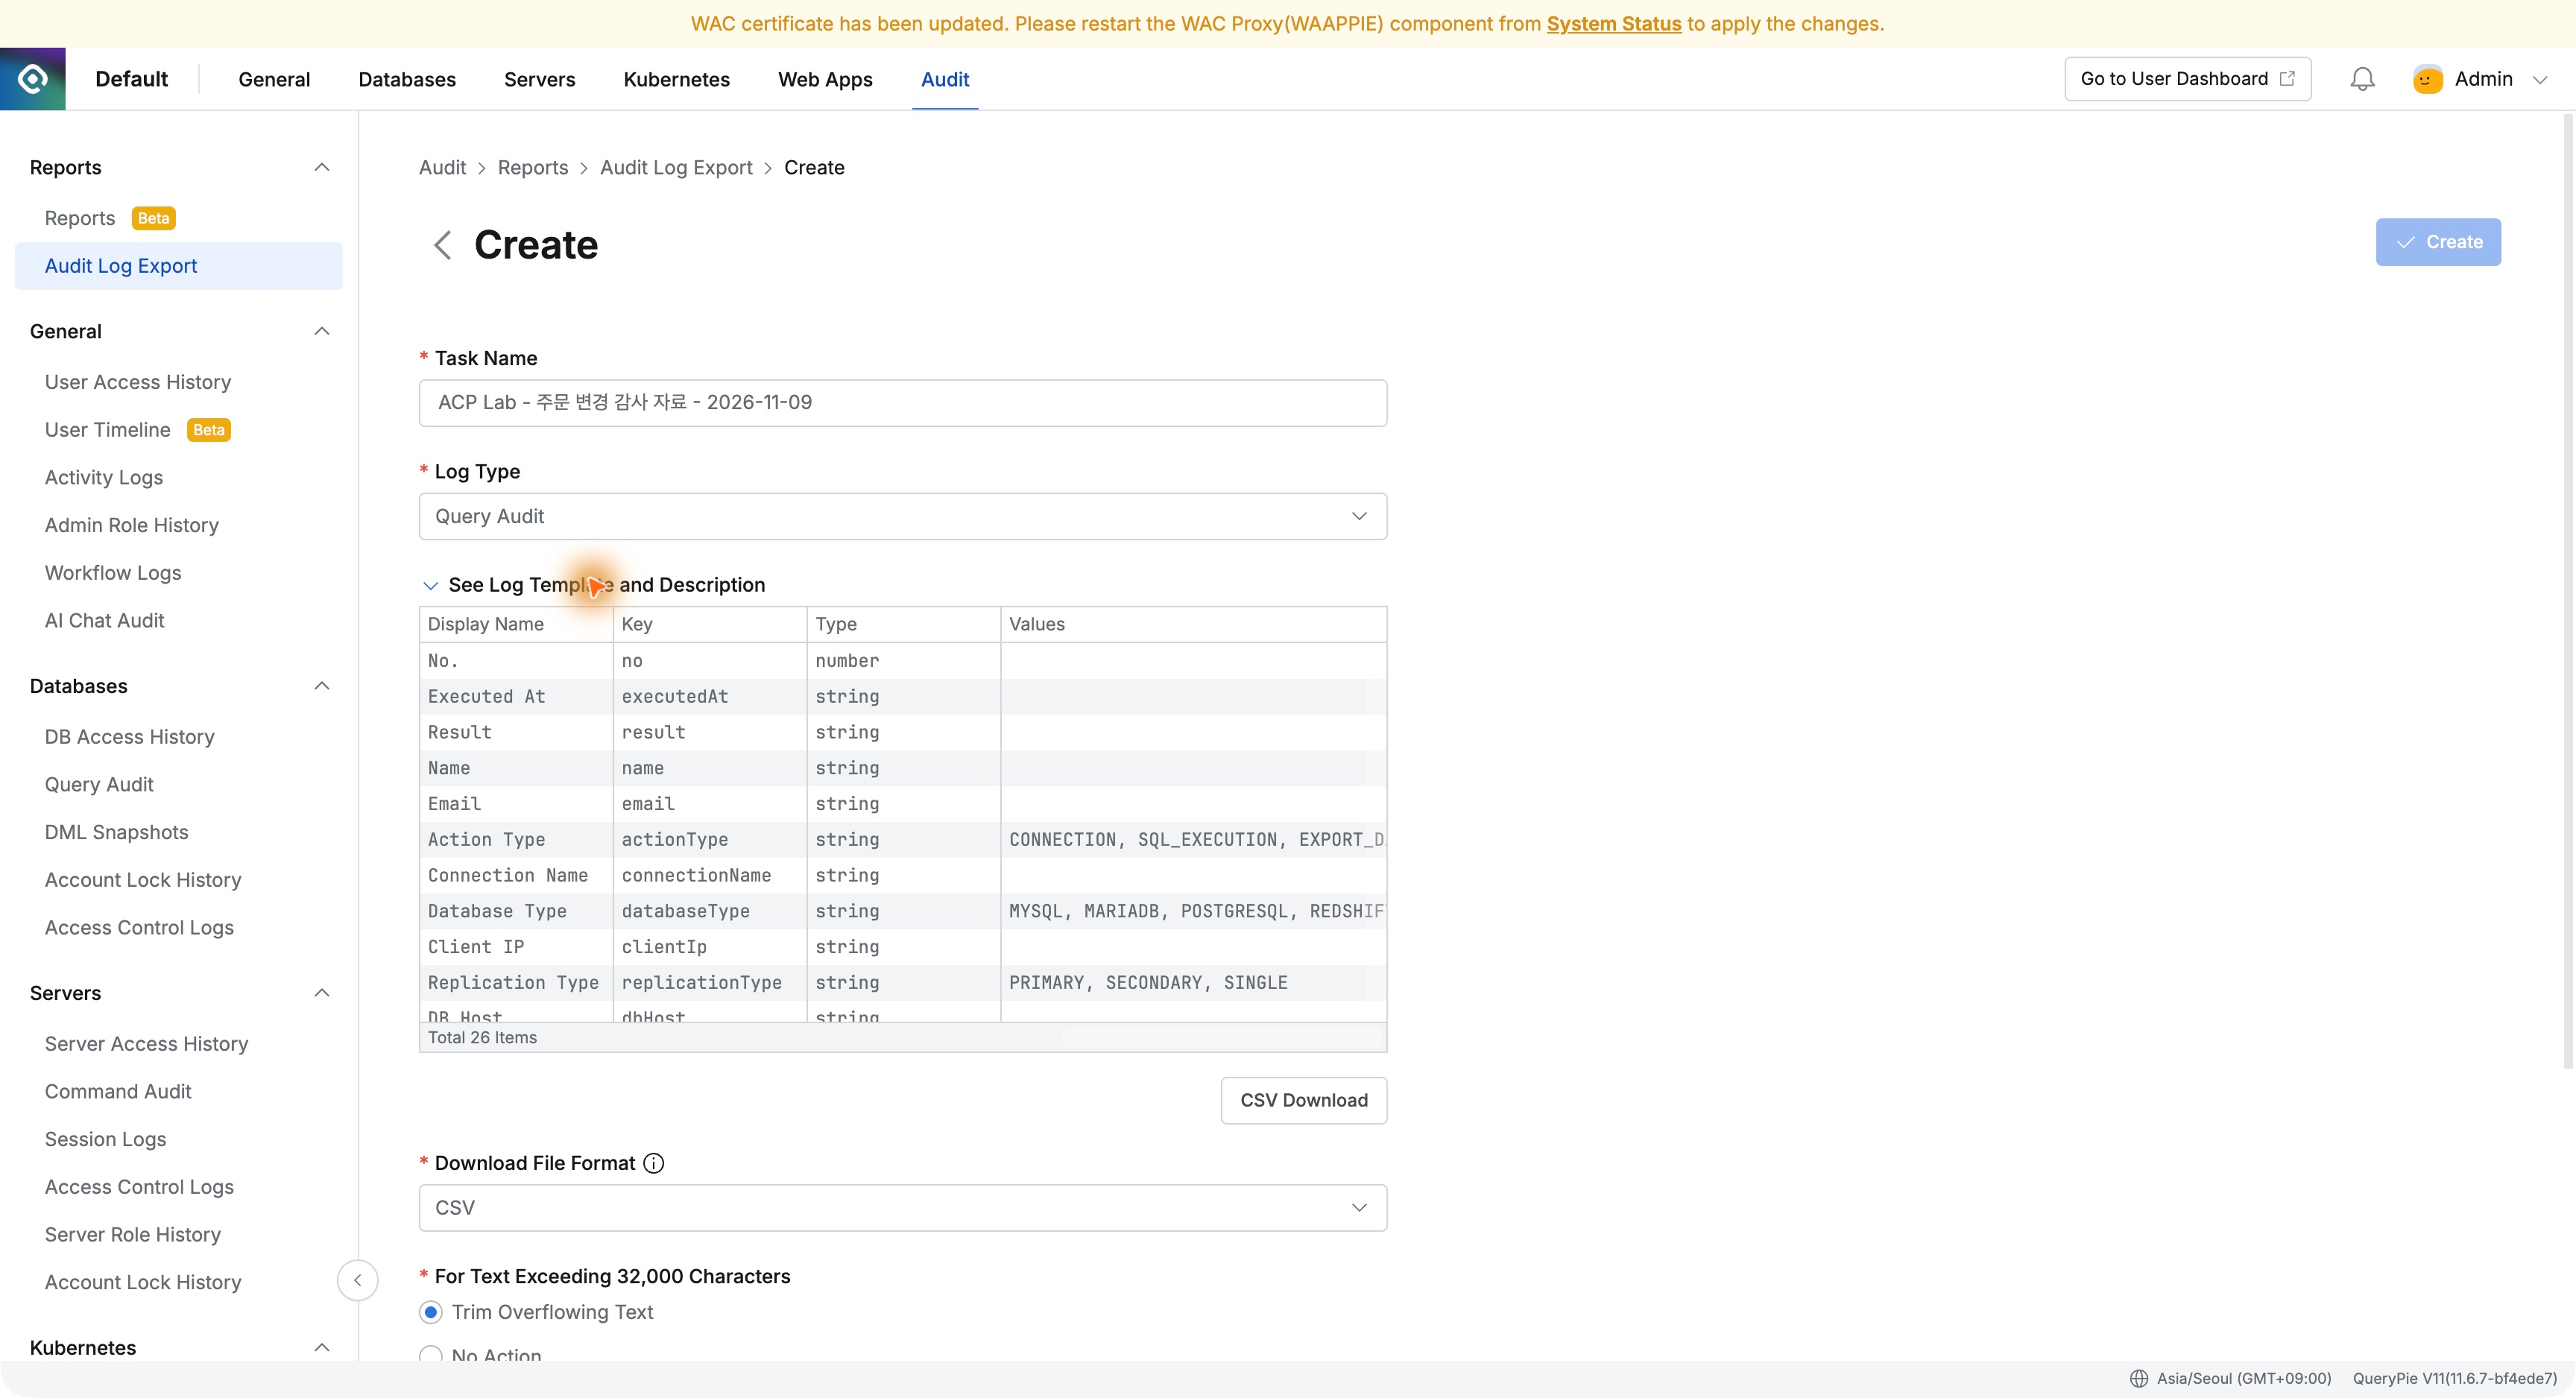
[Part 20] Selecting the Records an Audit Needs — QueryPie Audit Log Export
Part 19 inspected order values before and after a change. Here, I exported the activity records to support an audit or internal review of a particular user’s database work. Filtering by period and user gathered both the read and approved update, with SQL, outcomes, and workflow UUID.
White Papers
QueryPie gRPC DAST Security: ZAP Custom Script Example
Learn how QueryPie leverages gRPC communication for high performance and stability in web applications.
Blog
Mastering Data Observability: Insights, Techniques, and Best Practices
Understand QueryPie's commitment to an agentless approach for streamlined and secure system management.
January 9, 2025
ACP Lab Notes
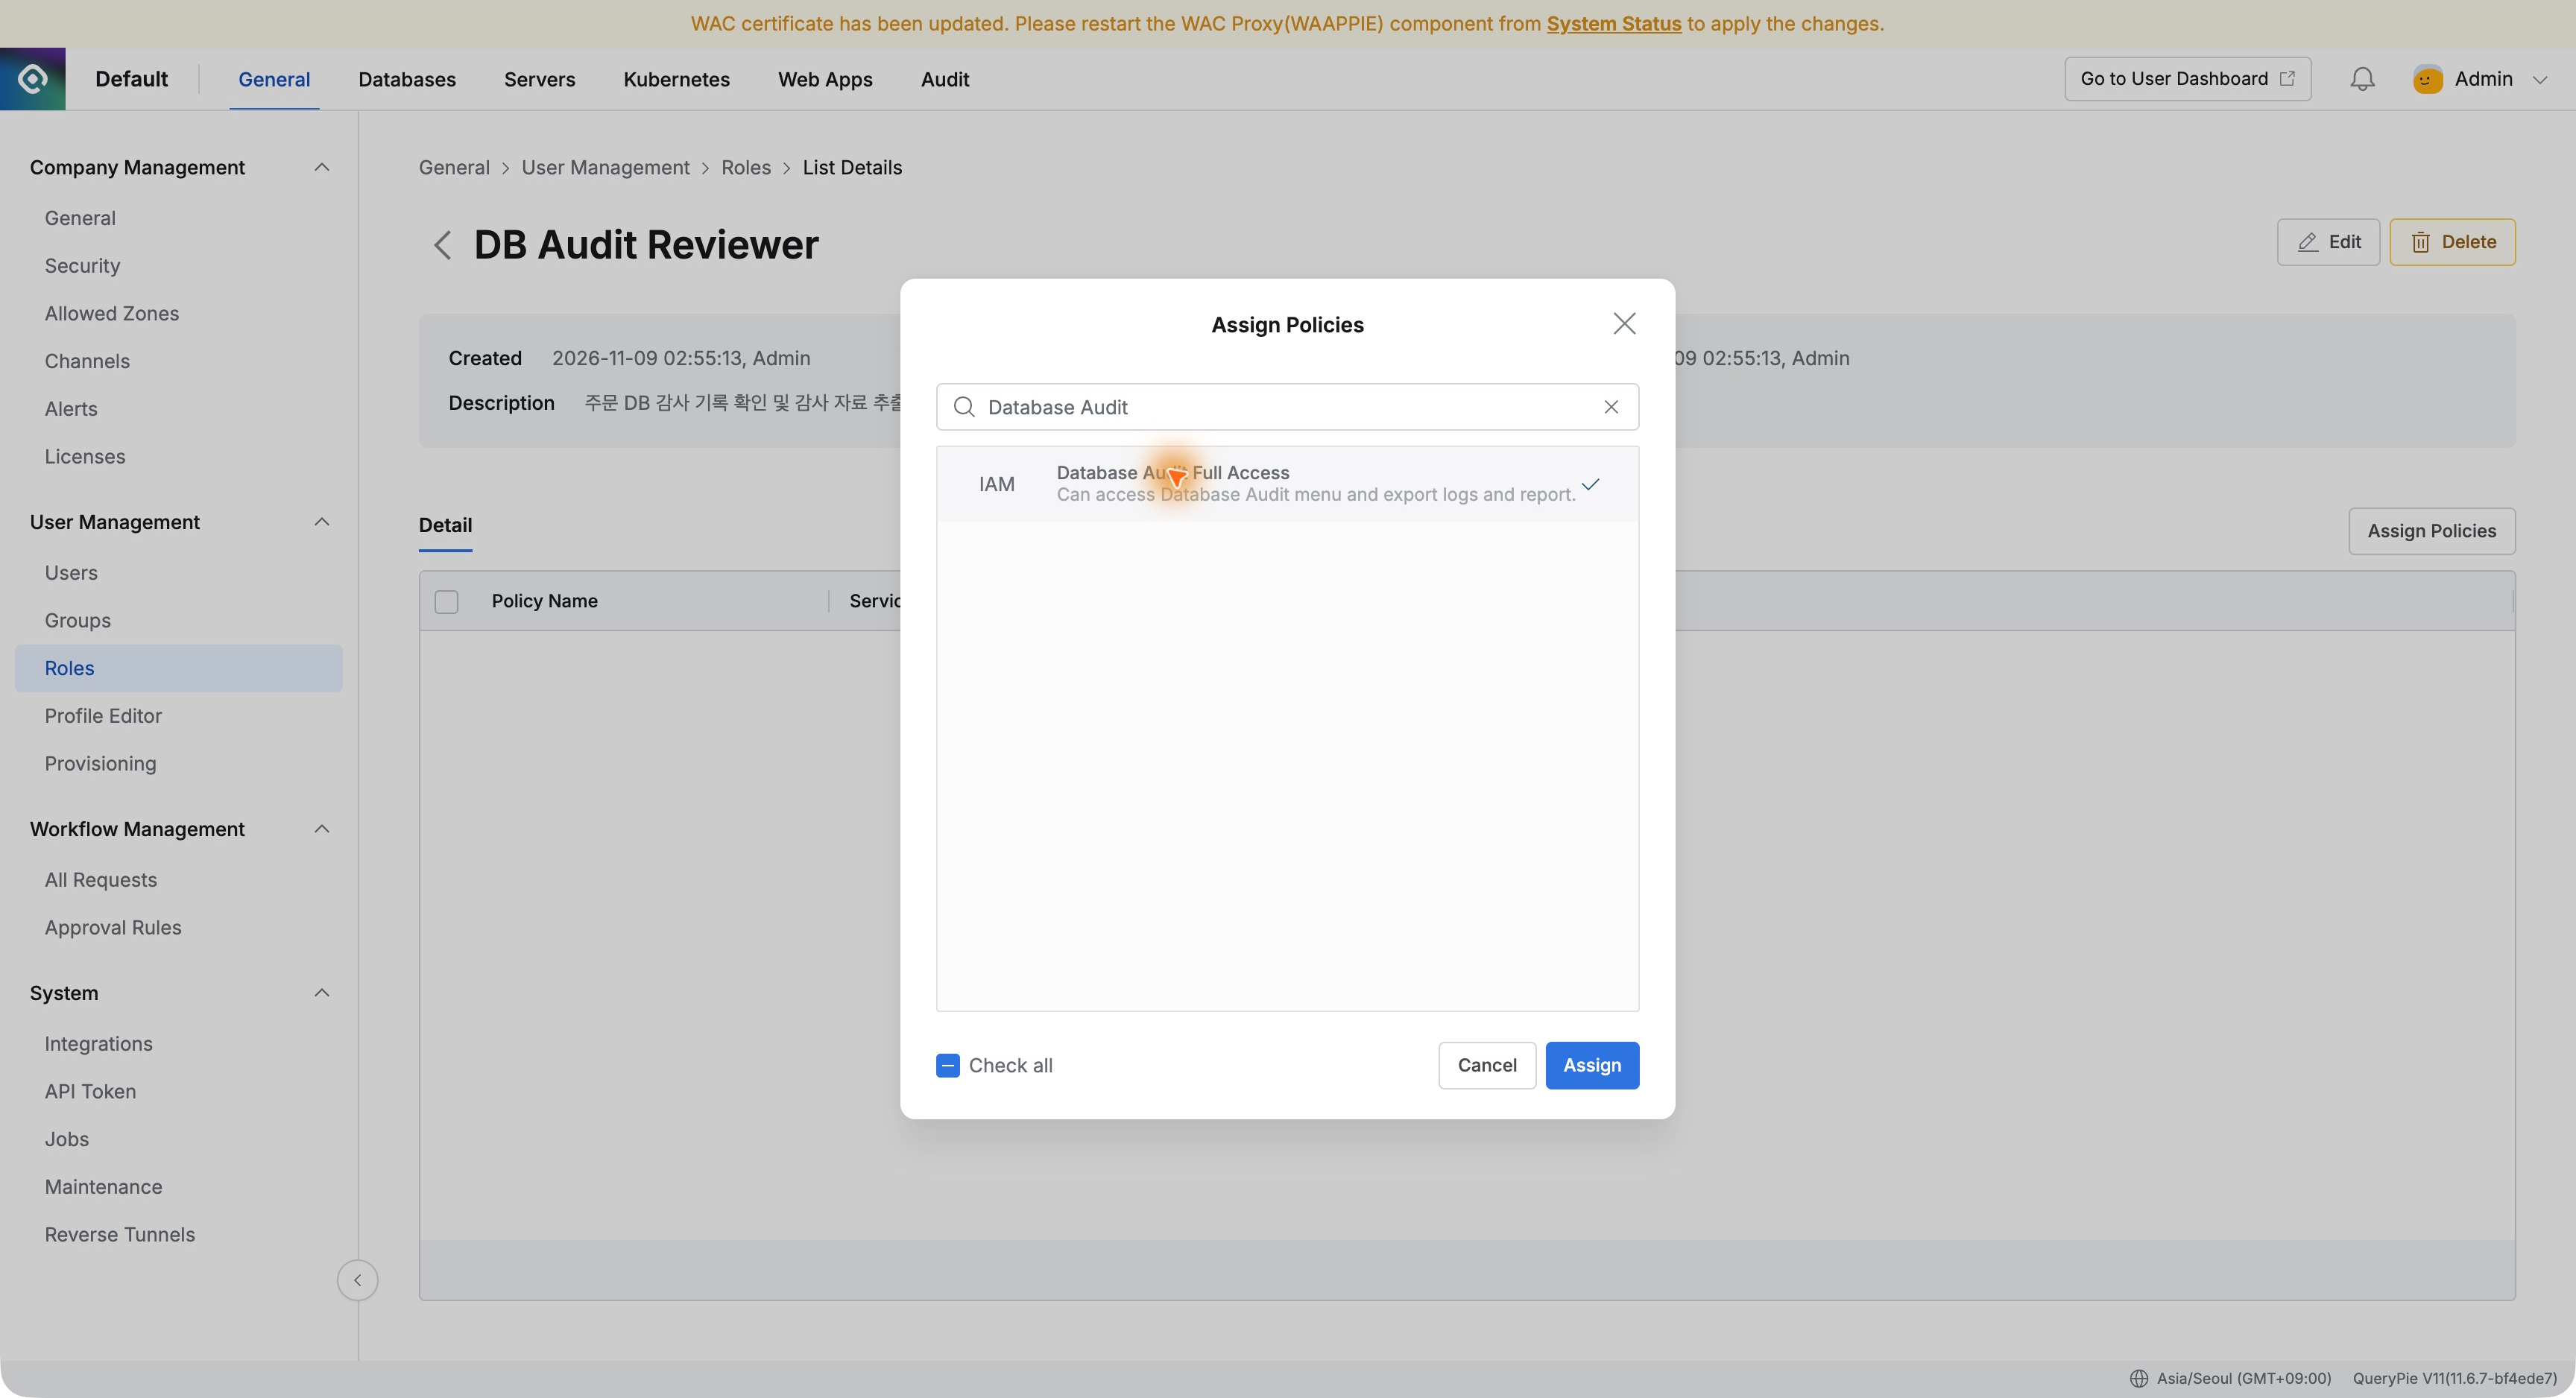
[Part 21] Giving Auditors Only the Access They Need — Separating QueryPie Administrator Roles
Previously, an administrator reviewed and exported database audits. In production, configuration and audit review may belong to different people. I created an auditor role that could inspect changes, DML snapshots, and downloads, while database configuration remained inaccessible.
White Papers
Efficient Storage and Management of Large-Scale Audit Logs (OVEN)
Guiding efficient storage and management of large-scale audit logs while meeting security and compliance requirements.
Events
Ep. 3 QueryPie SAC: Smashing Server Management Hurdles!—Mass Server Management, Yap! Auto-Scaling, Yap! Permissions and Policies, Yap!
In Episode 3, we took a close look at how to efficiently manage numerous permissions across a large number of servers and multi-cloud environments using QueryPie's system access control solution, 'QueryPie SAC (System Access Controller)'.
November 29, 2024
Blog
What businesses can learn from Sentiment Analysis
Learn how sentiment analysis can boost your business by understanding customer emotions, refining strategies, and enhancing satisfaction. Explore its power today!
April 26, 2022
ACP Lab Notes
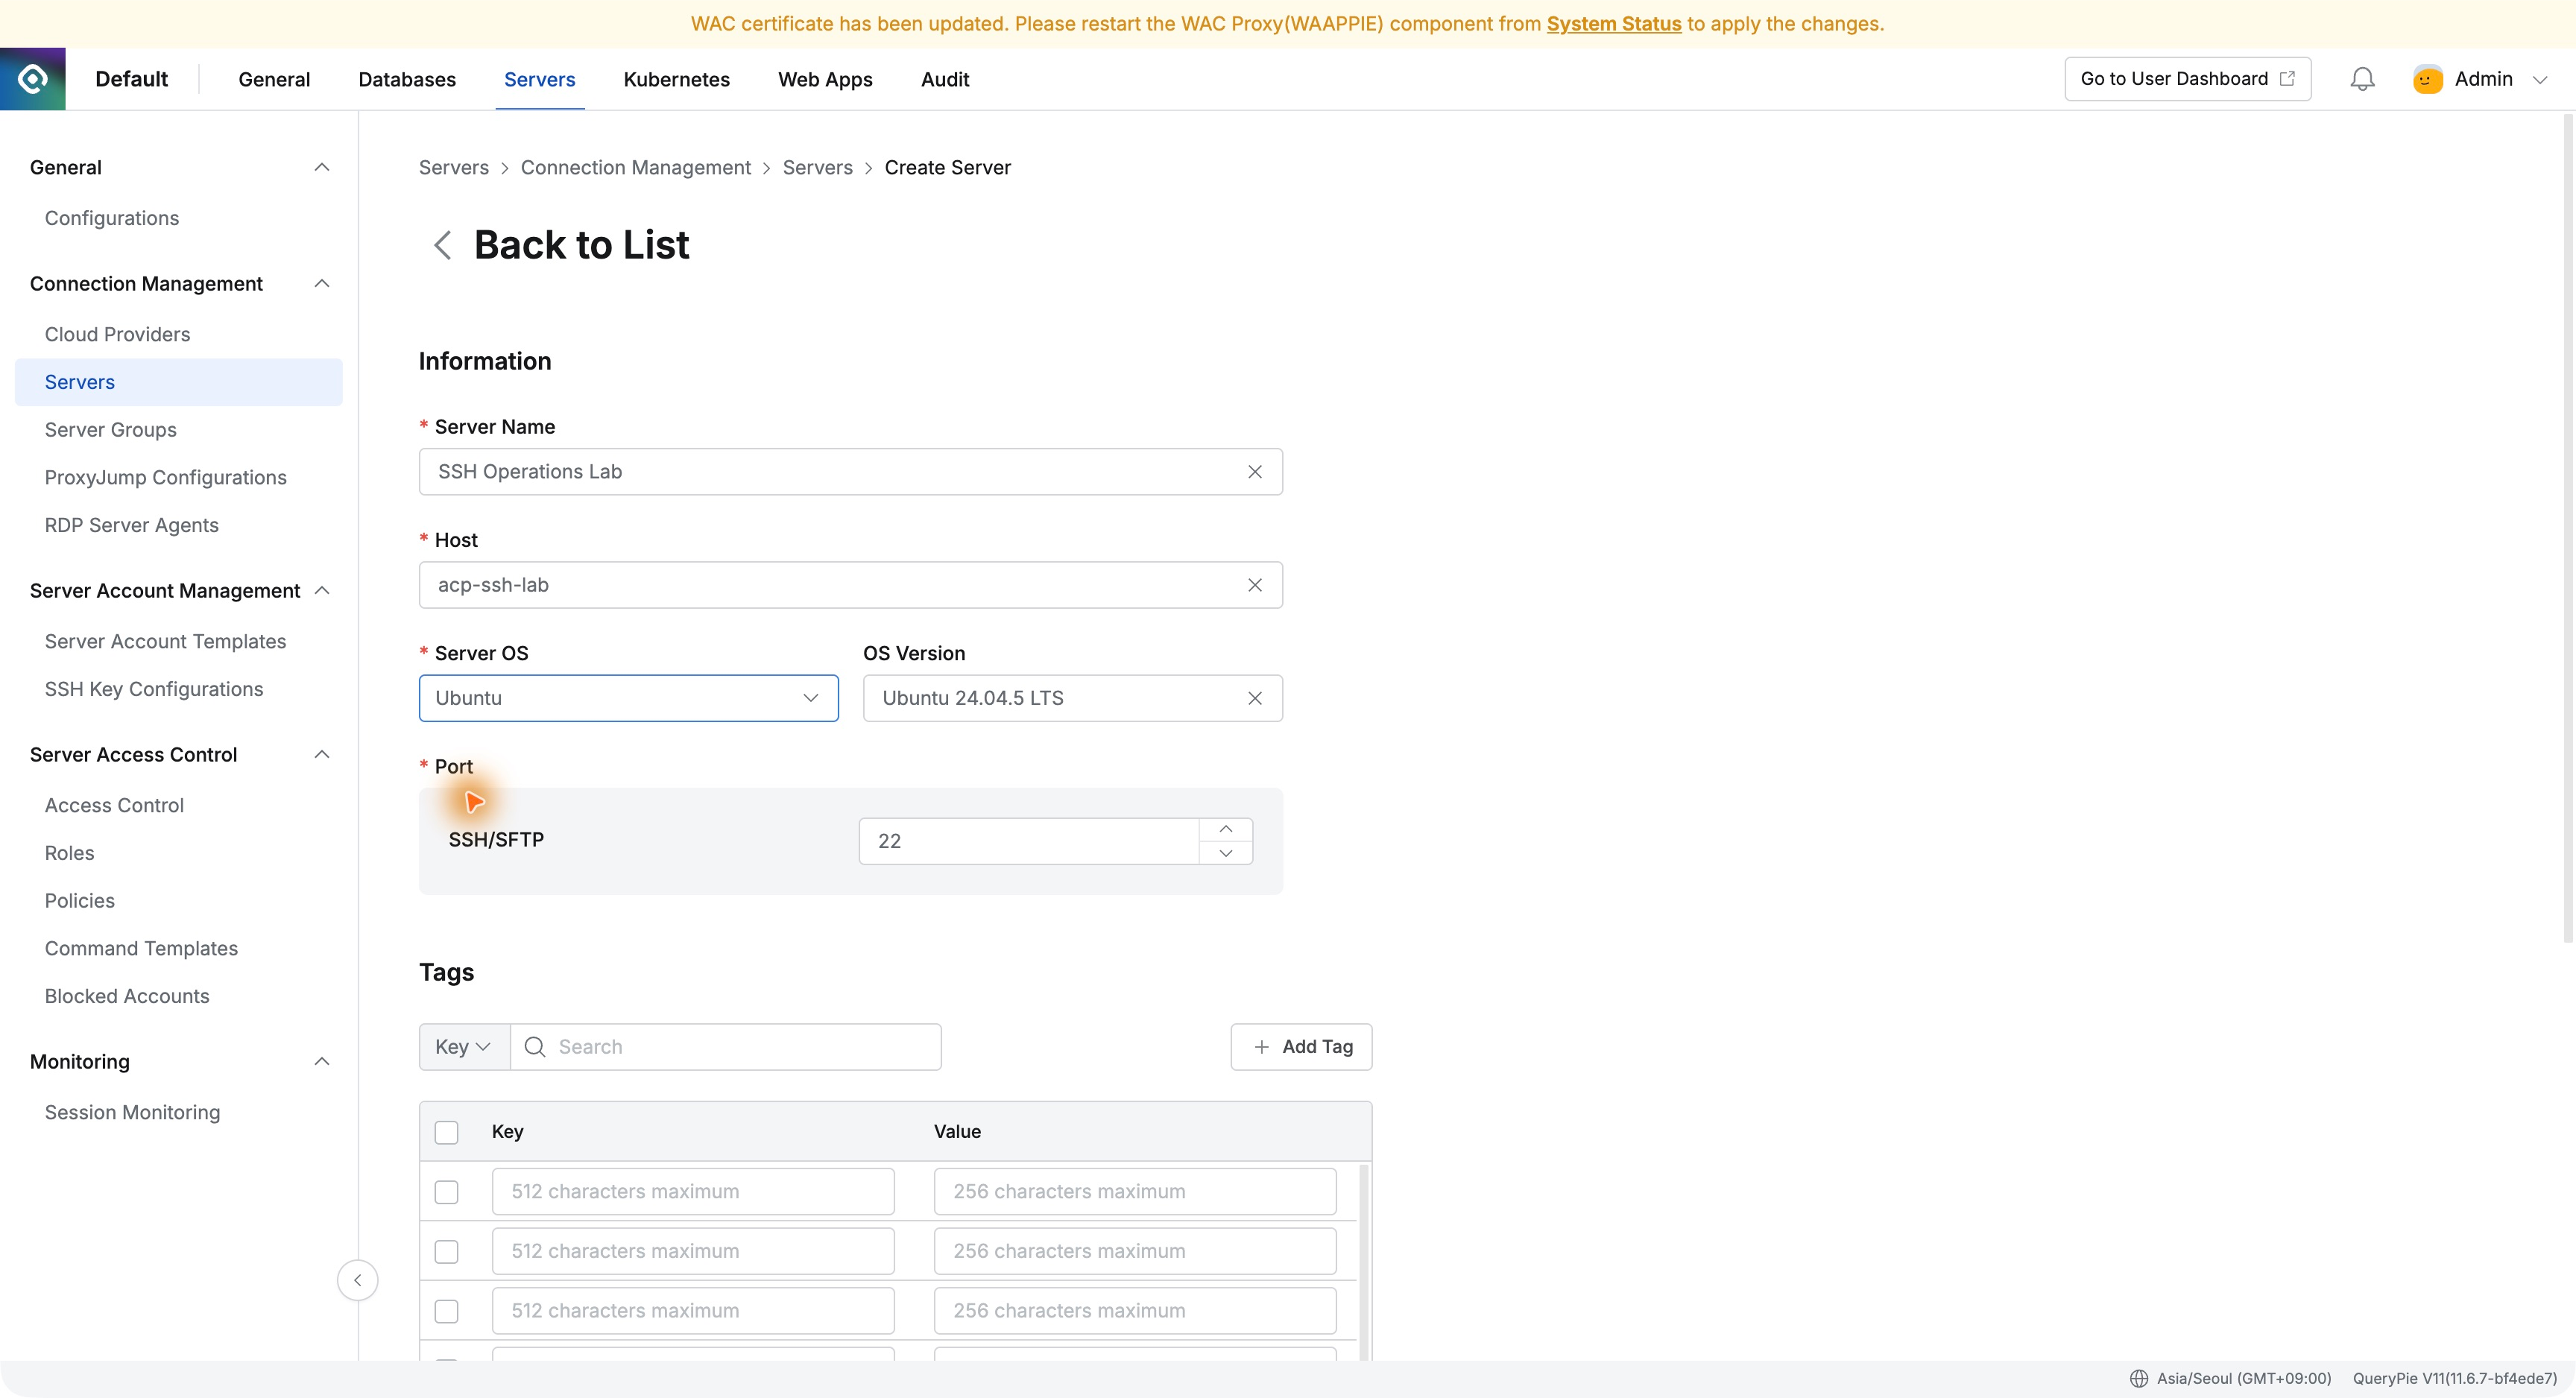
[Part 22] Connecting to SSH Without Entering the Server Password — QueryPie Web Terminal
After exploring database work, I moved to servers. Instead of distributing passwords to each new operator, I registered a test Ubuntu server and assigned an SSH role in QueryPie. The developer signed in, chose server and account, and opened a browser terminal without entering its password.
Blog
Data Leaks: How a Small Internal Breach Can Turn into a Disaster
Explore how small internal breaches can escalate into major data leaks and how QueryPie helps mitigate risks effectively.
November 22, 2024
White Papers
QueryPie’s DevSecOps Pipeline: Proven to Enhance Development Speed and Stability
Streamline development with QueryPie's DevSecOps pipeline for enhanced speed, stability, and security.
ACP Lab Notes
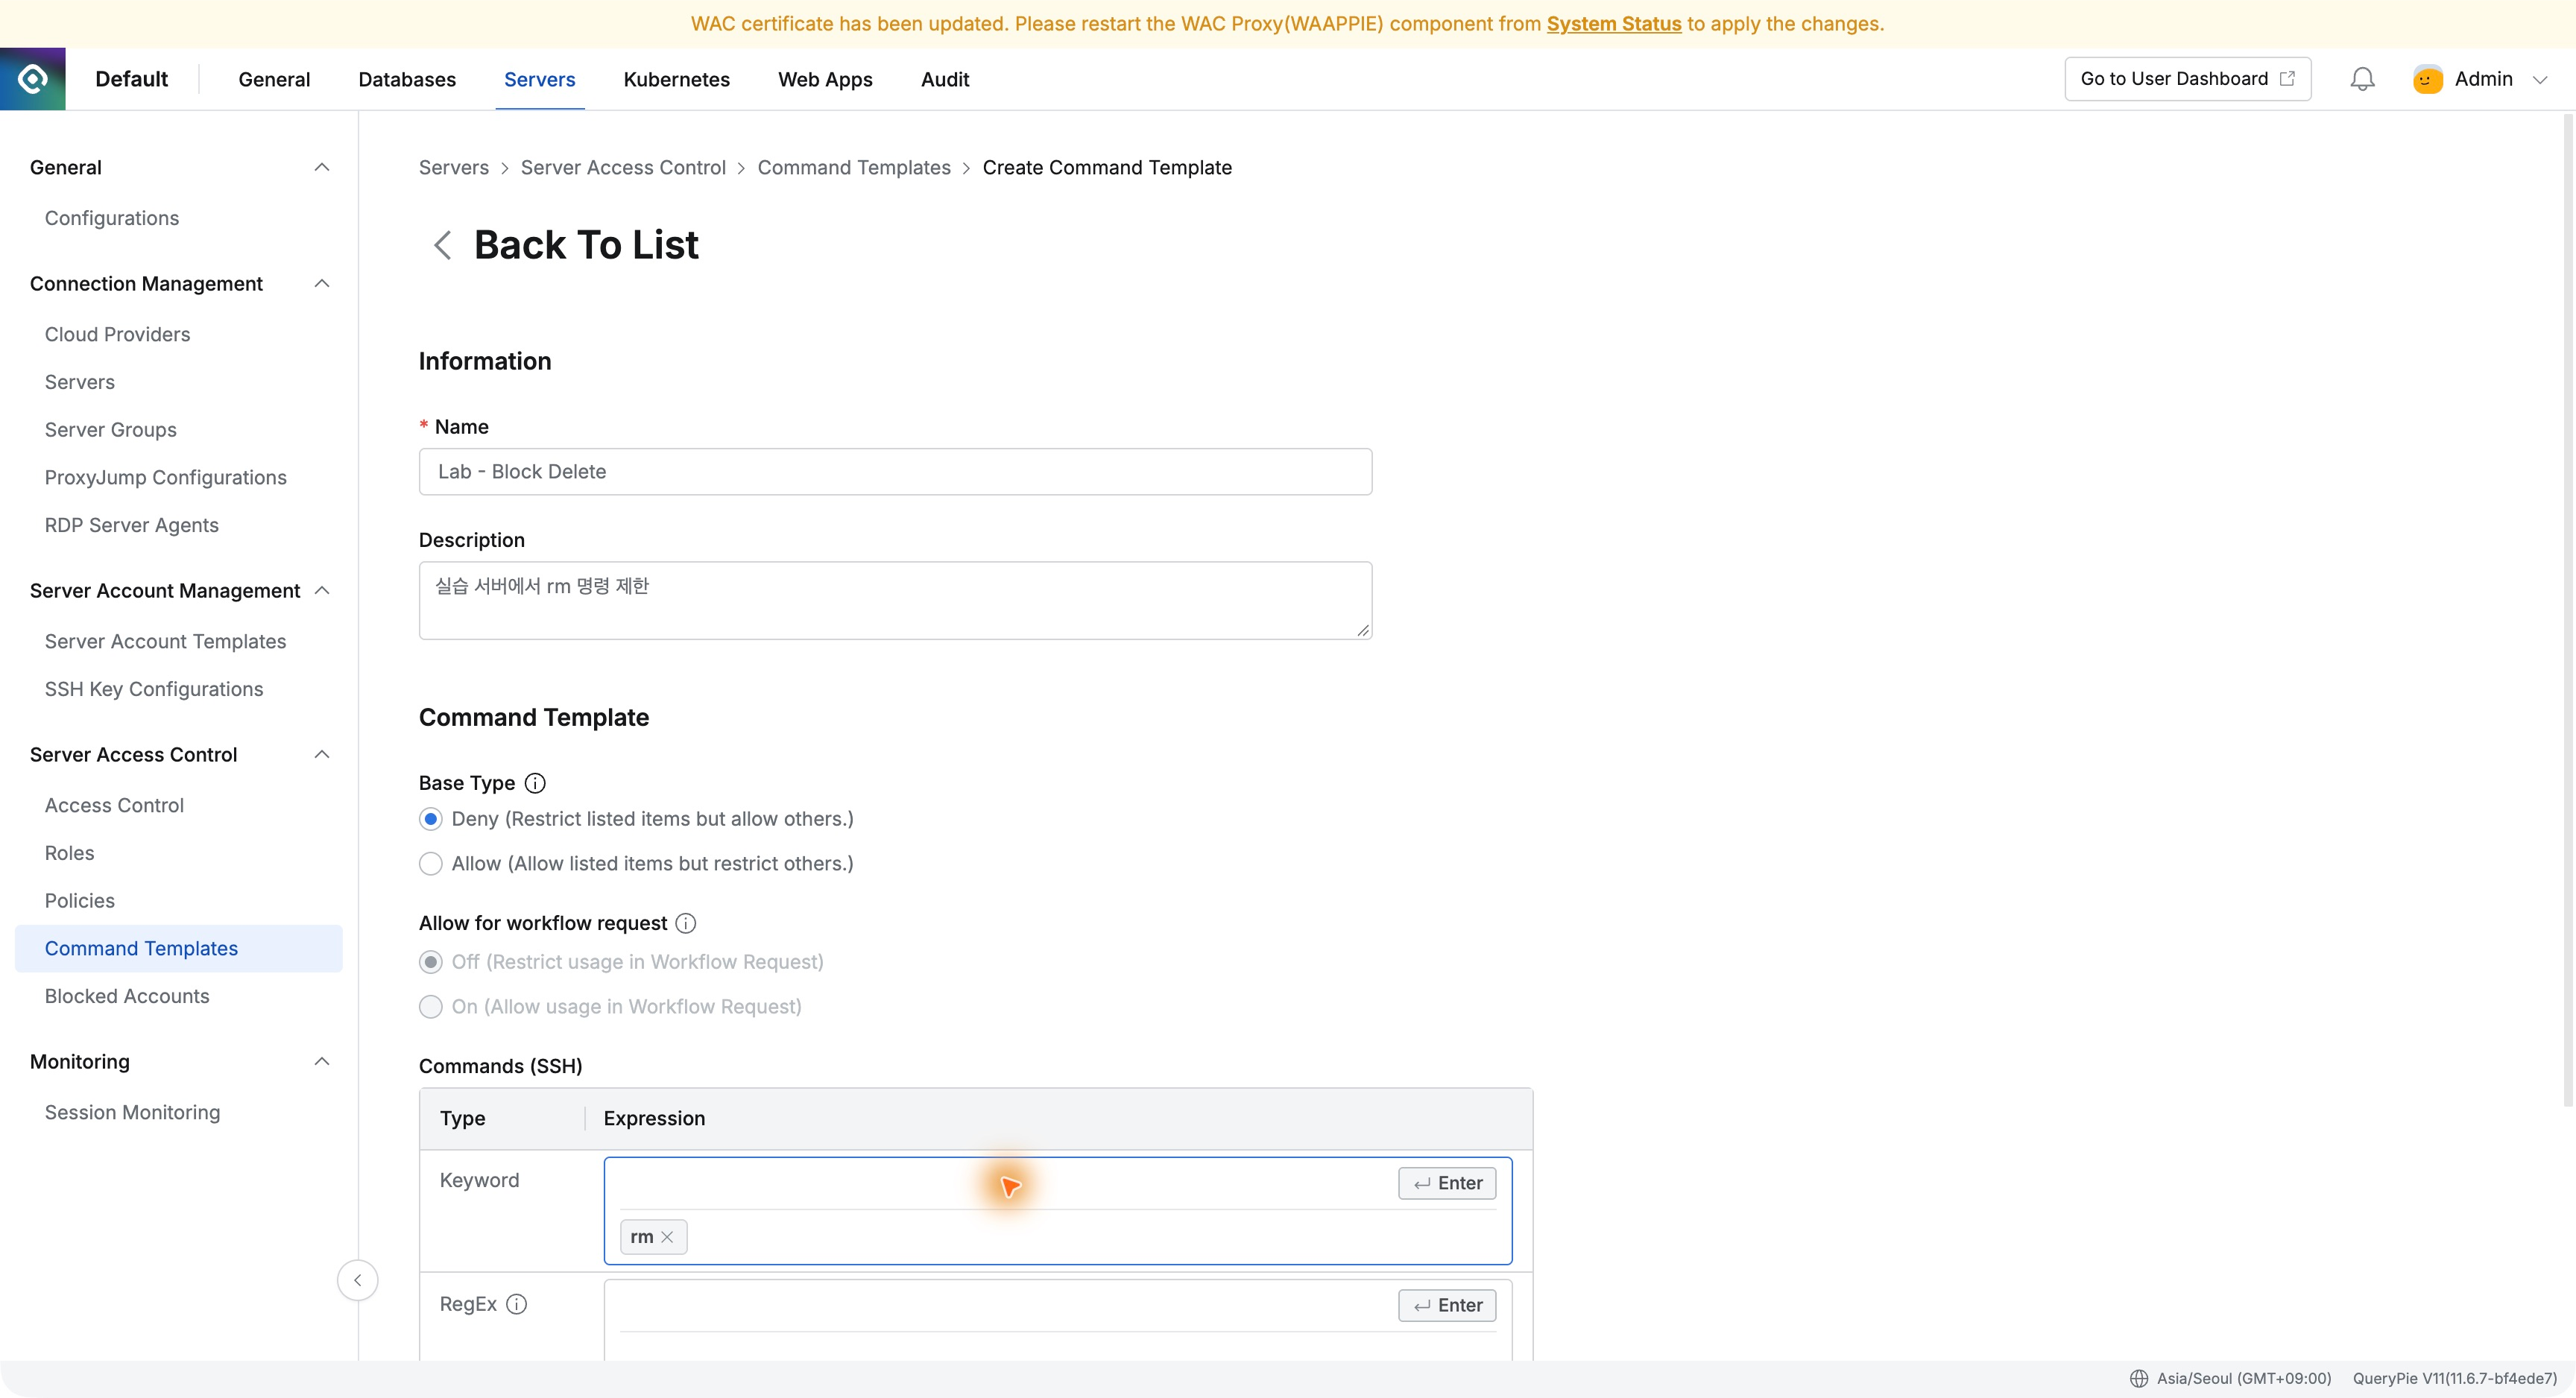
[Part 23] Allowing Server Access but Blocking Deletion — QueryPie Command Control
After password-free web-terminal access, I restricted commands after login. The operator should inspect account and file contents but not delete files with rm. I prepared a test file and applied Command Templates.
Events
Ep. 2 QueryPie DAC: Crushing DB Concerns!—DB Integrated Management, Yap! NoSQL, Yap! Ledger Data, Yap!
QueryPie's DB Access Control (QueryPie DAC) plays a central role in strengthening security for accumulated sensitive information and enabling convenient access control and management to ensure security stability. We explored methods for reliably managing vast amounts of sensitive information and data in a multi-cloud environment.
November 29, 2024
Blog
QueryPie x Figma: The Ultimate Guide to Seamless Collaboration
Discover how QueryPie and Figma ensure seamless collaboration for design and development teams, boosting productivity.
November 22, 2024
White Papers
QueryPie’s New Standard for Penetration Testing
QueryPie sets a new benchmark in penetration testing to prevent vulnerabilities and secure systems effectively.
White Papers
Secure Login Token Management: An Essential Frontend Strategy
Secure user authentication with QueryPie's login token management, enhancing frontend security and data protection.
ACP Lab Notes
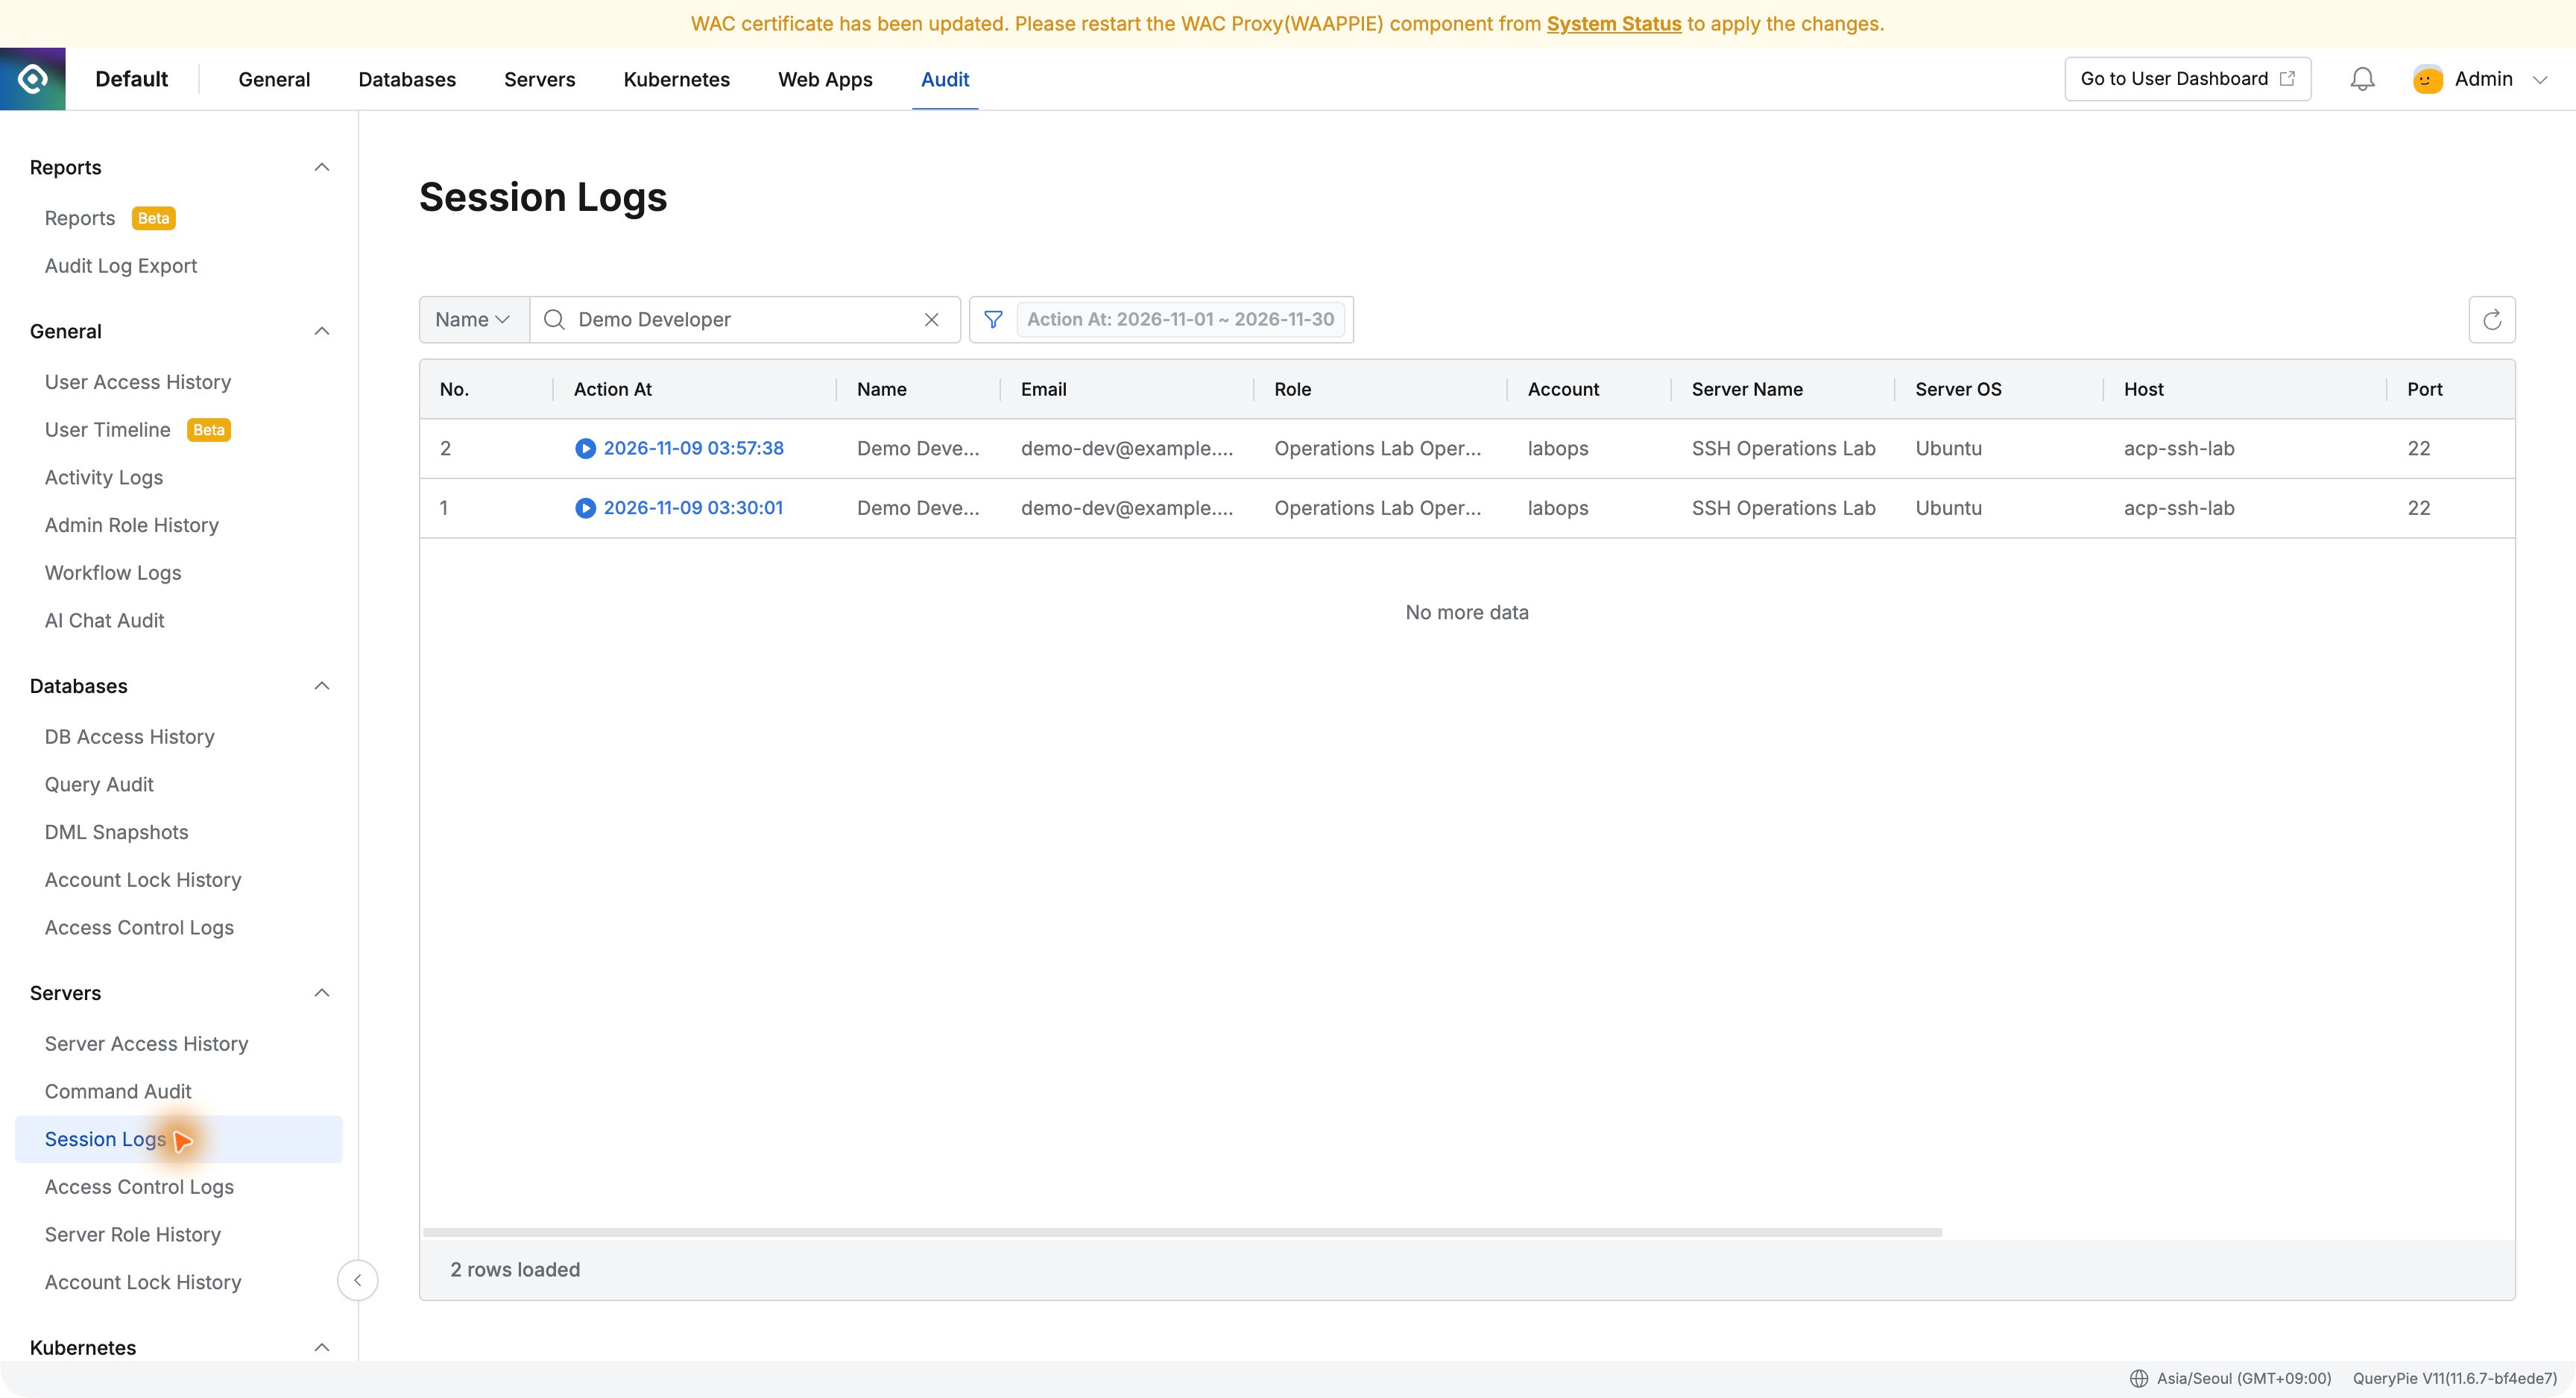
[Part 24] Replaying Work Done on a Server — QueryPie Session Recording
Previously, command audits showed who attempted rm and that it was blocked. Now I replayed the terminal session from Session Logs, jumping to the restriction and the subsequent file checks. Direct replay from Command Audit was especially convenient.
Blog
A Peek Into a Day in the Life of QueryPie TPM Team: The Secret to Winning Over Customers
A glimpse into QueryPie TPM's daily efforts to win customer trust and deliver exceptional results with effective strategies.
November 22, 2024
White Papers
Revolutionizing Security Management with Policy as Code (PaC)
Automate and optimize security protocols using QueryPie's Policy as Code, ensuring compliance and reducing risks.
ACP Lab Notes
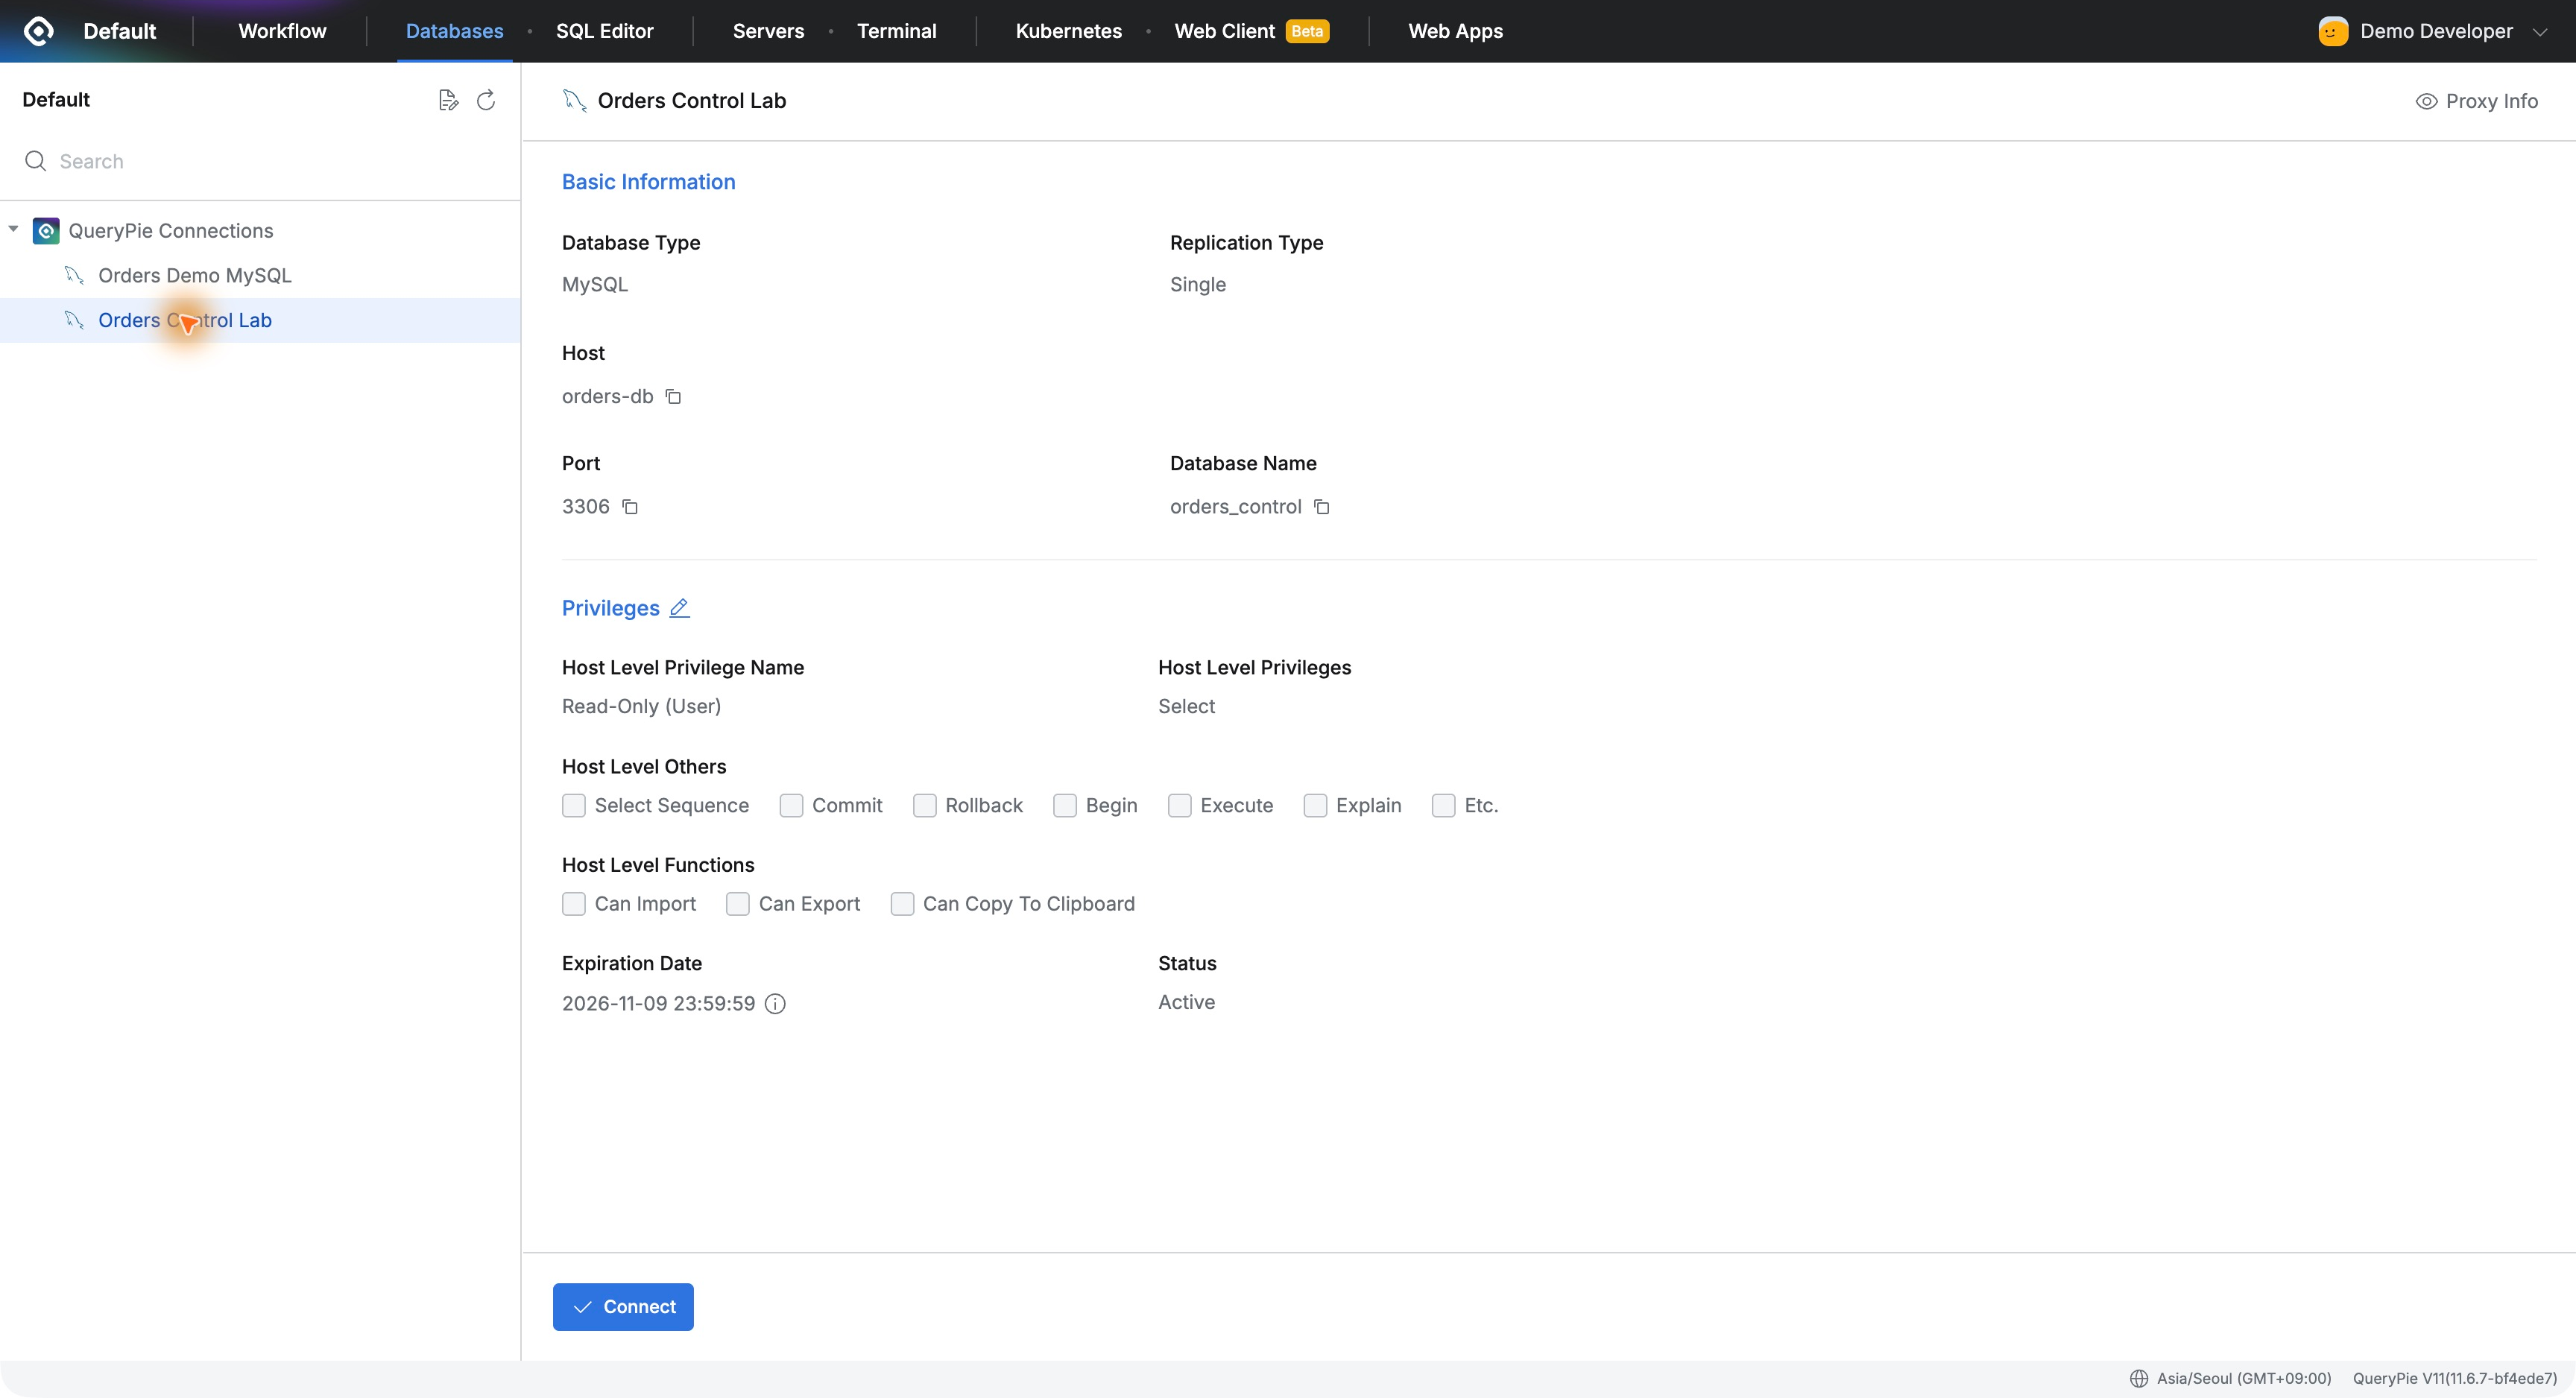
[Part 25] Database Queries Through MCP Keep Existing Permissions — QueryPie Community MCP
When connecting AI tools to a database, I first wanted to know who could see what. Orders should be accessible for work while settlements retain their restrictions. I connected MCP Inspector to QueryPie Community and tested both.
VOC
"The solution that best fit our automation strategy was undoubtedly QueryPie!"
How did LG U+ implement Zero Trust in a public cloud environment? Discover how QueryPie helped automate security & access control!
March 24, 2025
Events
Ep.1 QueryPie Integrations: Hitting the Core of Automation!—SCIM, yap! Vault, yap! Slack approval workflow integration, yap!
Are you curious about what features the QueryPie product has and what roles each feature plays? In Ep. 1, we explored the key features of the QueryPie product on behalf of our customers.
November 29, 2024
Blog
Your New Ally in Data Privacy and Management: Data Discovery
Learn how QueryPie's data discovery tools enhance privacy management and ensure compliance with global data regulations.
November 22, 2024
White Papers
Access Control for Secure Operation of Kubernetes Clusters
QueryPie ensures secure Kubernetes access control for improved cloud cluster management and operational security.
ACP Lab Notes
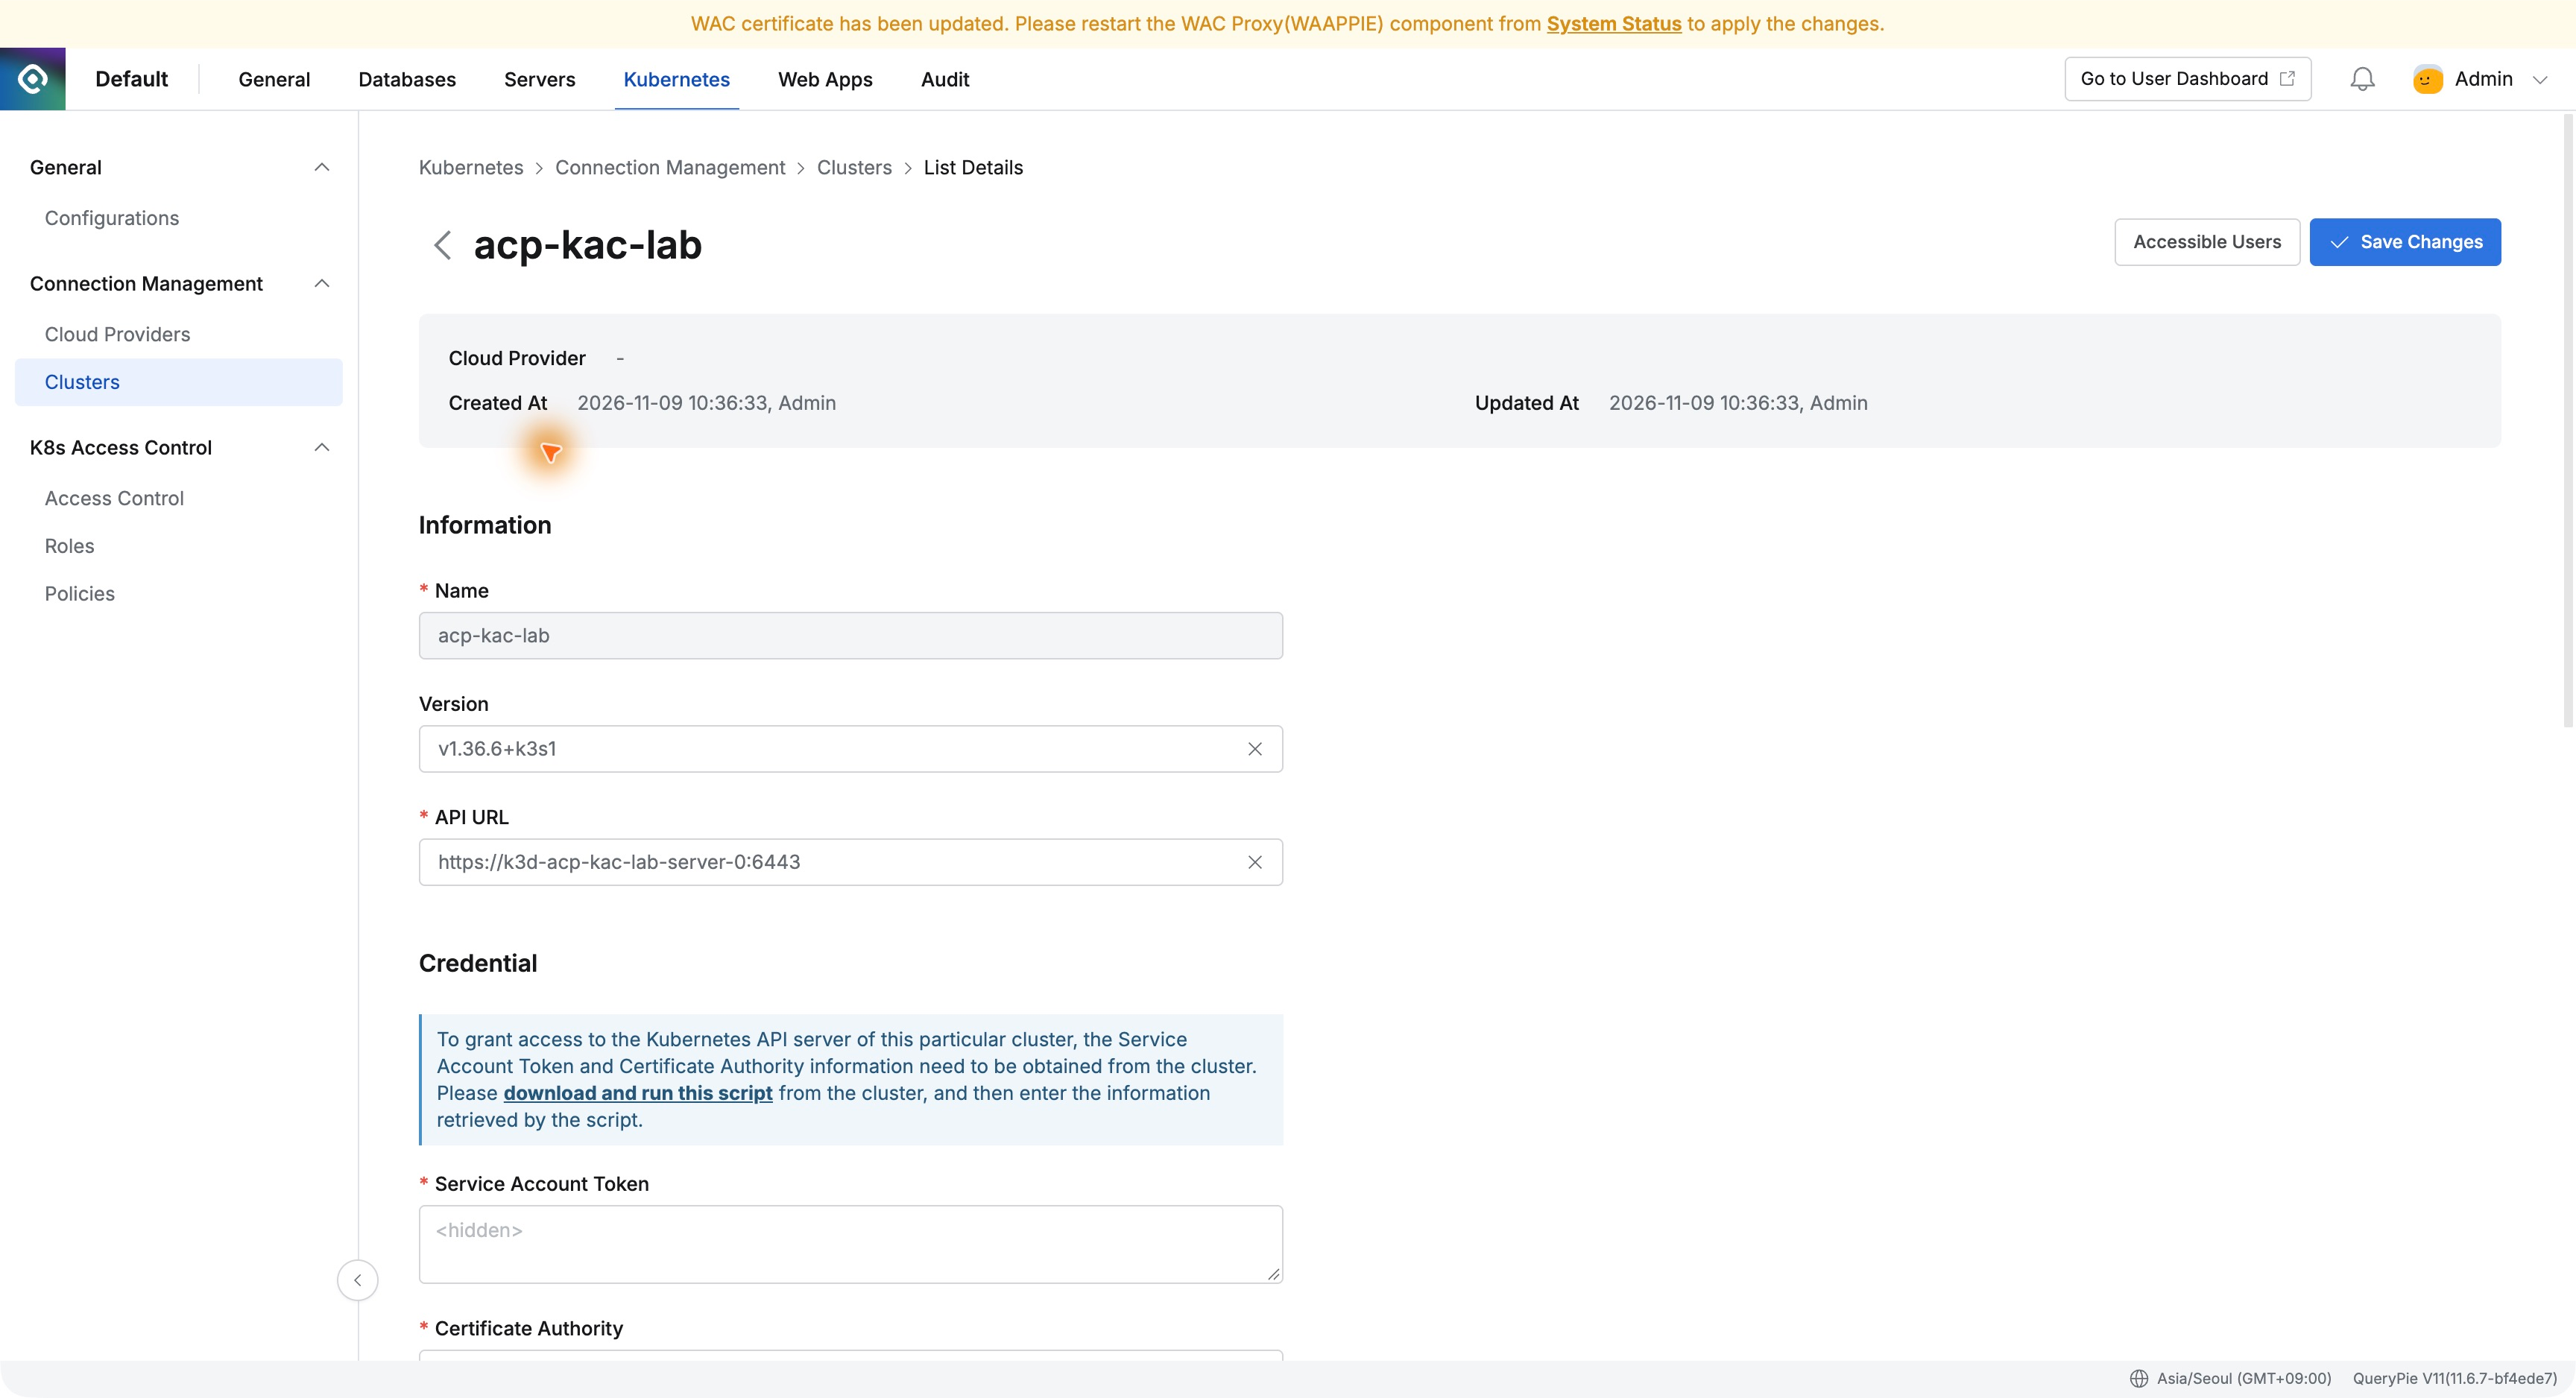
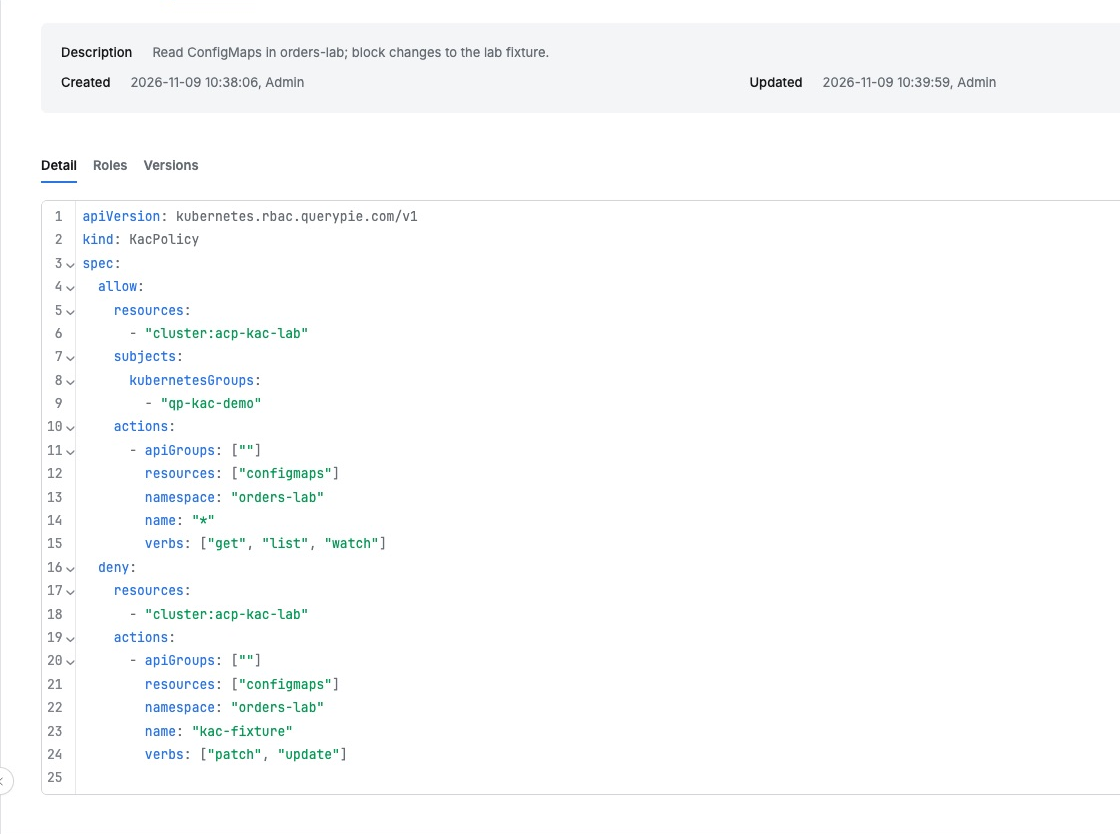
[Part 26] Reading Kubernetes Configuration While Blocking Changes — QueryPie Roles and Policies
Checking production Kubernetes settings does not always require permission to change them. I granted ConfigMap reads in QueryPie Community and denied changes, then reviewed both operations in the same audit screen.
Manuals
QueryPie ACP Community Edition Installation Guide
QueryPie ACP Community Edition is a free version that lets you experience all the core features of QueryPie ACP Enterprise — including Database, System, Kubernetes, and Web Access Controllers — with a maximum limit of 5 users. Get started quickly with a simple installation.
VOC
"The adoption of AI in traditional industries hinges on data and security as the keys to success."
In this video, we have the privilege of featuring Hyun Kim, the CEO and Founder of Superb AI.
January 6, 2025
Events
The full-scale customer communication content [Ch. QueryPie: 3-Step Side Kick] is here!
We prepared this for those who want to learn more about QueryPie and have many questions. From DB access control, system access control, Kubernetes access control, web application access control, to data discovery... We've extracted the core essentials of QueryPie, which encompasses access control and audit solutions covering enterprise infrastructure across cloud and on-premises environments.
November 29, 2024
Blog
QueryPie PM’s Work Smarts: Transforming into a True All-Rounder
QueryPie PM insights on becoming an all-rounder through effective work strategies and cross-functional collaboration.
November 22, 2024
White Papers
Preventing Command Bypass at the Source with Process-Tracking Methods
Prevent command bypass threats at the source with QueryPie's innovative process-tracking methods.
ACP Lab Notes
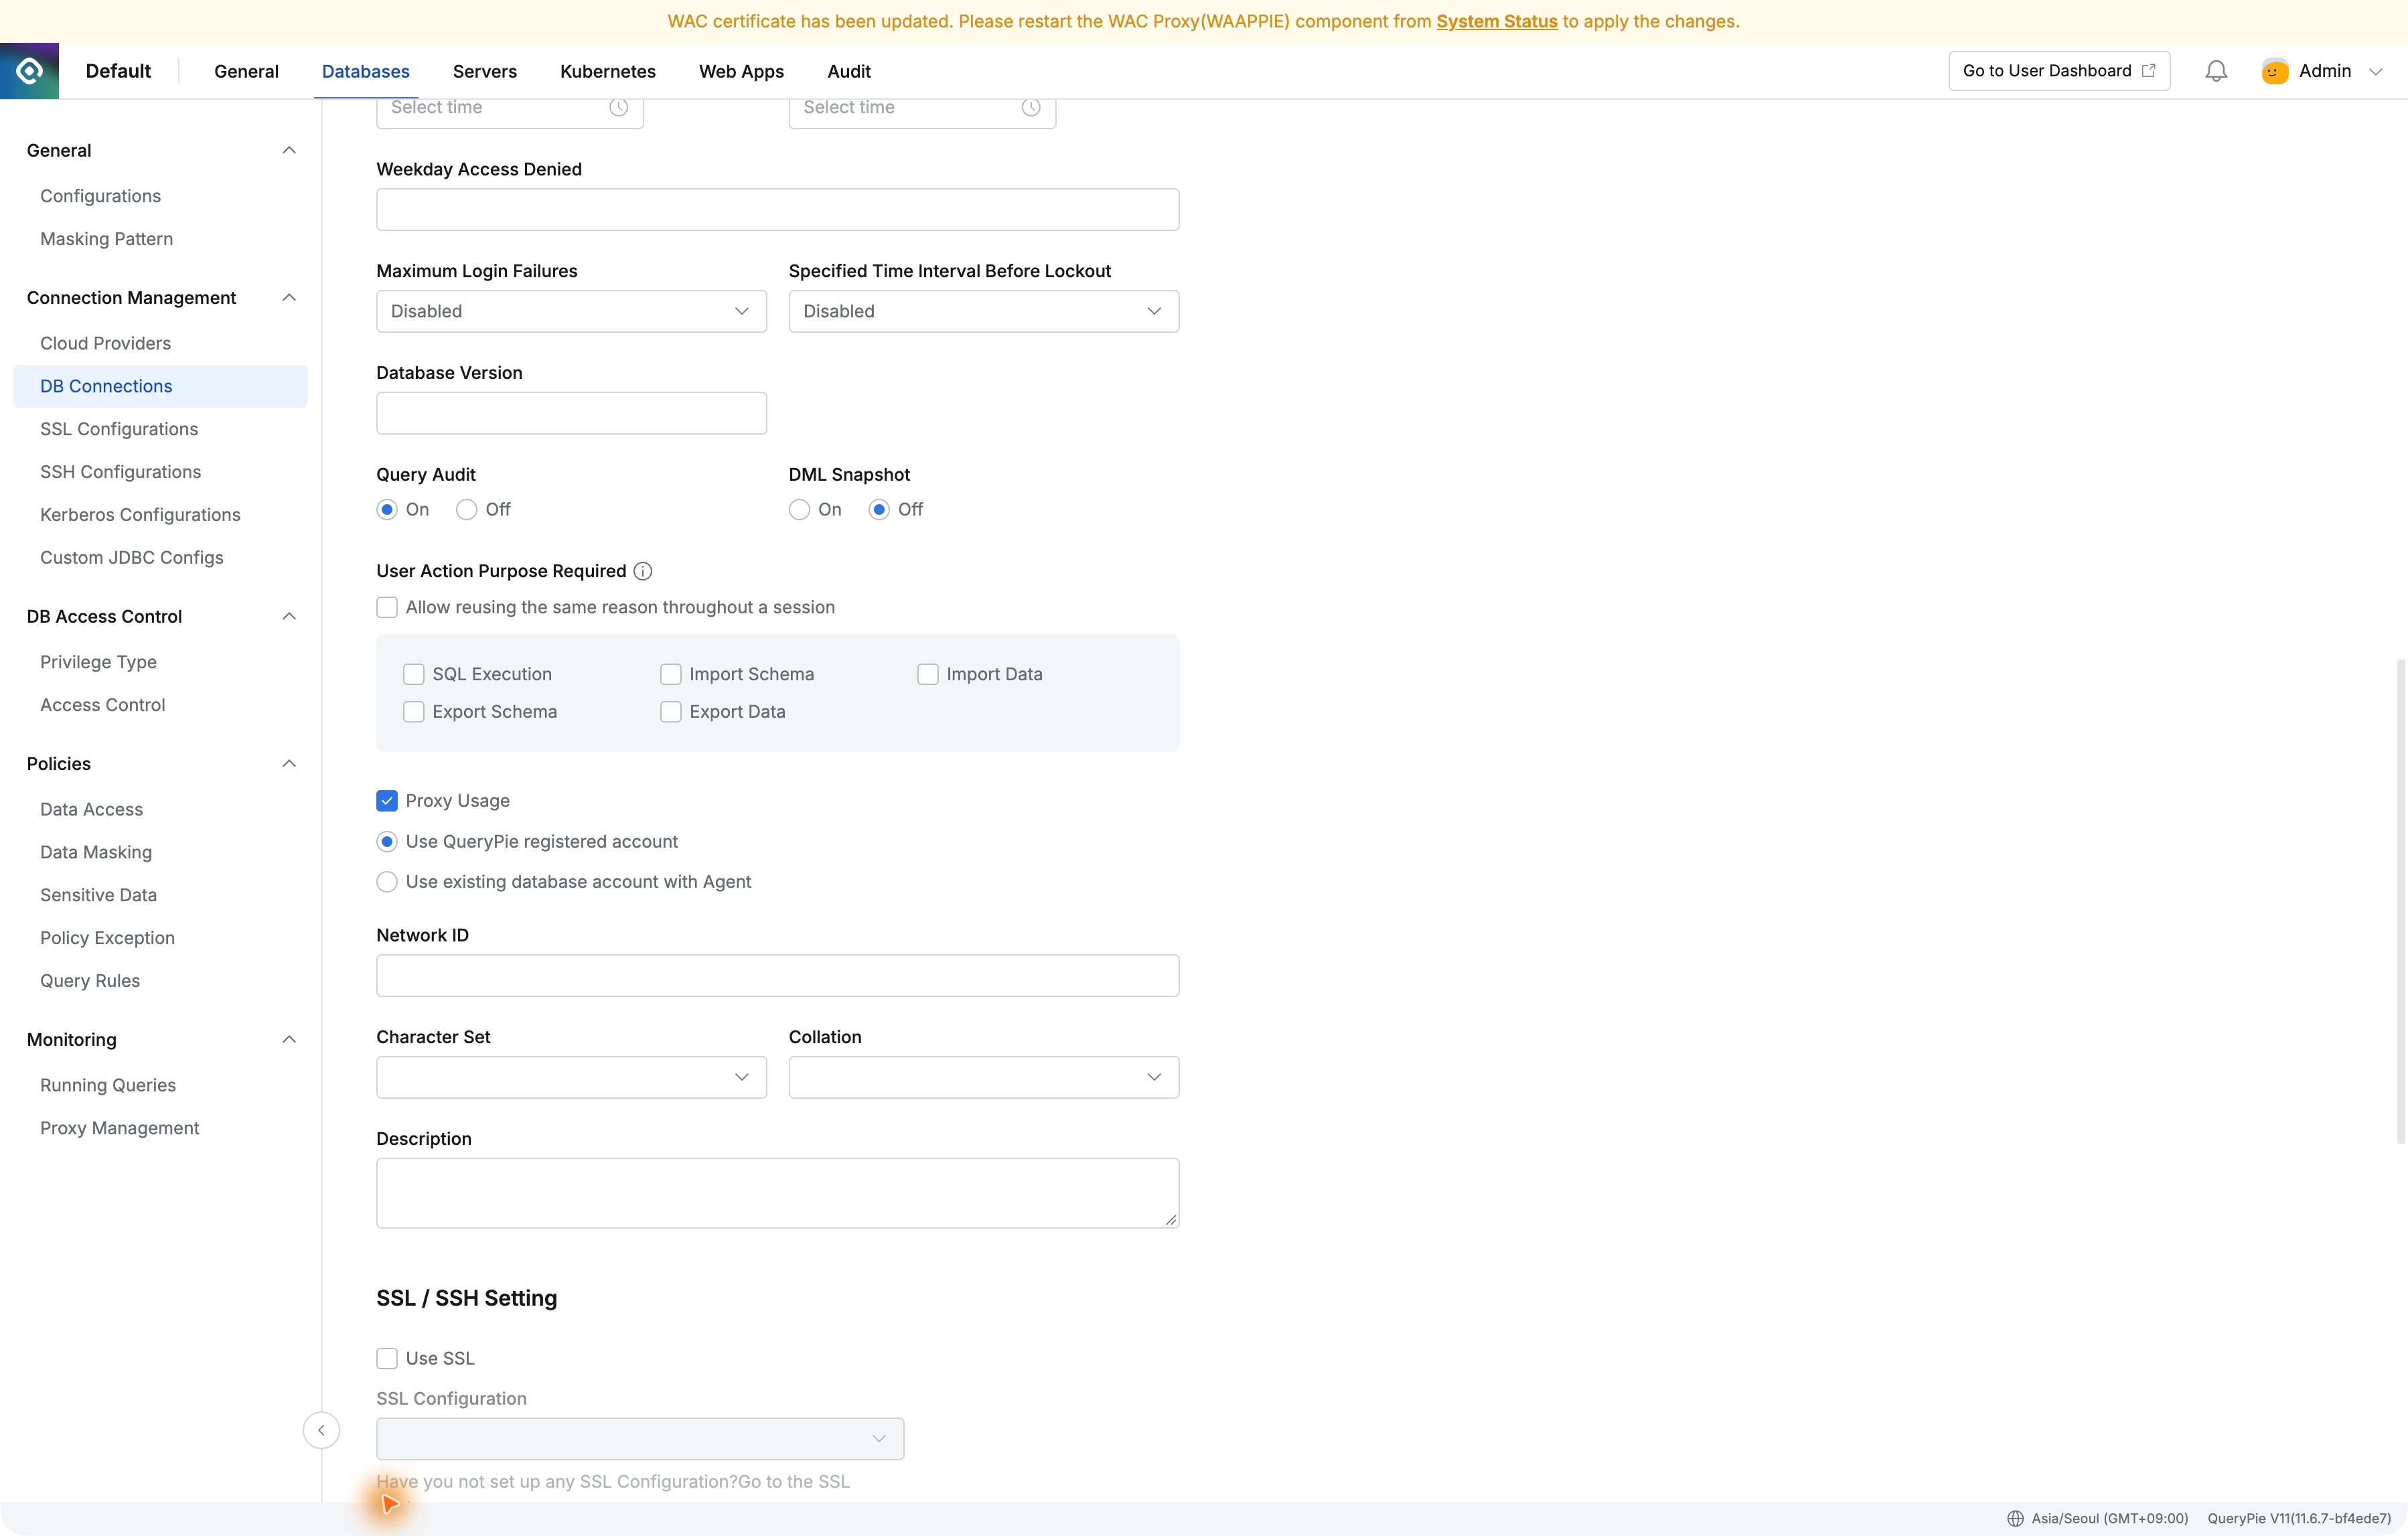
[Part 27] Keeping DBeaver, Closing Direct Database Access — Organizing QueryPie Connection Paths
QueryPie manages permissions and records, but an old direct database route needs separate attention. I compared direct and proxy queries in DBeaver, closed the direct port, and verified a new QueryPie connection still worked and produced audits.
Events
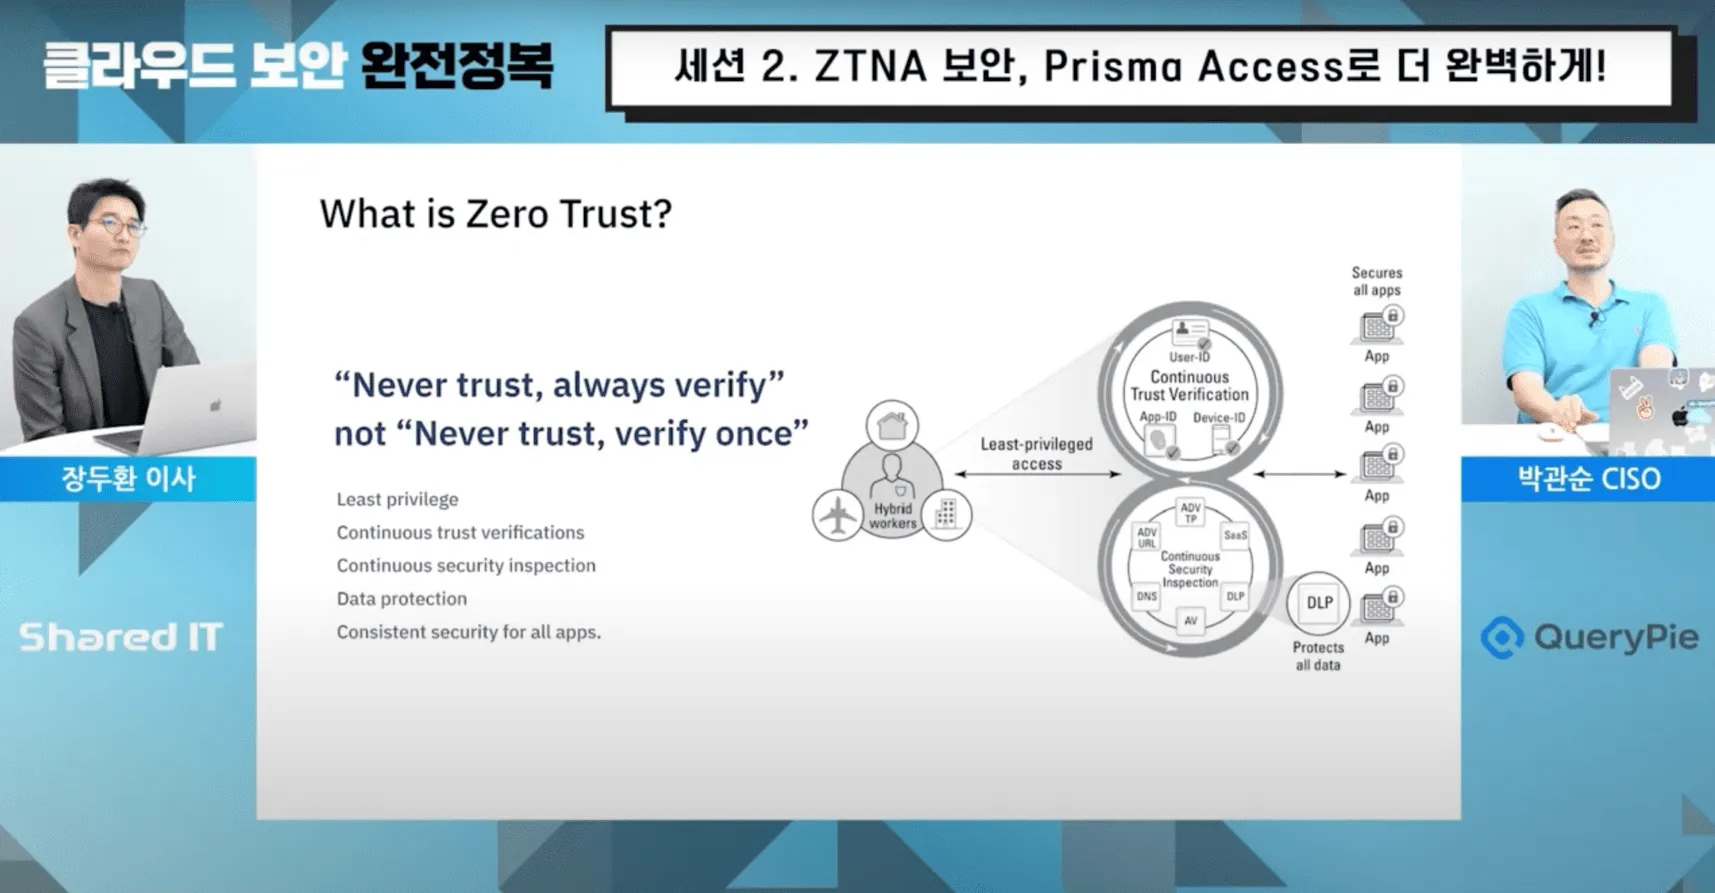
Achieve Perfect ZTNA Security with Prisma Access!
Why Did QueryPie Choose Prisma Access? Dive into the details of how QueryPie identified Prisma Access as the ultimate choice for their security needs.
November 29, 2024
VOC
"Beyond monitoring, it’s true governance."
In today's video, we have the privilege of featuring Mori Takeshi, the CEO of AIR Company Limited in Japan. AIR, also as one of QueryPie Japan's partners, they have been lead IT & software market in Japan for last decades.
November 29, 2024
Blog
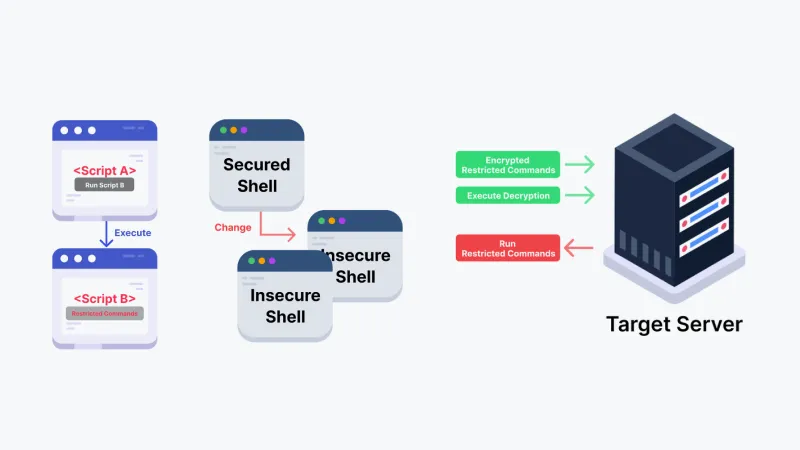
The Overlooked Command Bypass Issue: Let’s Finally Talk About It!
Addressing the overlooked risks of command bypass issues and how QueryPie offers advanced solutions to prevent them.
November 22, 2024
White Papers
Building a Transaction-Free, Flawless CDC (Change Data Capture) System
Sync data seamlessly with QueryPie's CDC system, ensuring conflict-free updates without transactions.
ACP Lab Notes
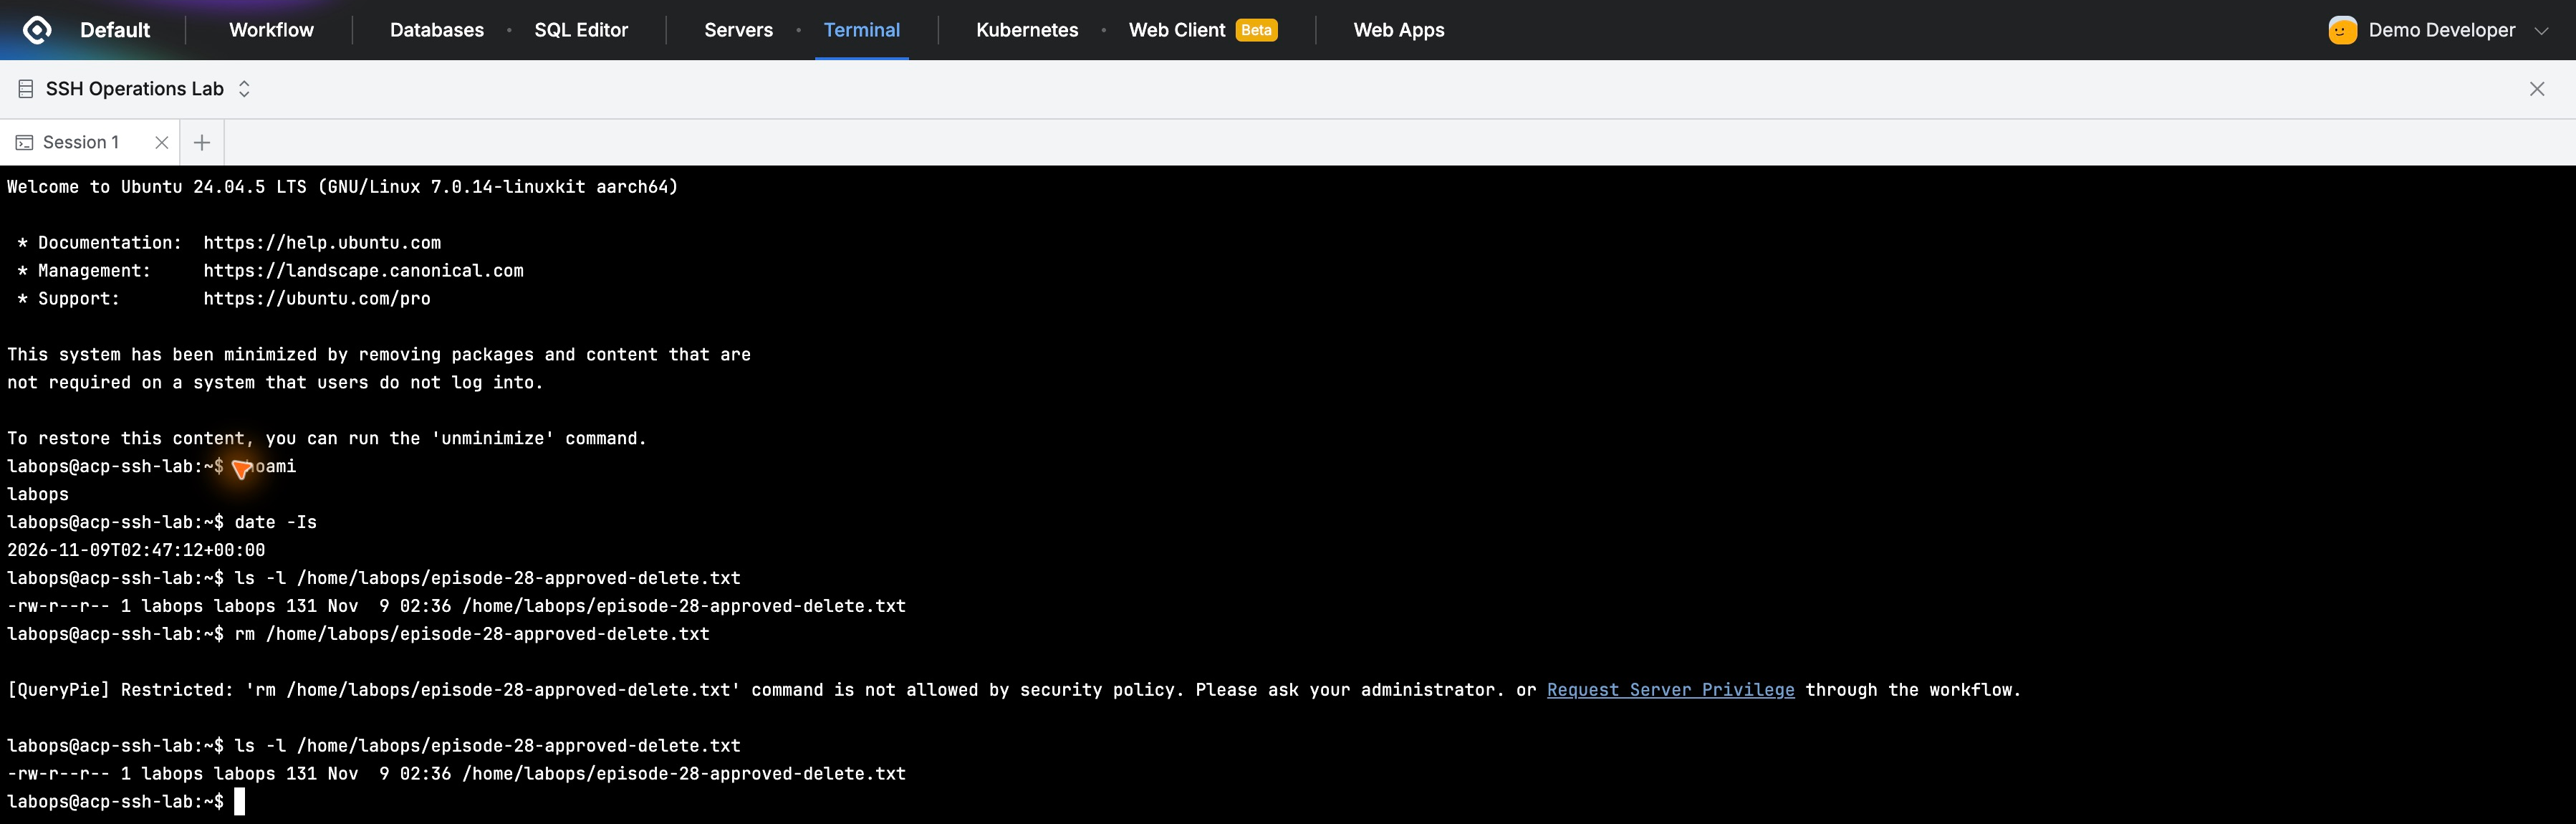
[Part 28] When a Blocked Delete Command Is Needed — Using It Only During an Approved Window
Part 23 blocked deletion despite allowing server login. Operations sometimes require restricted commands, such as cleaning old files. I requested five minutes of rm through Server Privilege Request, keeping the normal restriction intact.
Events
Flex Unveils the Secrets of QueryPie
Flex, Korea's top HR platform, unveils the surprising revelations they discovered after integrating QueryPie into their system. What hidden magic in QueryPie completely captivated the Flex team and transformed the way they work?
November 29, 2024
VOC
"QueryPie' s like a tailor shop almost for security."
Today, we have a special guest with us: Tom Lee, the CEO and Co-founder of LOVO AI.
November 29, 2024
Blog
QueryPie’s New Paradigm: Beyond Integration, Toward True Connectivity
QueryPie introduces a new paradigm, emphasizing true connectivity beyond mere system integration for better collaboration.
November 22, 2024
White Papers
Core Technology for Parsing SQL Across Multiple Vendors: QSI (Query Structural Interface)
Enhance system security with QueryPie's native command control through an advanced SSH proxy architecture.
ACP Lab Notes
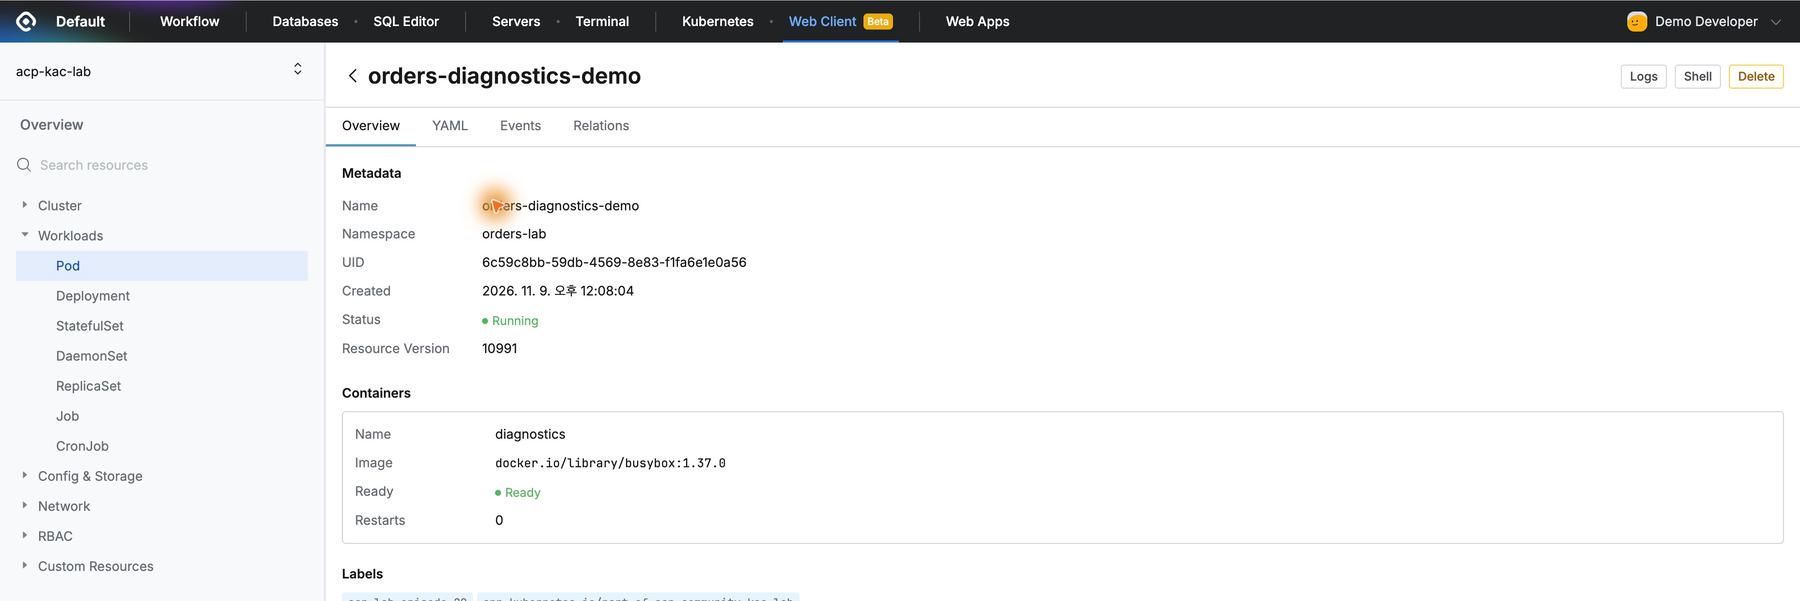
[Part 29] Reading Logs While Restricting Container Shell Access
Troubleshooting starts with logs, but not every log reader needs to execute commands in a container. Following Part 26’s read/change distinction, I separated log access from shell access on the same Pod in QueryPie.
Events
Achieving device security through MDM: Kandji x QueryPie
In this webinar, our security experts Brant Hwang (CEO, QueryPie) and Kenny Park (CISO, QueryPie) discuss how to secure your Apple devices and utilize Kandji’s powerful, purpose-built tools to create an intuitive, streamlined experience for admins and users alike.
November 29, 2024
VOC
"I envision a bright future, similar to the global business outcomes of QueryPie."
In today's video, we have the privilege of featuring Changsu Lee, the CEO and Founder of Allganize.
November 29, 2024
Blog
QueryPie’s Stride & Sustainability by Converging Technology and Humanities
How QueryPie merges technology with humanities to drive innovation and ensure long-term sustainability.
November 22, 2024
White Papers
Shell Native Command Control through SSH Proxy Architecture
Enhance system security with QueryPie's native command control through an advanced SSH proxy architecture.
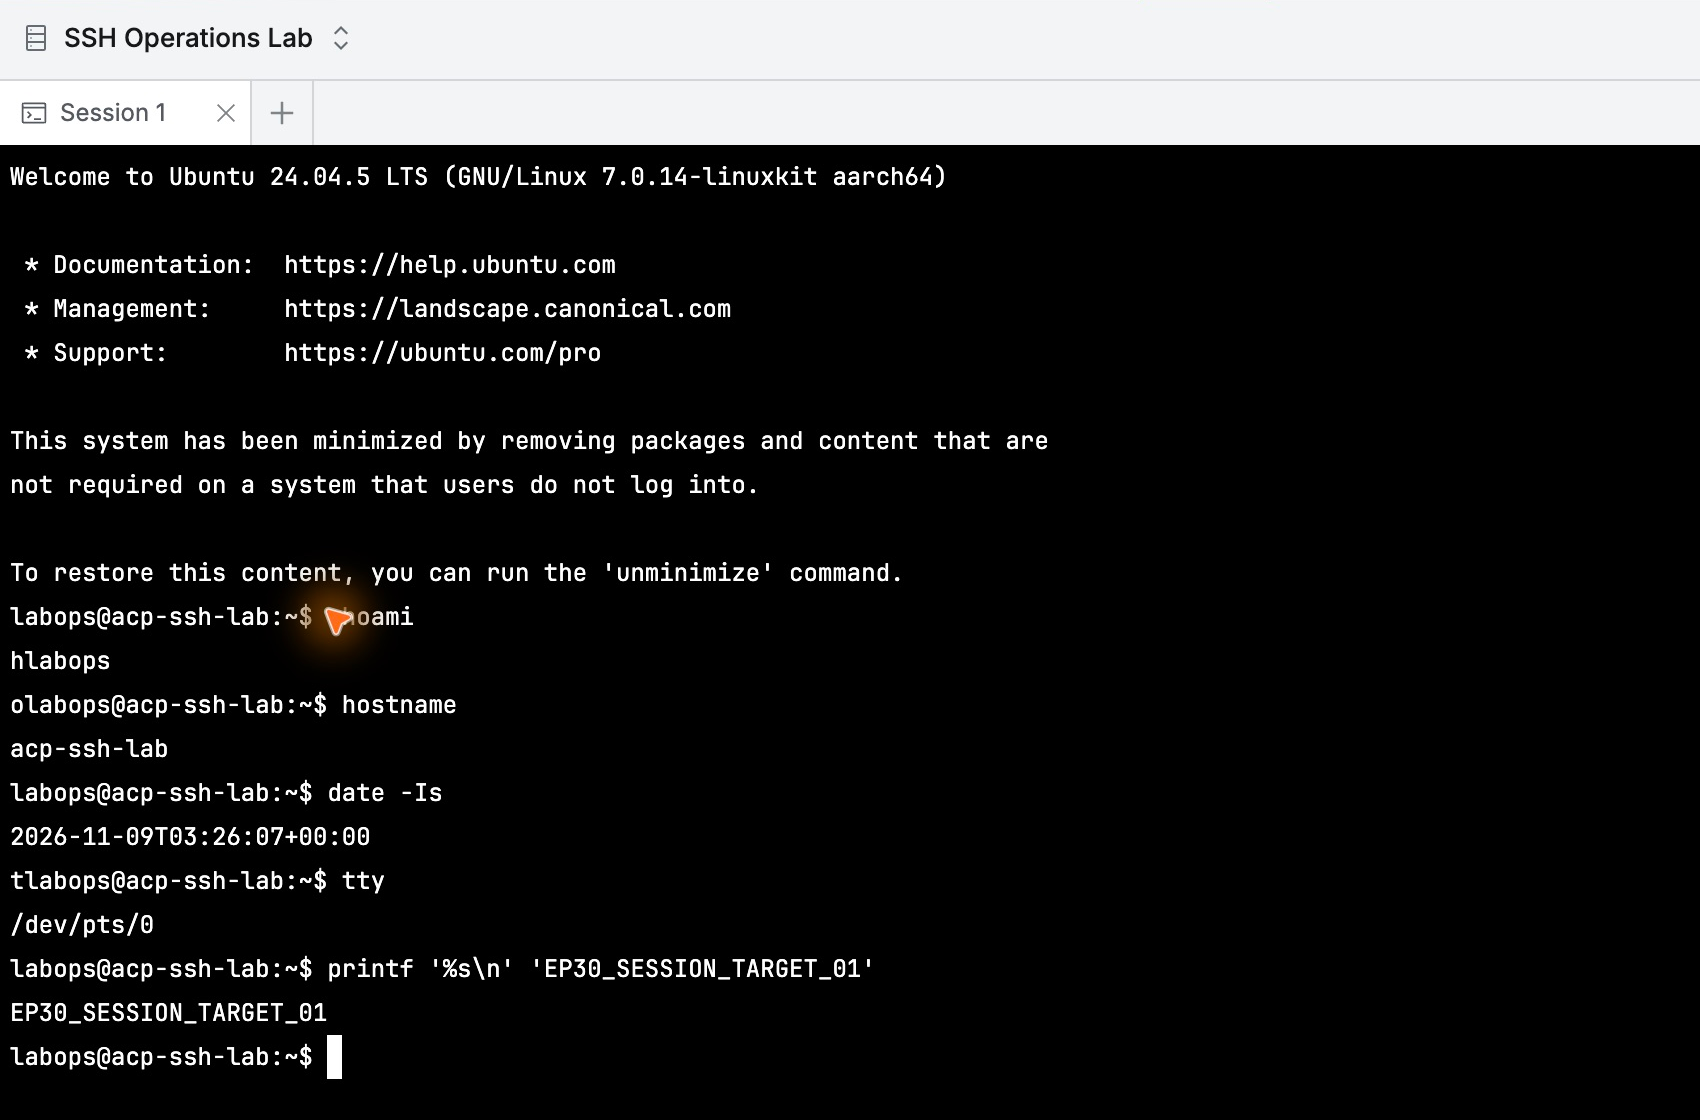
ACP Lab Notes
[Part 30] Finding and Terminating an Active Server Session
Access management continues after login: operators need to see who is connected and end a specific session when necessary. Part 24 replayed completed work; this time I found and terminated an active SSH session, then checked reconnection with the same role.
Events
Okta x PaloAlto Networks x QueryPie: The OPQ Webinar
Going beyond cloud security to cloud-native security, the OPQ Alliance (Okta x Palo Alto Networks x QueryPie) will show you the way. Watch this three-part webinar to learn more!
November 29, 2024
Blog
From Chaos to Order: Revolutionizing Multi-Cloud Kubernetes Access Control
QueryPie's approach to streamlining multi-cloud Kubernetes access control for enhanced security and operational efficiency.
November 22, 2024
White Papers
Improving Personal Data Identification and Analysis with AI
Utilize QueryPie's AI to analyze personal data, ensuring better privacy management and regulatory compliance.
ACP Lab Notes
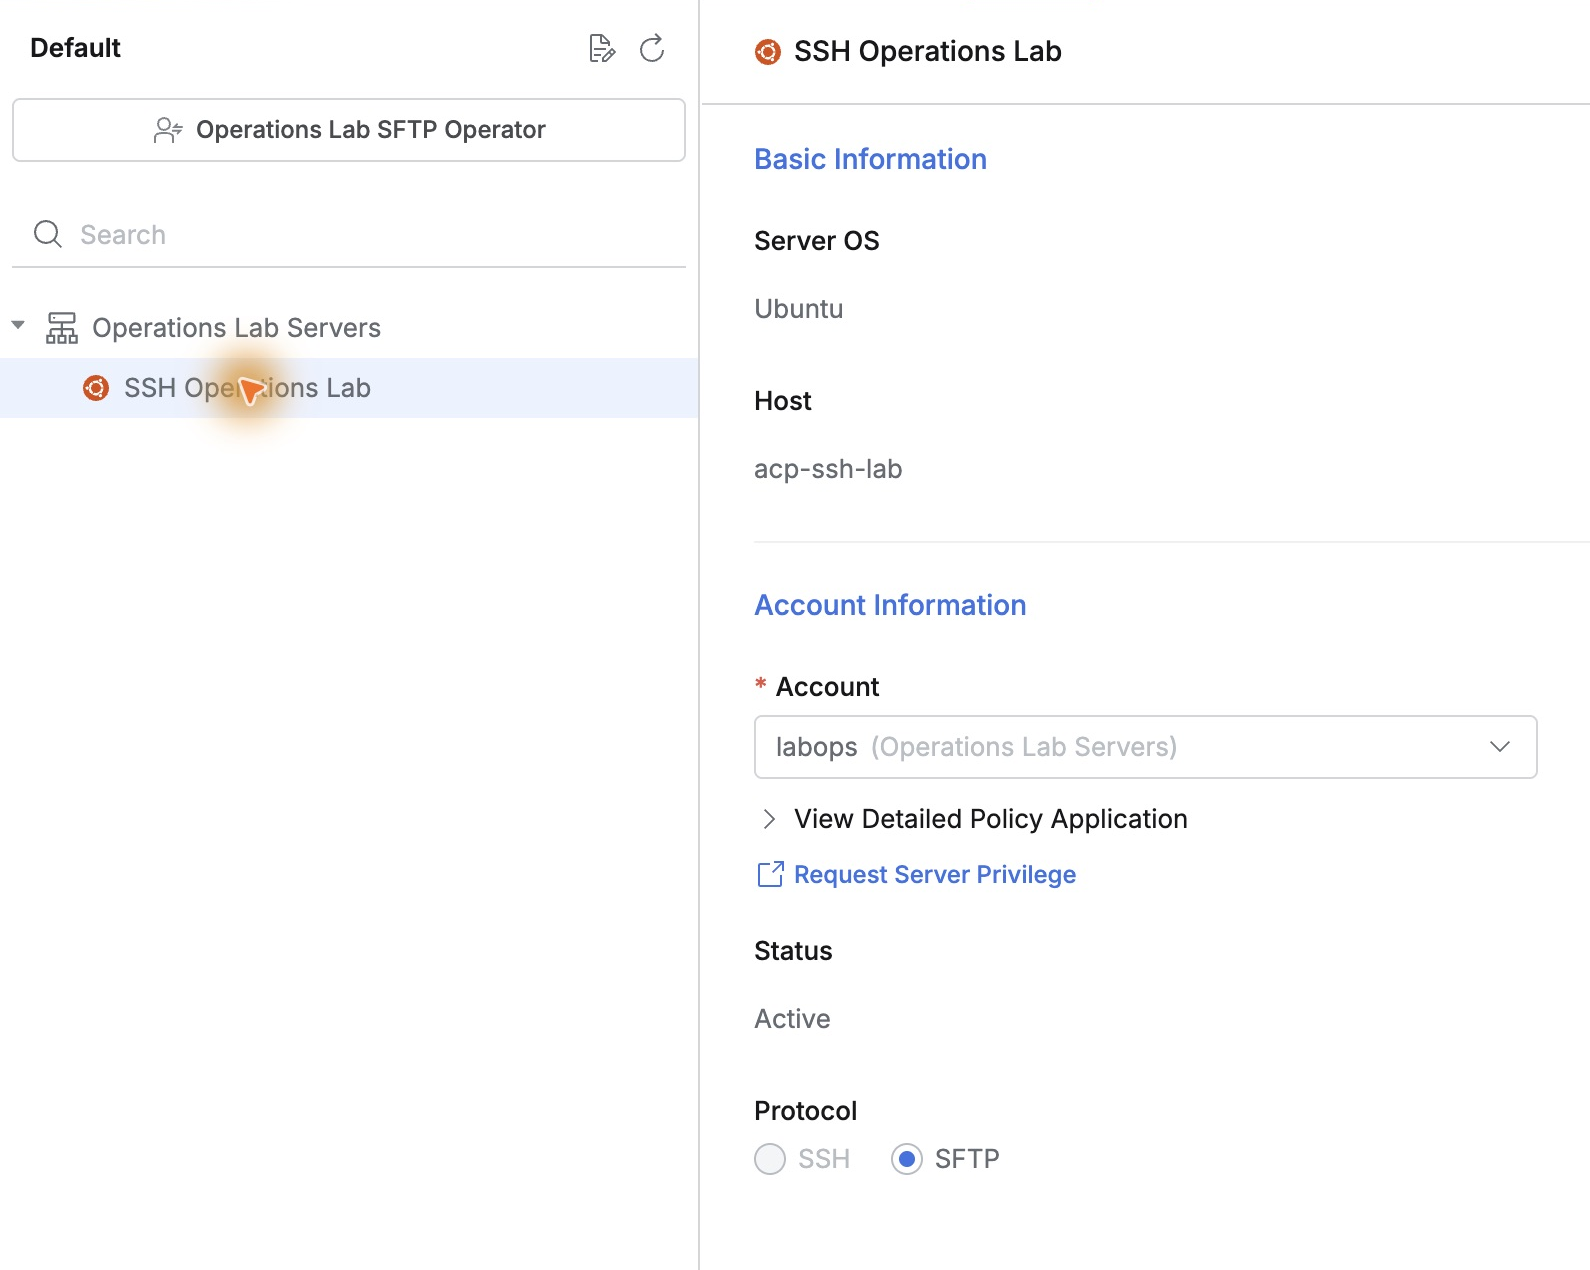
[Part 31] Downloading Server Files While Blocking Uploads
Inspecting production status files need not include upload rights. I used QueryPie web SFTP to transfer files with one user/account, then restricted only uploads and checked that downloads remained available.
Events
Discover the shortest path to getting certified in the cloud era with our best practices
Are you going round in circles trying to get certified? Discover the shortest path to getting certified in the cloud era with our best practices.
November 29, 2024
Blog
Secrets of Successful Teams? Work Like QueryPie!
Explore QueryPie's secrets to building successful teams through collaboration and shared values.
November 22, 2024
ACP Lab Notes
[Part 32] Recording the Reason Alongside the SQL
SQL audits show who queried what, but not whether a lookup answered a shipping inquiry or reconciled processing. I required execution reasons in QueryPie and queried two orders for different purposes, then checked their audit records.
Blog
Cracking the Toughest Global Markets: What Makes QueryPie So Confident?
How QueryPie confidently tackles global market challenges with innovative solutions and strategic expertise.
November 22, 2024
ACP Lab Notes
[Part 33] Combining Database Privileges and Access History in a Report
Access reviews ask what privileges a person holds now and which databases they used recently. I combined both in QueryPie Reports for Demo Developer, then inspected the downloaded summary and detailed files.
Blog
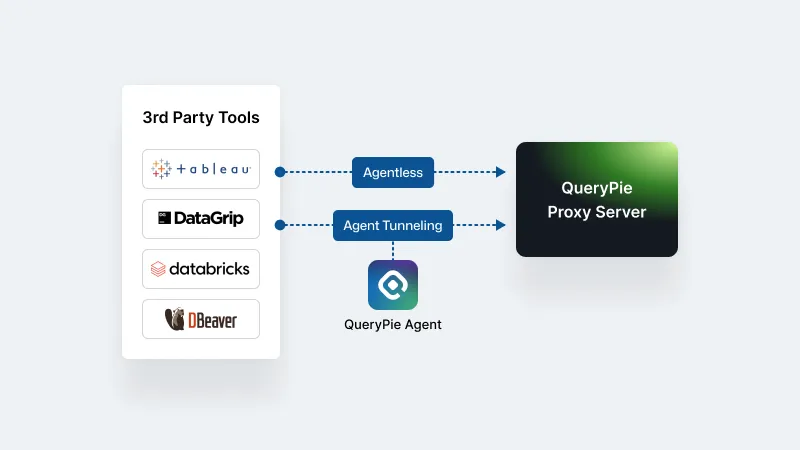
Why QueryPie Stands Firm on Its Agentless Philosophy
Understand QueryPie's commitment to an agentless approach for streamlined and secure system management.
November 22, 2024
ACP Lab Notes
[Part 34] Separating Database Access by Task on the Same Server
Multiple business databases may share a server, but order staff do not need all settlement data. After table-level restrictions, I tested logical-database permissions: allow the orders database on one MySQL server while excluding finance.
ACP Lab Notes
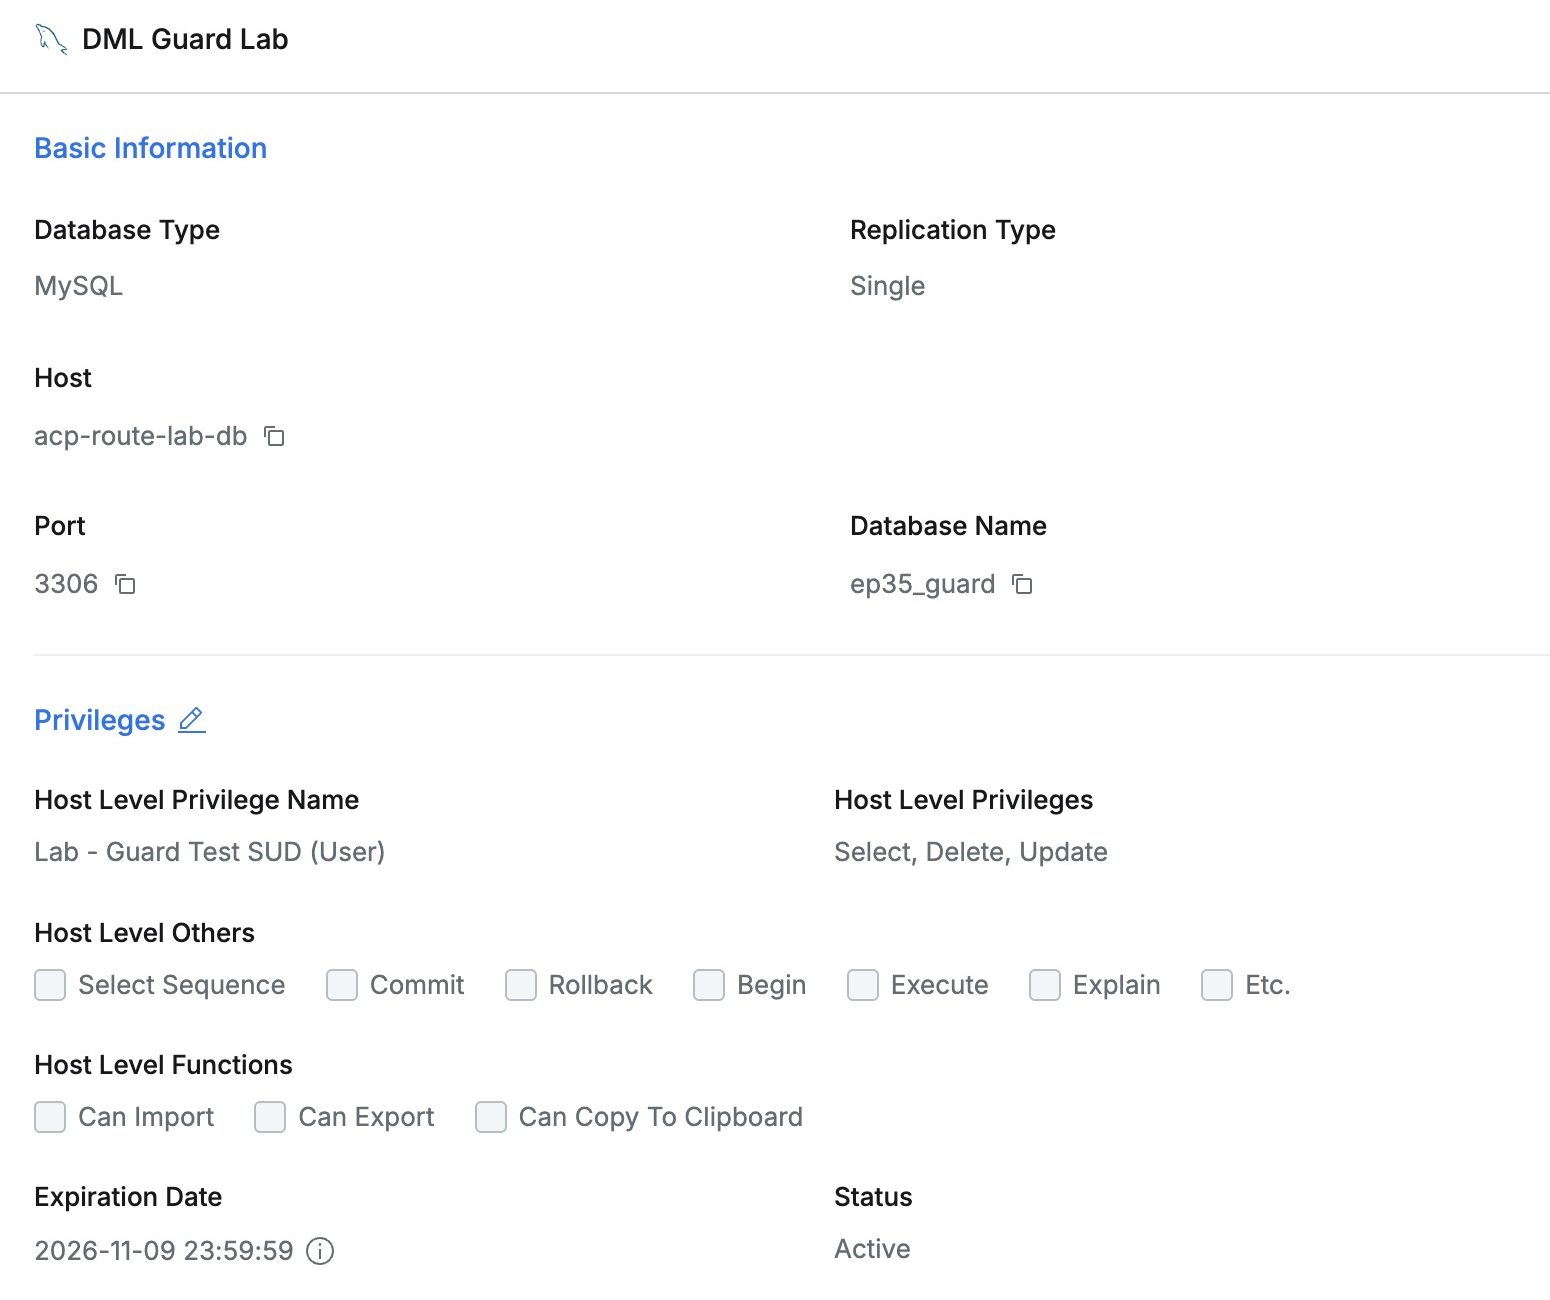
[Part 35] Blocking UPDATE and DELETE Without WHERE
Forgetting WHERE while changing one order can affect every row; DELETE may remove the whole table’s data. I enabled QueryPie’s safeguard and compared scoped SQL with missing-WHERE SQL using an account allowed to update and delete.
ACP Lab Notes
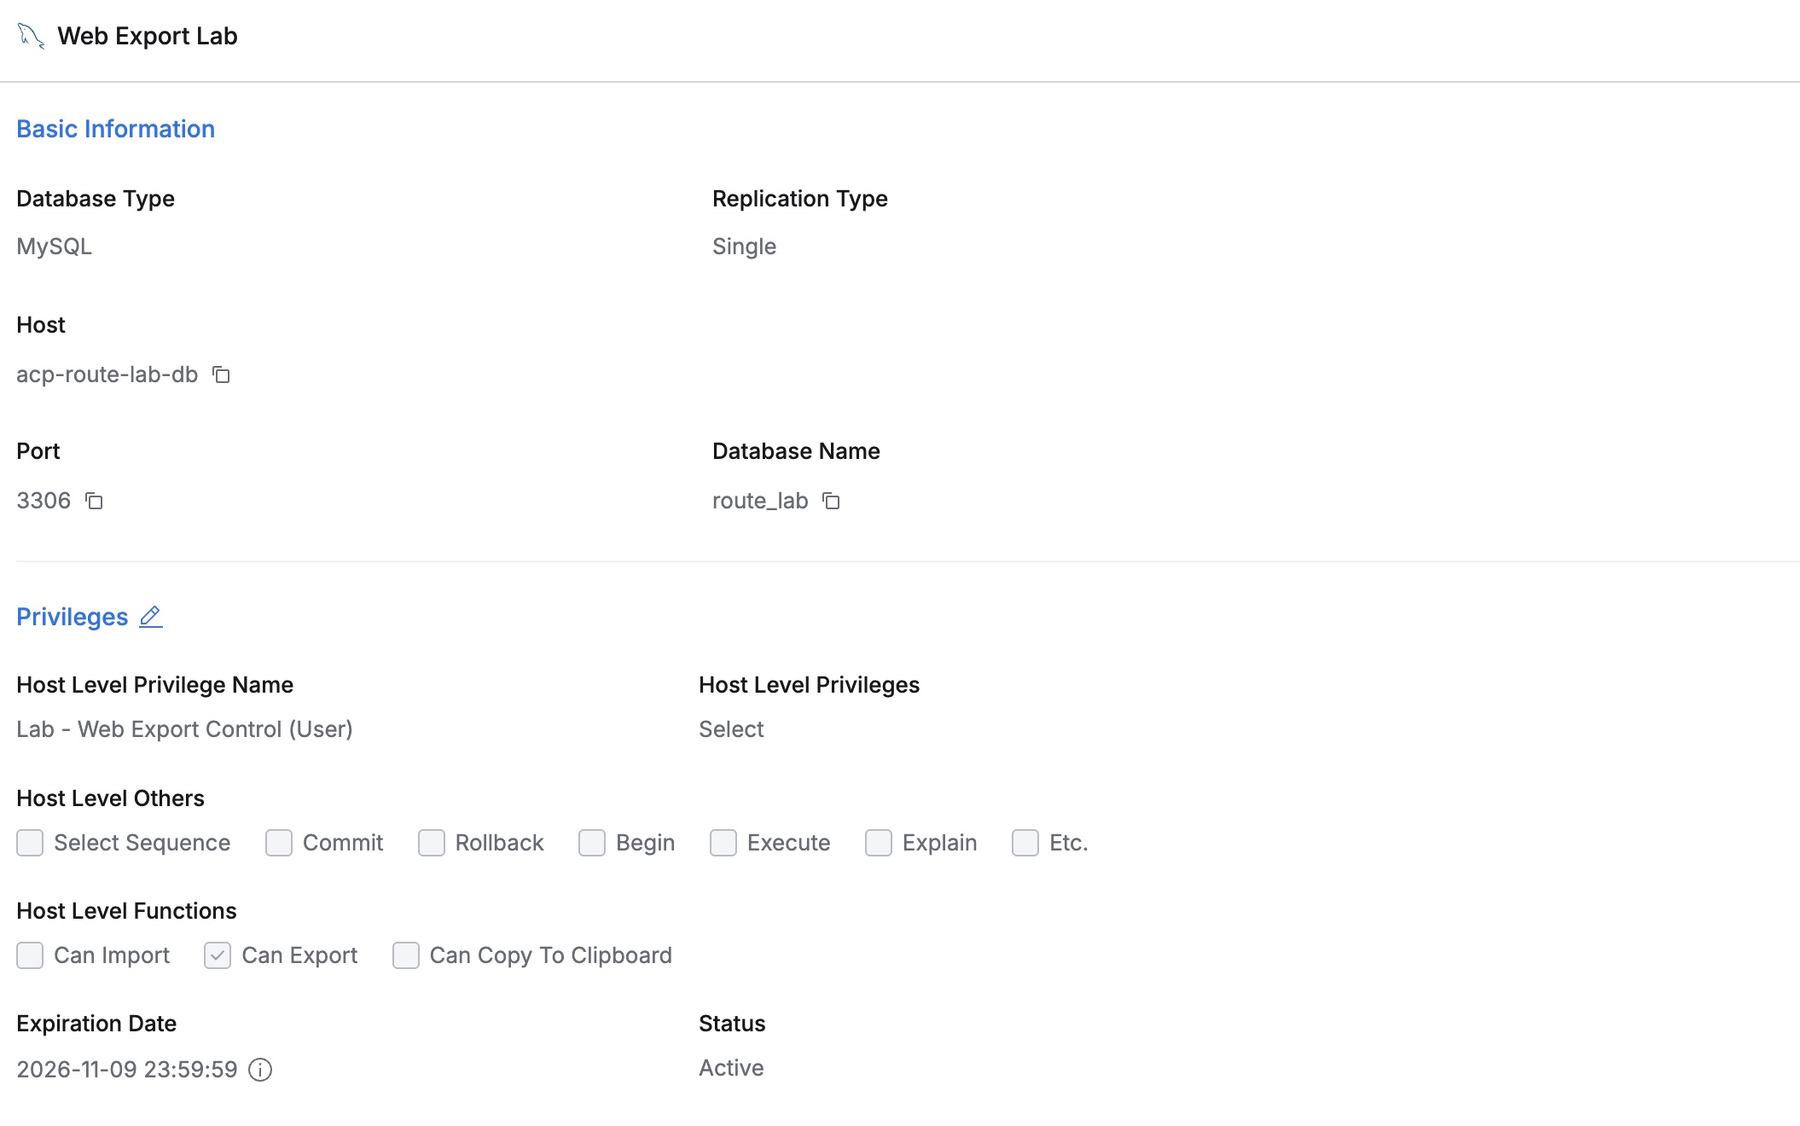
[Part 36] Allowing Reads and Managing File Export Separately
Sometimes viewing orders on screen is enough for shipping checks. I separated read and export privileges in the web SQL editor: first download three orders to CSV, then disable only Can Export and compare the UI.
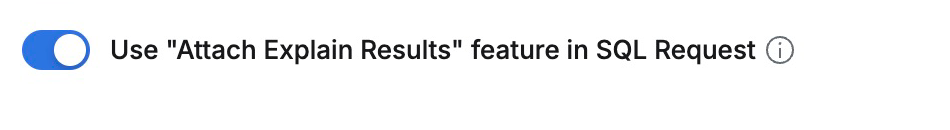
ACP Lab Notes
[Part 37] Reviewing the Execution Plan Before Approving SQL
SQL approval reviews the statement and reason. An execution plan adds table/index context. I attached a plan to SQL Request and checked that the approver could inspect the same evidence inside the request.
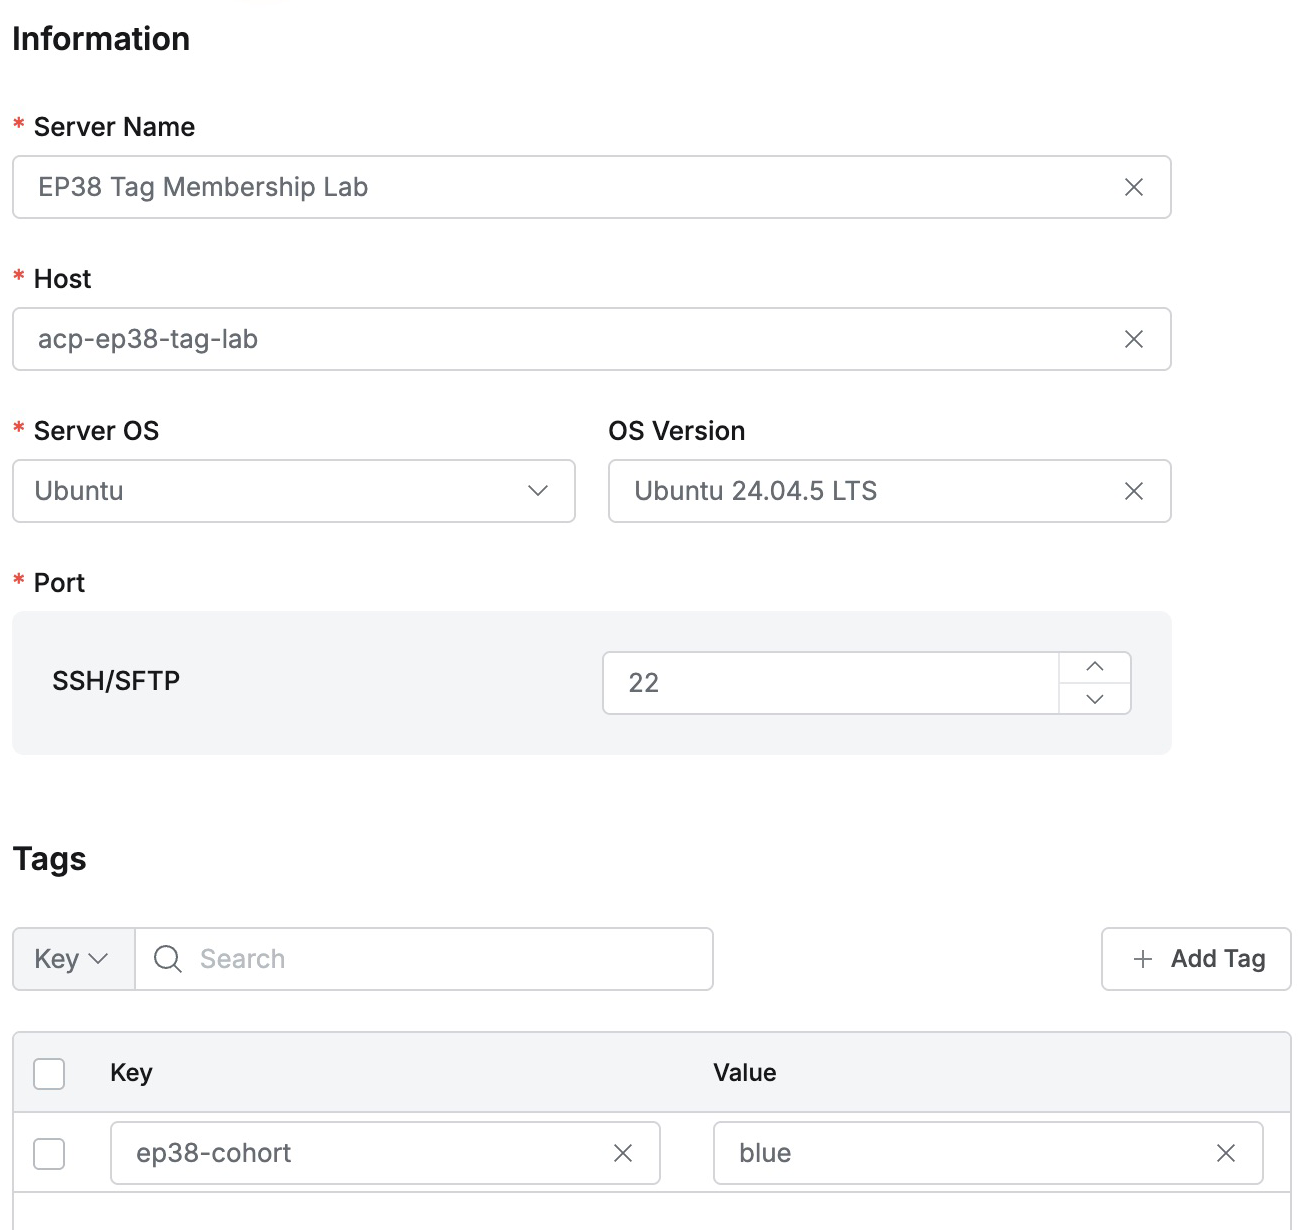
ACP Lab Notes
[Part 38] Changing a Server Tag Also Changes Group Membership
After registration and access grants, I explored grouping servers. QueryPie Server Groups can use tag conditions. I put the same server into a tag-based group and a manual group, then changed its tag to compare membership.
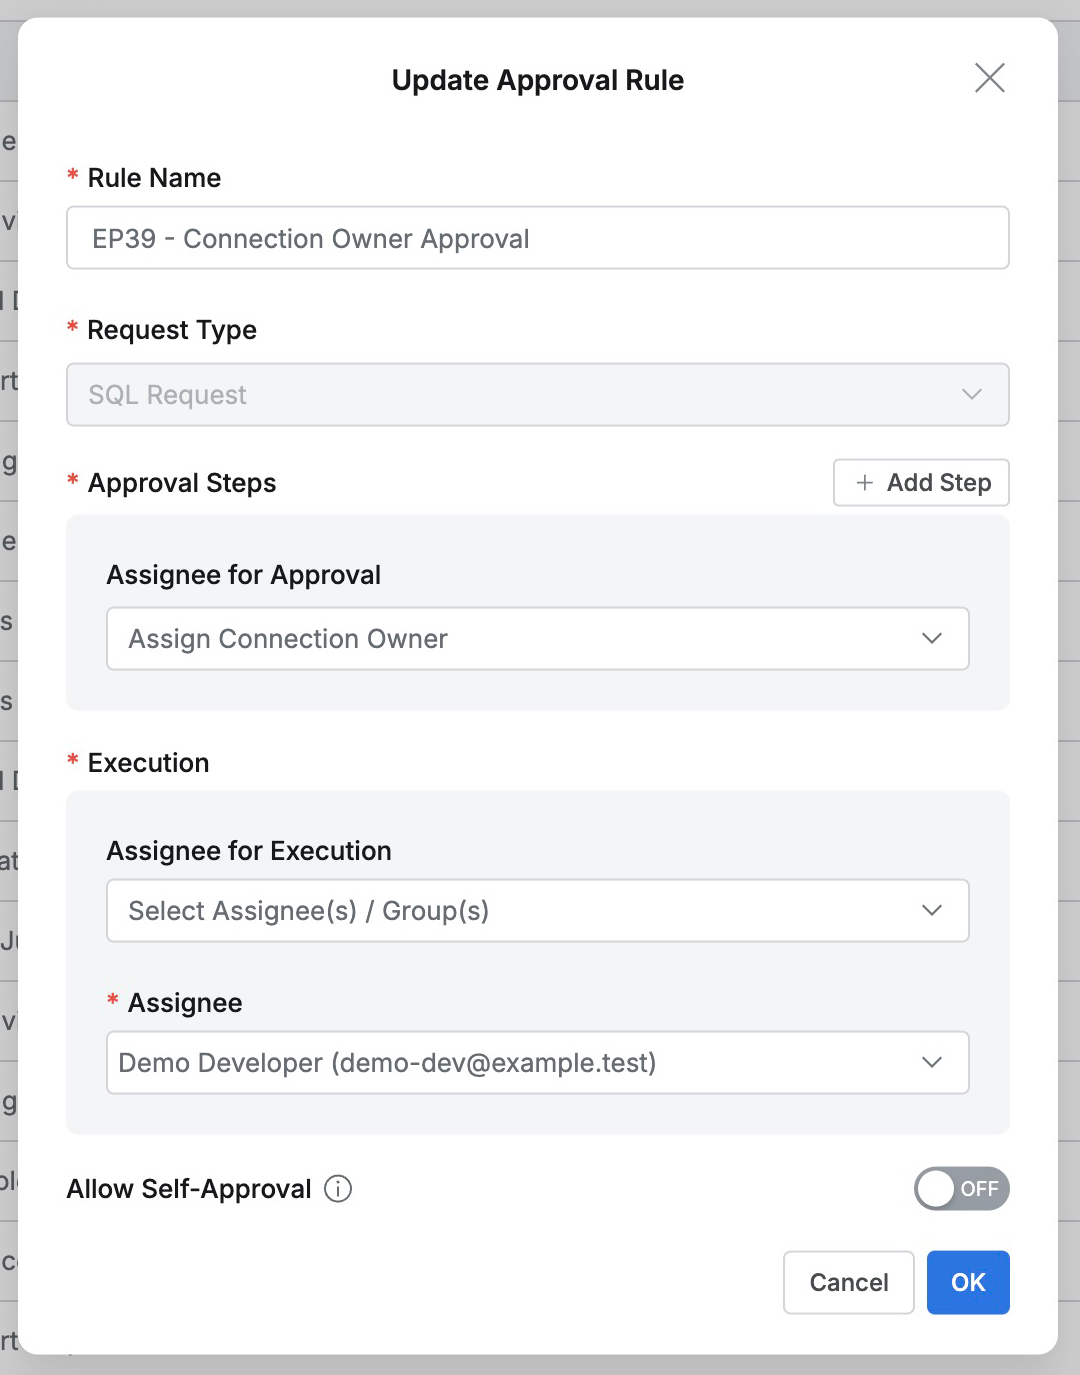
ACP Lab Notes
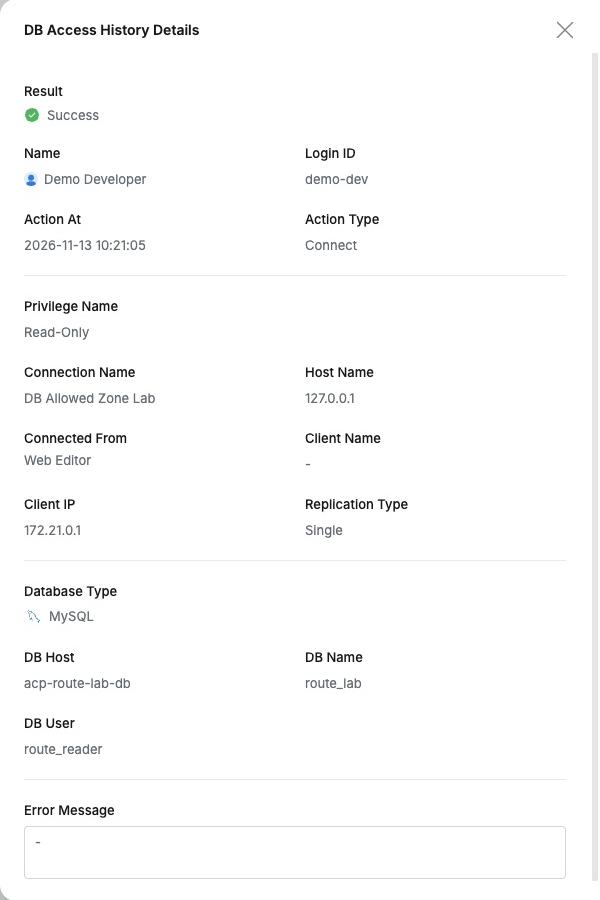
[Part 39] Changing the Database Owner Without Rewriting Approval Rules
Approval rules route SQL requests to reviewers, but must each rule be edited when the database owner changes? I used Connection Owner, processed one request, changed only the connection owner, and checked the next request’s assigned approver.
ACP Lab Notes
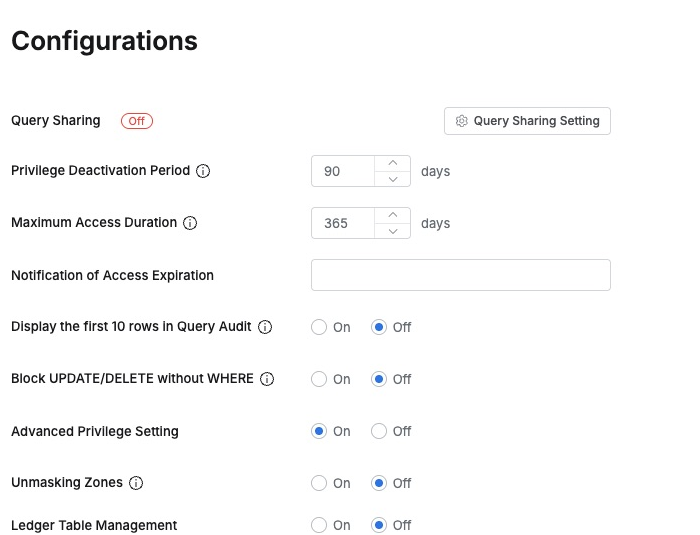
[Part 40] Keeping Database Privileges and Defining Allowed IPs
A user may need read access only from an approved network. I tried Allowed Zone, changing only allowed IPs while retaining user privileges, then restoring the original setting to verify access returned.
ACP Lab Notes
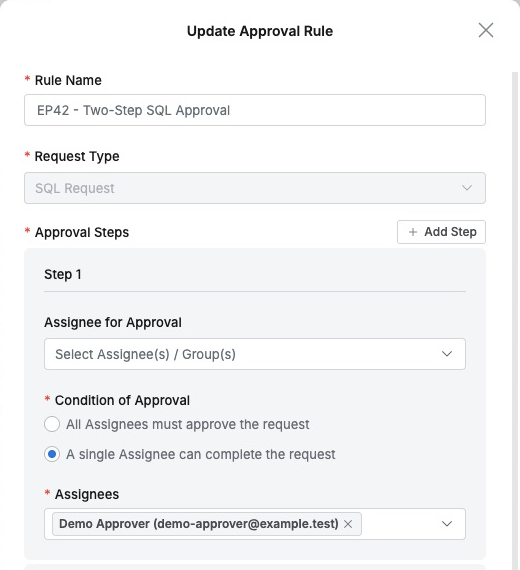
[Part 41] Mapping Read and Operational Privileges to Different Database Accounts
Database teams often separate read accounts from operational accounts. I mapped that distinction to QueryPie Advanced Privilege, verifying that the actual account changes with privileges and both identities remain in audits.
ACP Lab Notes
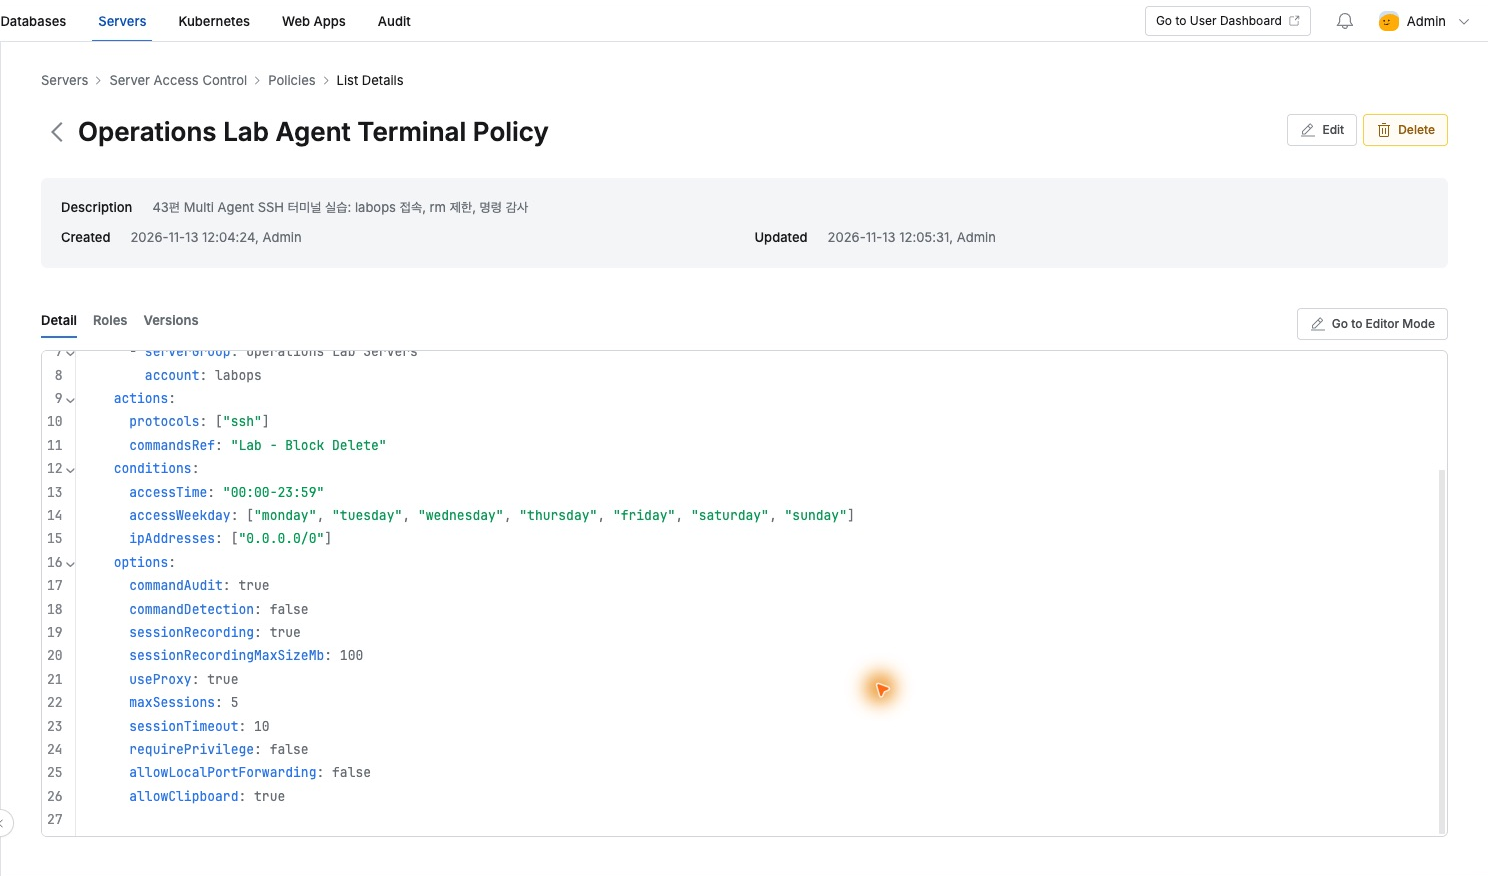
[Part 42] Adding Two-Step Approval to Database Work
Some database tasks need more than one reviewer: development checks SQL, then operations checks target and purpose. I built two sequential SQL Request approvals with different reviewers, then executed a one-order SELECT.
ACP Lab Notes
[Part 43] Connecting to Servers from My Everyday Mac Terminal
I wanted to keep inspecting accounts, files, and commands in my familiar terminal. I connected through Multi Agent from the Mac, tested normal commands and a restricted deletion, then reviewed connection and command audits in QueryPie.
ACP Lab Notes
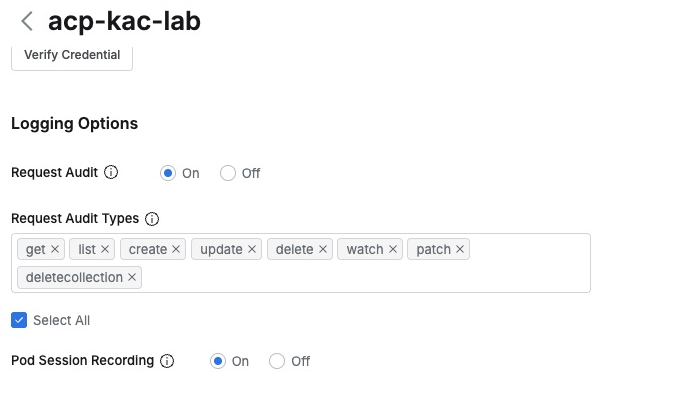
[Part 44] Separating Access Scope While Keeping kubectl
Kubernetes teams use kubectl daily and should not need a web UI for every check. I connected through Multi Agent, read a ConfigMap, attempted a change, and checked role-based handling in QueryPie.
ACP Lab Notes
[Part 45] Replaying Work Inside a Container
Knowing someone entered a container raises the next question: what did they do and see? I performed a short test-Pod inspection and replayed Pod Session Recordings, linking access records to the actual terminal view.
ACP Lab Notes
[Part 46] Changing a Server Account Password in QueryPie
A password change includes verifying access afterward and helping users reconnect, not just pressing a button. As servers grow, tracking rotations becomes difficult. I tried Password Provisioning on a test account, then connected and ran commands through QueryPie.
ACP Lab Notes
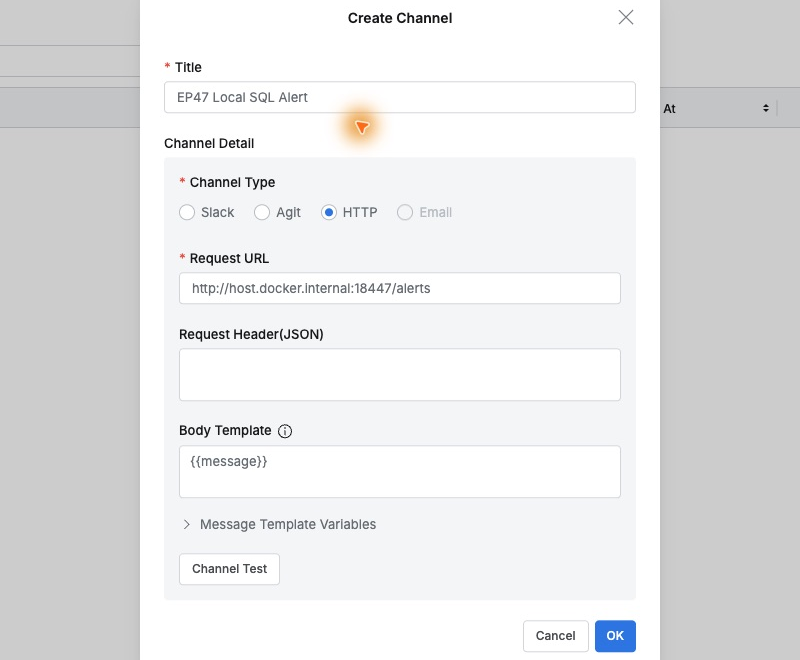
[Part 47] Receiving Alerts for Blocked SQL
Unauthorized SQL was already blocked, but could operators learn about attempts without constantly checking audits? I used Alerts, ran UPDATE with read-only access, and compared the delivered message with the audit.
ACP Lab Notes
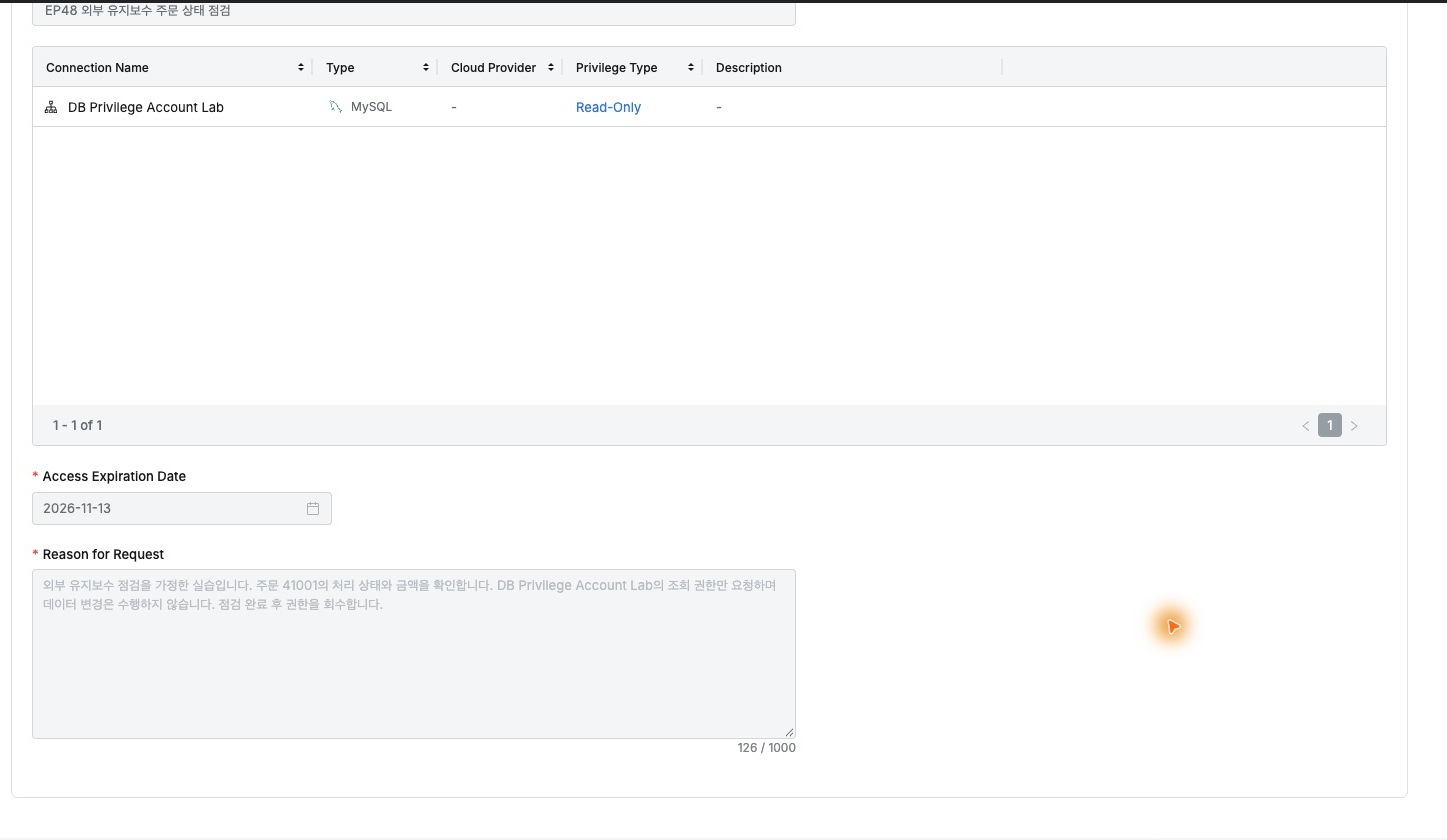
[Part 48] Delegating Only Necessary Work to External Maintenance Staff
External database checks need careful scope: order inspection does not require changes, and access should not remain after work ends. I followed a test contractor from read-access request through approval, inspection, revocation, and verification.
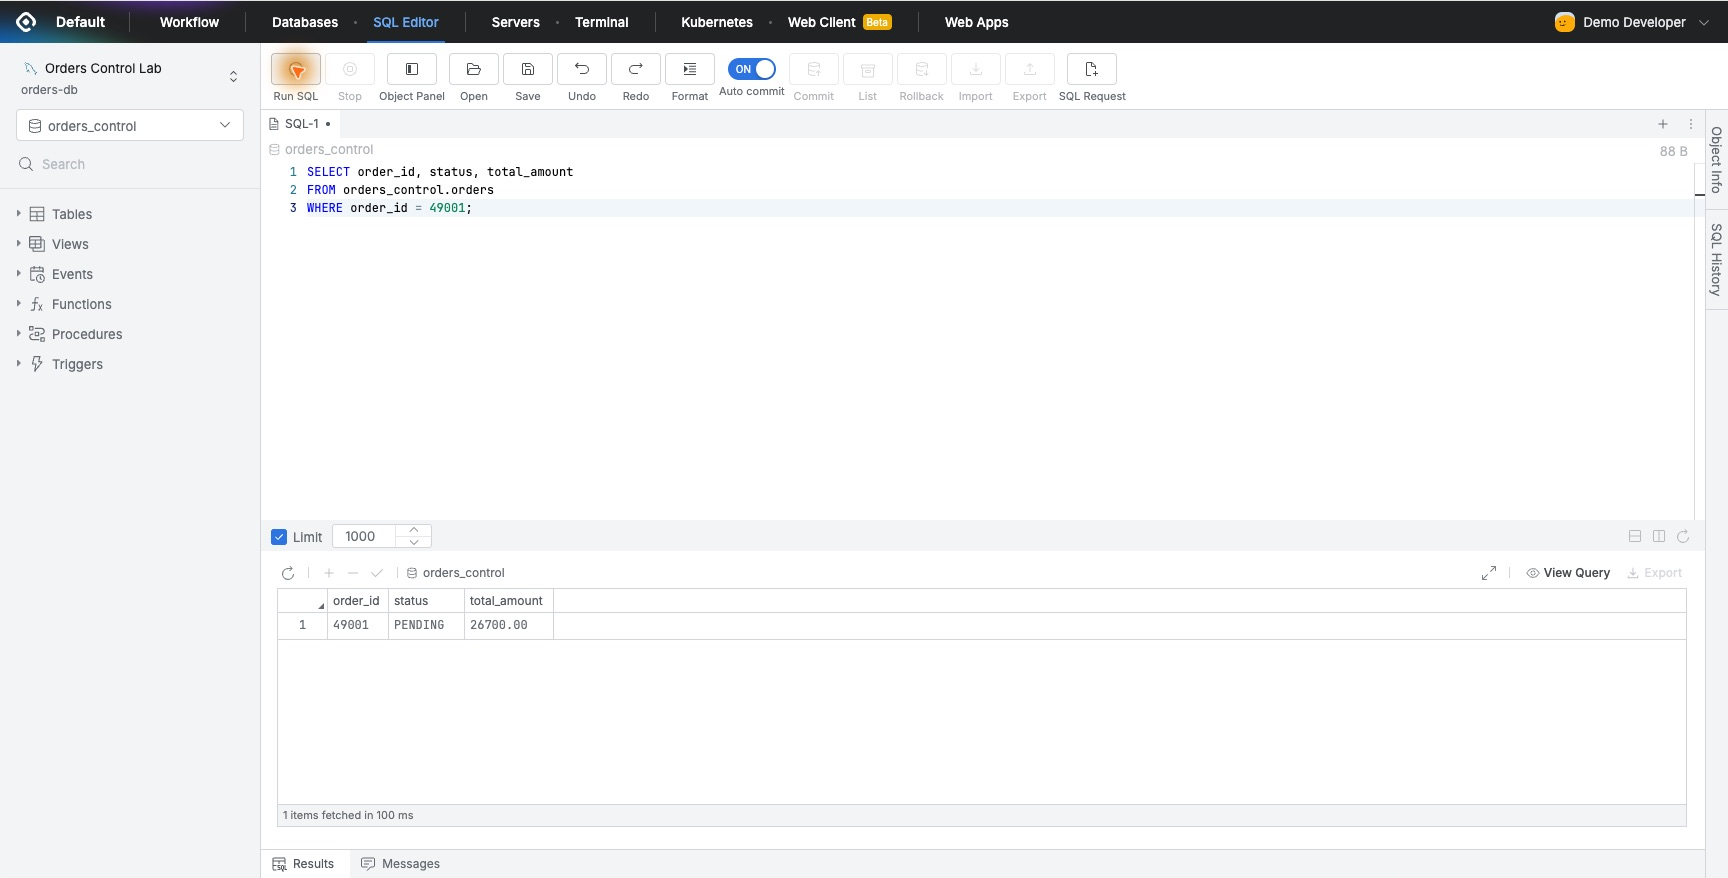
ACP Lab Notes
[Part 49] What records remain after changing a single order?
Changing a value in a production database often requires more than saying it is done. I followed one order correction through its justification, SQL approval, execution, before-and-after snapshots, and audit export.
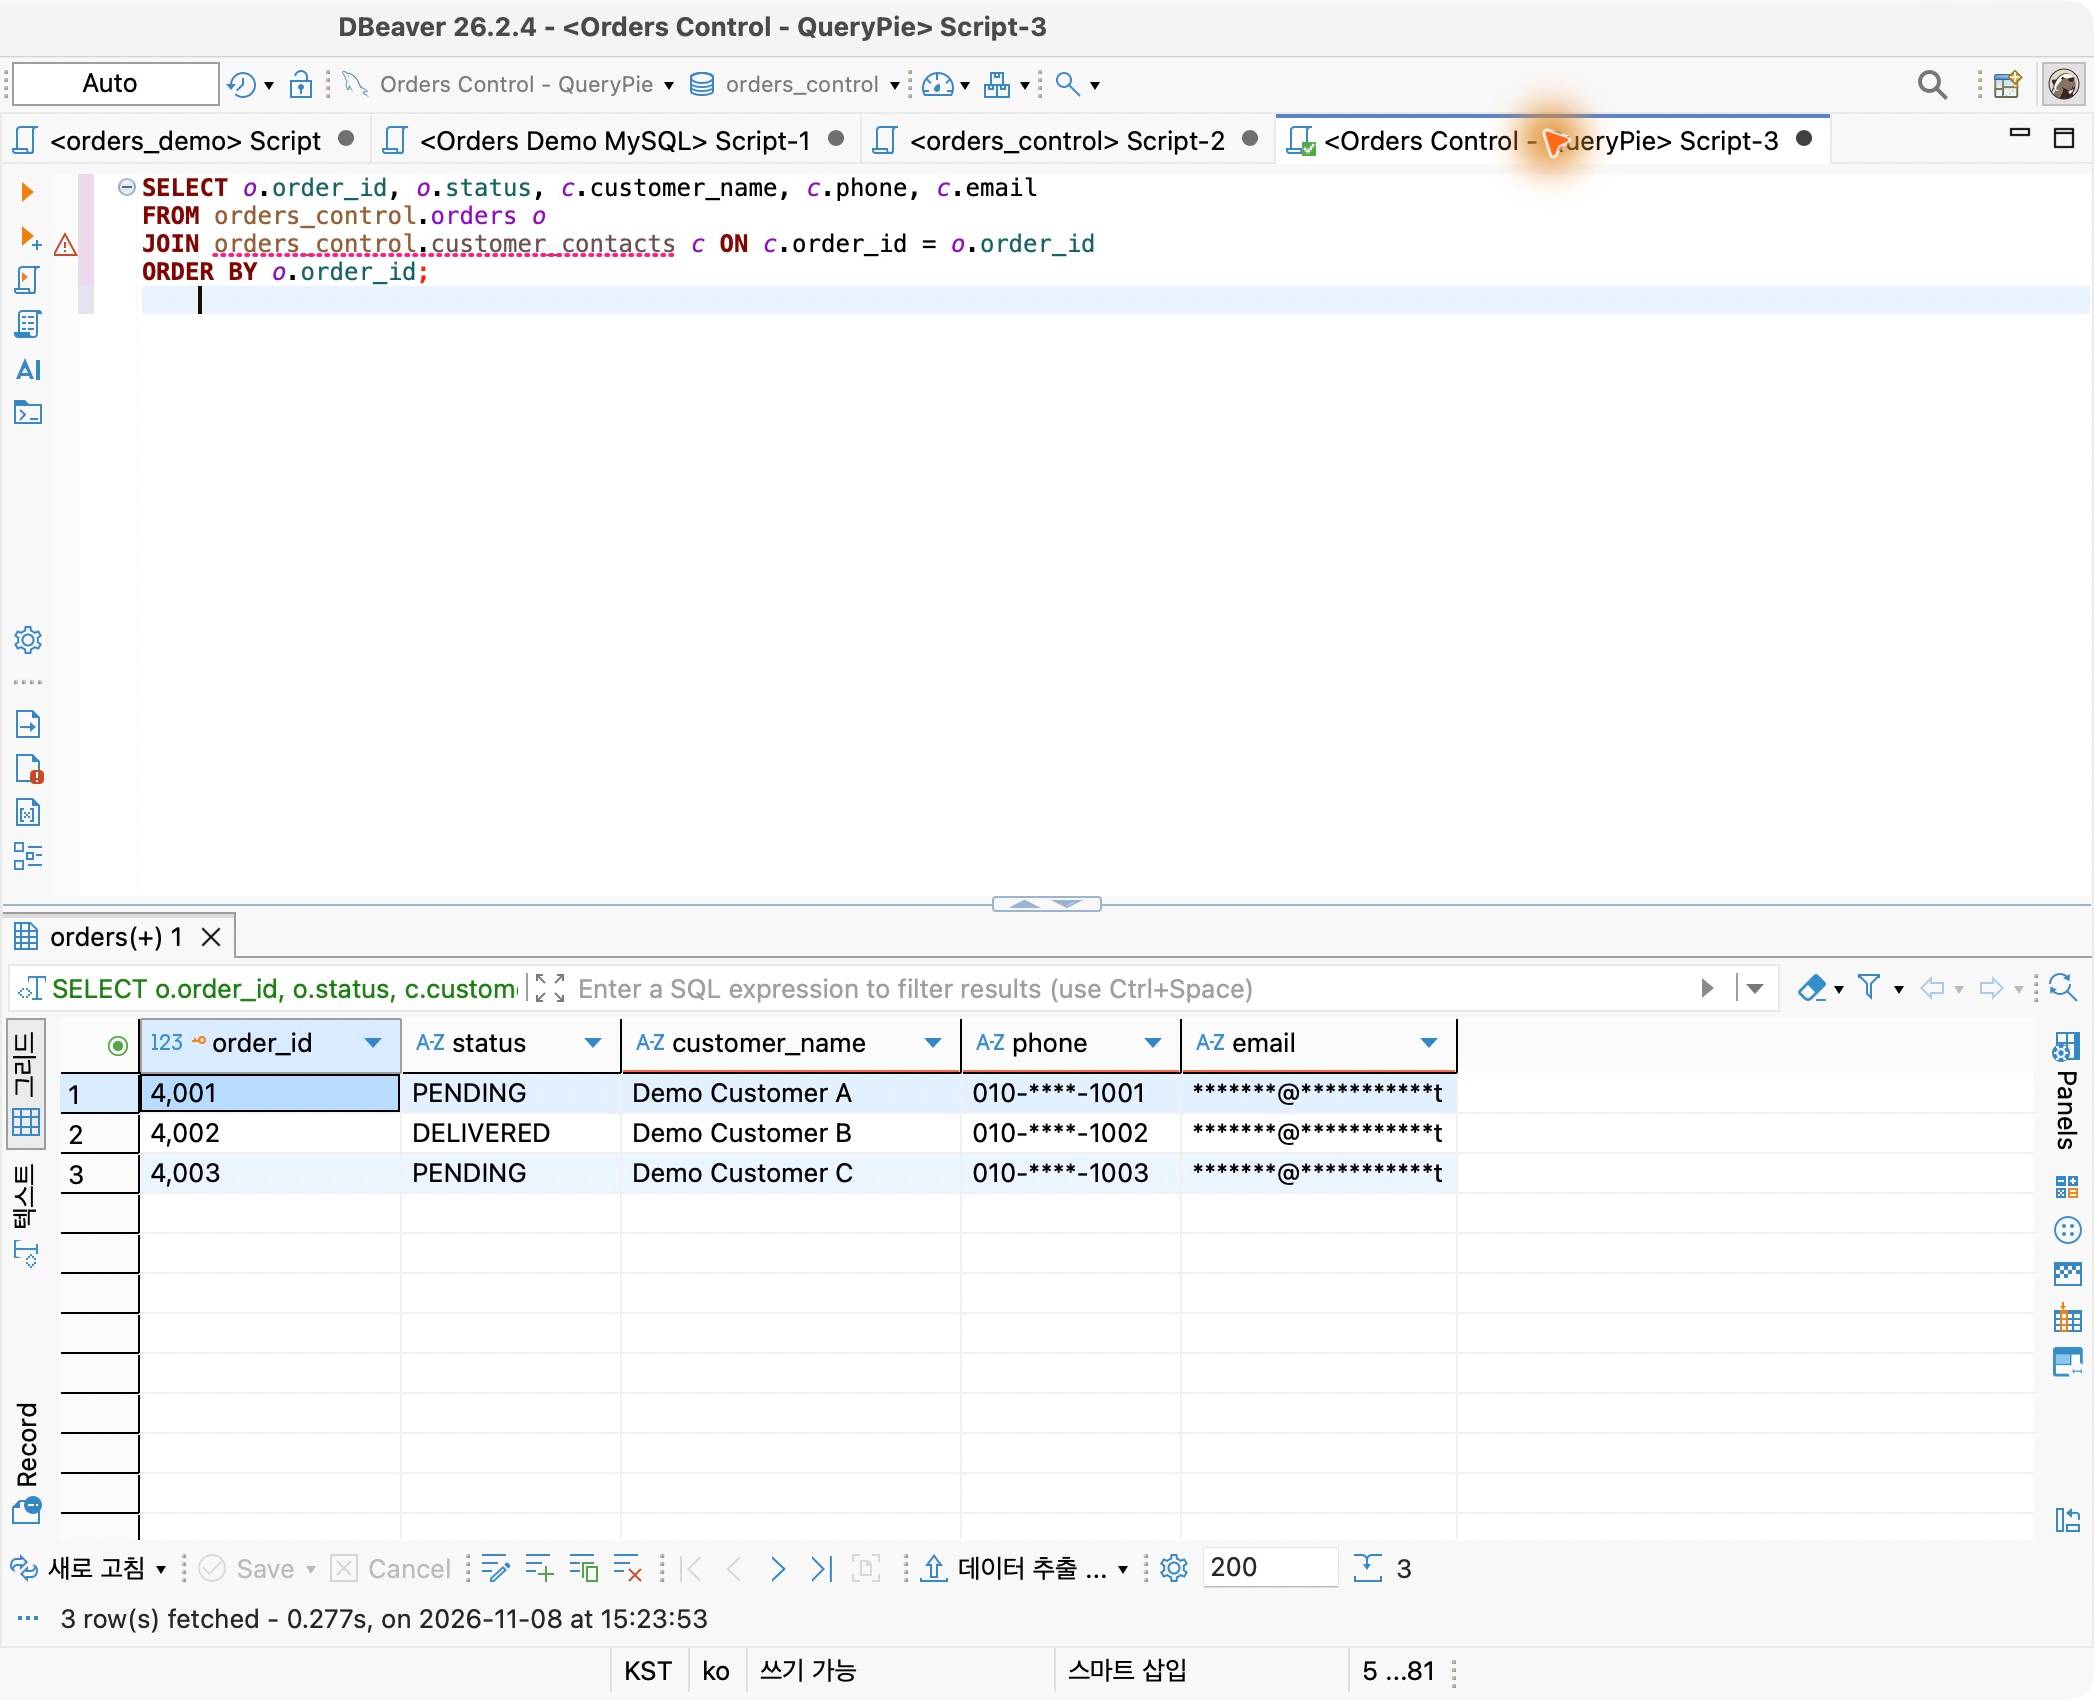
ACP Lab Notes
[Part 50] After a breach, how far can an attacker go? Reflections on the first ACP series
I began this series wondering how far an incident could spread after one account was compromised. After 50 hands-on posts covering databases, servers, and Kubernetes, I reflect on the controls I configured and the results I observed.
Stop Thinking.
Start Transforming.
